Hacker caught double-crossing Gentlemen ransomware gang, diverting victims to keep all the loot
The so-called ransomware turncoat used MCP and reverse PowerShell as part of a never-before-seen AI attack chain.
The Gentlemen dark leak site. Image by Cybernews
 Follow us
- A Russian hacker secretly hijacked The Gentlemen’s victims, cutting the ransomware gang out of its own payday.
- Exposed infrastructure revealed 50TB of data, including 6TB stolen from 24+ victims across six countries.
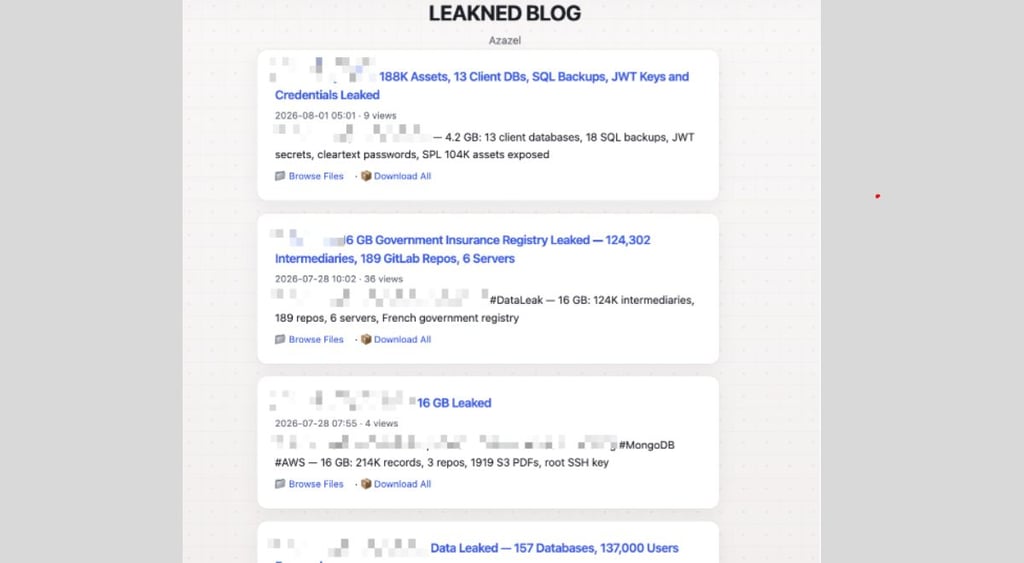
- The affiliate ran its own servers and LEAKNED extortion site, apparently behind The Gentlemen's back.
- CloudSEK uncovered what it says is the first publicly reported use of MCP as a C2 channel in a live criminal campaign.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
An affiliate of The Gentlemen ransomware group was discovered running their own operational infrastructure and leak site in parallel with the gang – all to siphon off victims and keep the extortion money for themselves.
50TB of exposed infrastructure
The Russian-speaking affiliate “Azazel” and its clandestine setup was first discovered by CloudSEK security researchers via an “exposed open directory and a misconfigured storage server” – with the threat actor completely unaware that their 50TB infrastructure had even been invaded.
One exposed server gave up an entire ransomware operation. A Gentlemen affiliate breached 2 dozen+ orgs across 6 countries via stolen CI/CD secrets, then ran attacks through an AI assistant over MCP, a technique with no prior public reporting. https://t.co/KYDy450fUM
undefined CloudSEK (@cloudsek) October 6, 2026
In a blog posted Monday, CloudSEK says Azazel was holding onto more than 2 dozen victim directories, including roughly 6TB of data stolen from victims across six countries.
In fact, CloudSEK says they were able to observe the affiliate infrastructure operating live, at one point watching "hundreds of gigabytes" of one victim's exfiltration flow seamlessly to the hacker's storage server in real time.
Victims spanned various sectors, from logistics, insurance, and AI to medical devices, pharmaceuticals, and government-adjacent infrastructure, CloudSEK said.
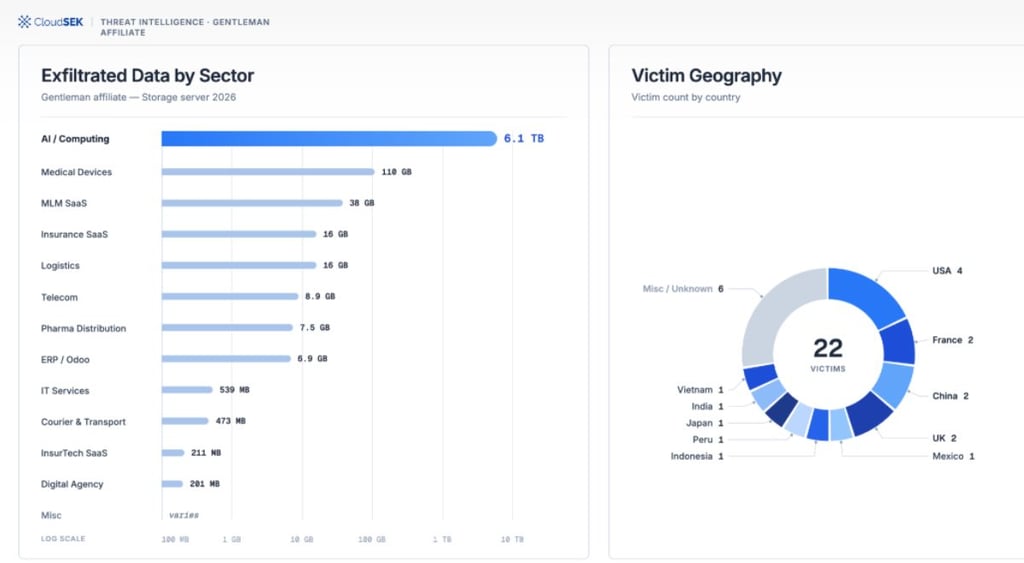
In total, researchers found more than 29TB of raw storage across two servers run by the alleged backstabber.
CloudSEK has not identified prior public reporting of a threat actor operationally using MCP exec_in_session as a C2 channel in a live criminal campaign.the CloudSEK Threat Intelligence analysis states.
This investigation documents one confirmed instance.
CloudSEK also said their researchers notified all victims before publishing their findings.
No honor among ransomware thieves
Ripping off a ransomware-as-a-service (RaaS) gang is complicated stuff, apparently.
CloudSEK says Azazel built and operated an entire ransomware ecosystem on their own, completely independent of The Gentlemen.
Azazel's extortion system included its very own branded leak site – “LEAKNED” – and, in a move that ran the gamut, also published victims' data and facilitated handsome payouts – all without the knowledge of its ransomware host, it appears.
Affiliates typically give an RaaS group a cut of their proceeds, often in exchange for permission to use that group’s infrastructure and/or signature malware to carry out attacks.
In this case, Azazel was said to have used The Gentlemen's infrastructure and tooling to compromise the organizations, then, after exfiltrating their data, contacted the victims directly – even using The Gentlemen's own communication channels – and posted them on LEAKNED.
Gentlemen,Your corporate infrastructure has been assessed and confidential data has been secured on our storage. This is not a threat it is a notification of an existing vulnerability that requires your immediate attention,Azazel's ransom note begins.
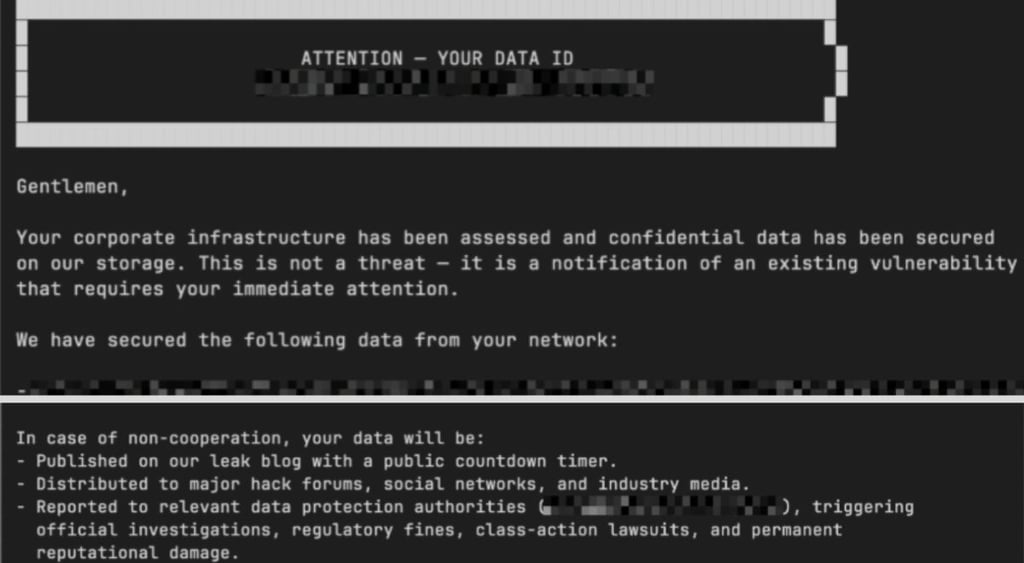
Finally, after negotiating directly with the victim, Azazel would then collect the ransom and keep the full financial haul, effectively cutting The Gentlemen out of the entire criminal process.
AI enters the affiliate playbook
From naming conventions to referencing “culturally significant Russian novels,” CloudSEK confidently believes Azazel is a Russian-speaking operator.
The operational scripts confirm it directly. Multiple shell scripts and Python files contain fluent Russian prose in their comments, not single borrowed words or transliterations, but full grammatical sentences written by someone who thinks in Russian,CloudSEK researchers say.
Still, one of the most significant findings is the discovery of what may be the first AI-powered attack chain using the Model Context Protocol (MCP) alongside reverse PowerShell to carry out attacks.
CloudSEK says the setup allowed the threat actor to connect AI tooling with malicious infrastructure, essentially turning MCP into a conduit between the AI agent and compromised systems.
Check if your data was exposed
Find out if your email and related personal information have appeared in known data breaches.
Researchers said the never-before-seen-in-the-wild technique has given them a rare glimpse into how ransomware affiliates are beginning to operationalize AI during live attacks.
CloudSEK said that although the security research community has documented MCP attack risks since 2025, until now, it “has not identified prior public reporting of a threat actor operationally using MCP exec_in_session as a C2 channel in a live criminal campaign.”