Job hunting? North Korean fake recruiters infected 30,000 devices
Be wary of attractive opportunities requiring you to download files or run code.
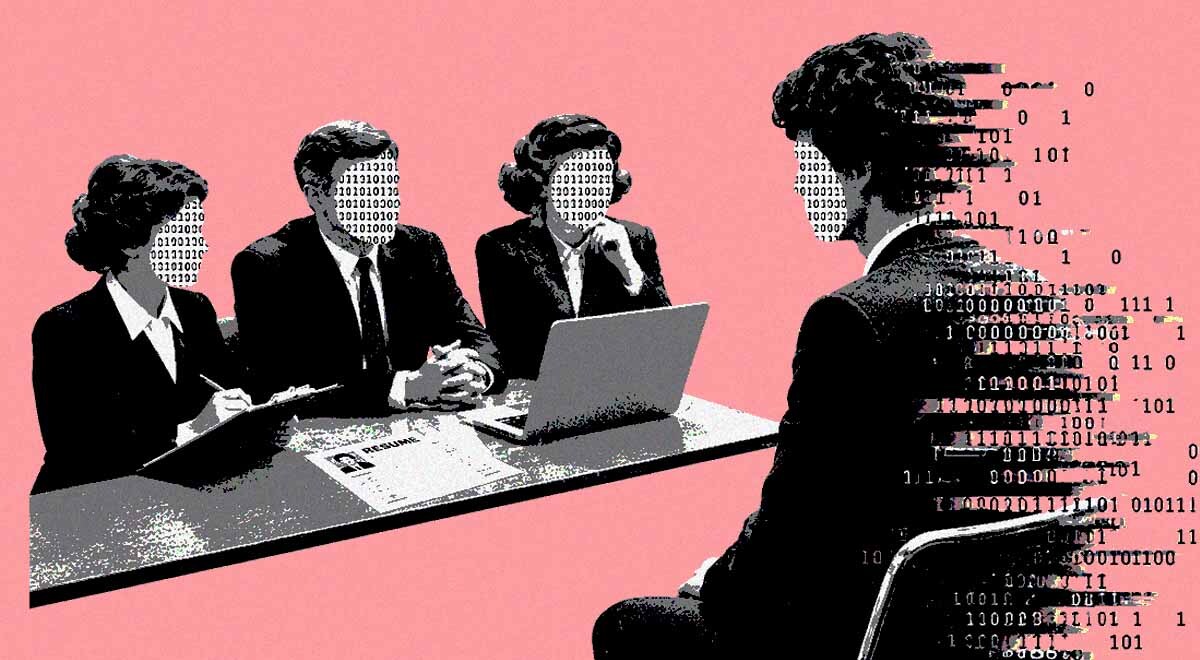
Image by Cybernews.

- WaterPlum infected more than 30,000 devices in over 100 countries through fake recruiter contacts.
- Authorities say the group compromised over 7,000 crypto wallets and stole at least $10.71 million.
- The hackers posed as employers and asked job seekers to run malicious files during fake interviews.
- Officials warn victims to disconnect compromised devices and assume sensitive data may already be stolen.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
North Korean group WaterPlum infected more than 30,000 devices across over 100 countries, compromised more than 7,000 cryptocurrency wallets, and transferred at least $10.71 million in stolen cryptocurrency to North Korea.
Japanese, US, Australian, and German authorities issued a joint advisory on the hacking group, warning that it conducts cyberattacks by infiltrating job seekers’ computer networks, harvesting sensitive information, and stealing cryptocurrency.
WaterPlum, also commonly known as Contagious Interview, targets software developers and IT professionals worldwide, with members posing as recruiters presenting attractive job opportunities.
They often impersonate legitimate employers, including AI, cryptocurrency, or NFT companies, or approach victims using recruiting services.
The scam also involves interviews and fake tasks requested as part of a technical hiring process. During the interviews, the hackers instruct job seekers to download and run malicious files hosted on developer platforms and code repositories, often under the guise of completing a coding assignment or troubleshooting a video conferencing issue, the advisory said.
WaterPlum then installs malware, including remote-access tools and information stealers, to exfiltrate sensitive data and cryptocurrency. The advisory mentions BeaverTail, InvisibleFerret, OtterCookie, OtterCandy, and StoatWaffle malware families.
The stolen data can include login credentials stored in web browsers, clipboard information, keylogs, screenshots, cryptocurrency private keys or seed phrases, as well as files stored on a PC or in shared folders, including IDs and passport scans.
“Stolen ID images can also be used by North Korean IT workers to impersonate victims and generate foreign currency,” the advisory said.
“Stolen credentials may be leveraged to exfiltrate crypto assets, personal data, trade secrets, etc., from victims' employers, clients, or contracting parties. The actors can also use stolen sensitive information for extortion.”
Investigators also noted that members use AI face-swapping software during online interviews before turning off their video due to “technical issues”.
At least $10.71 million had been stolen this way and funneled to North Korea, authorities said.
US and Japanese officials believe WaterPlum is connected to the North Korean state apparatus, specifically to the 313 Bureau of North Korea’s Department of Military Industry, which is subordinate to the Central Committee of North Korea’s ruling Workers’ Party.
The advisory warns job seekers to avoid executing code from untrusted third parties, immediately disconnect their device from the internet if they suspect it has been compromised, back up essential data, and assume that sensitive information may already have been exfiltrated if an infection is detected.
Authorities also said that, for the first time in Japan, they had successfully dismantled a “laptop farm” operated by an enabler. A laptop farm is a collection of laptops physically located in one country but operated remotely by workers from abroad. The investigation found evidence that the cyber actor group transferred several hundred million Japanese yen to foreign locations outside of Japan.
The other side of the scam
North Korean hackers are already notoriously known for the opposite recruitment scam.
The famous “traditional” scheme involves North Korean operatives using fake or stolen identities to get hired at companies – and then send their wages back to the regime, steal data, or plant malware.



Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
In August, Huntress researchers identified five suspected cases of North Korean operatives being hired as legitimate remote workers at real companies.
“These aren’t hackers breaking in. They're walking through the front door, getting onboarded, and doing the job, all while wiring their wages back to the regime,” Huntress said in a blog post at the time.
