ASOS hack – what happened to your data and should you be worried?
Separating hacker hype from real data risks.
Smartphone displaying ASOS hack notification. Image by Cybernews.
 Follow us
- ASOS confirmed unauthorized activity involving third-party communication platforms, not a proven full customer database theft.
- Security researchers found no leaked files or samples proving hackers hold ASOS customer records.
- ASOS says names and contact details may have been accessed, but passwords and payment cards were likely unaffected.
- Customers should avoid suspicious links, ignore Telegram links, check ASOS directly, and report unauthorized bank transactions.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
The ASOS hack has raised concerns about customer data, but did hackers actually steal your information? Here’s what shoppers need to know.
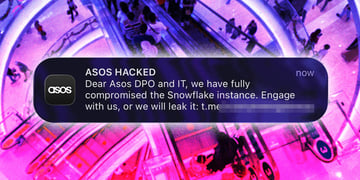
On October 6th, customers of the British brand ASOS were hit by a sinister notification claiming that hackers had “fully compromised” the digital vault, known as Snowflake, and threatened to leak customer data.
And though the notification itself didn’t prove that customer data had been stolen, it certainly felt that way for many after receiving such a jarring message.
While ASOS shared that basic personal information, including names and contact details, may have been accessed, the company does not believe that payment card information or account passwords were affected. Still, it doesn’t feel very secure.
Taking stock of the details
In such a breach, rather than panic, it’s better to separate the details into 3 layers: what is confirmed, what is possible, and what is merely claimed.
According to Anastasia Tikhonova, the global head of threat research at the cybersecurity firm Group-IB, it’s confirmed that ASOS experienced unauthorized activity involving third-party communication platforms.
What’s possible is that attackers accessed a messaging channel. What’s claimed – that attackers hold a full customer database – remains completely unverified.
There has been no confirmation that cloud data platform Snowflake has been compromised so far.
Dan Bird, a senior technology officer at cybersecurity firm Horizon3, notes that the delivery method is particularly revealing because the system used to send ASOS push notifications is separate from Snowflake.
If both claims hold up, it suggests the attackers got hold of credentials that opened more than one door,observed Dan Bird.
This raises the possibility that attackers reached multiple connected systems rather than simply breaking into one database.
Who was behind the attack?
Cybersecurity firm Group-IB tracked the Telegram group linked in the notification to a newly surfaced identity going by the name "Xuanye," which was set up on the exact same day as the hack.
Tikhonova found zero evidence, leaked files, or data samples to prove that the hackers actually hold any ASOS customer records.
In fact, the account’s history points to amateur origins rather than those of master criminals: previous activity showed the user buying and selling video game items for Roblox and CS:GO under display names such as "JohnCZ" and "Moon Transfers."
“Our analysis points to a newly surfaced identity,” said Tikhonova.
The account carried other names earlier, largely in gaming-item trading... It does not tell us who controls it, how experienced they are, or how access was gained,explained Anastasia Tikhonova.
So, did your ASOS data actually go anywhere?
The question on everyone's minds isn’t “Was ASOS hacked?” as the company has already acknowledged unauthorized activity. Instead, it’s a case of how deep the penetration was and how much of your information has left the building.
An attacker accessing an ASOS communication tool doesn’t automatically grant access to all customer databases.
Marie Wilcox, vice president of market strategy at Binalyze, describes the notification as “psychological warfare, designed to whip up panic,” in an urgent public threat aimed at getting ASOS itself to cough up, and not the customer.
And while it’s unknown exactly how many people got the alert (ASOS has 17 million customers worldwide), it is a high-profile breach.
For all the psychological pressure leveled at ASOS, the worst move from a customer's perspective would be to let their guard down. Even if your contact details haven’t been leaked today, there’s no guarantee a follow-up scam won't be launched tomorrow. We’re all familiar with fake emails or SMS pretending to be ASOS customer support.
Andrew Curtis, a chief information security officer at Australian cybersecurity firm Gadget Access, advises vigilance.
Your shopping profile can become a scammer’s script,recommended Andrew Curtis.
A hacker could theoretically sound legit if they know exactly what pair of Nikes you ordered, even if the probability of it happening seems relatively low.

Check if your data was exposed
Find out if your email and related personal information have appeared in known data breaches.
What should ASOS customers do right now?
The immediate and obvious threat at large is phishing. The UK National Cyber Security Centre (NCSC) advises customers to assume they’ve been affected.
The best reactive measures are to remain alert for suspicious messages and avoid clicking unknown links.
Bird warns against clicking so-called follow-up emails from ASOS, and as tempting as it may be, do not open any Telegram links.
Curtis, meanwhile, advises shoppers to visit the ASOS website to monitor important updates and contact their bank immediately if they encounter any unauthorized transactions.