Rogue VPN files can let hackers hijack ASUS routers
Vendor doesn't say whether router flaws have been exploited in the wild.
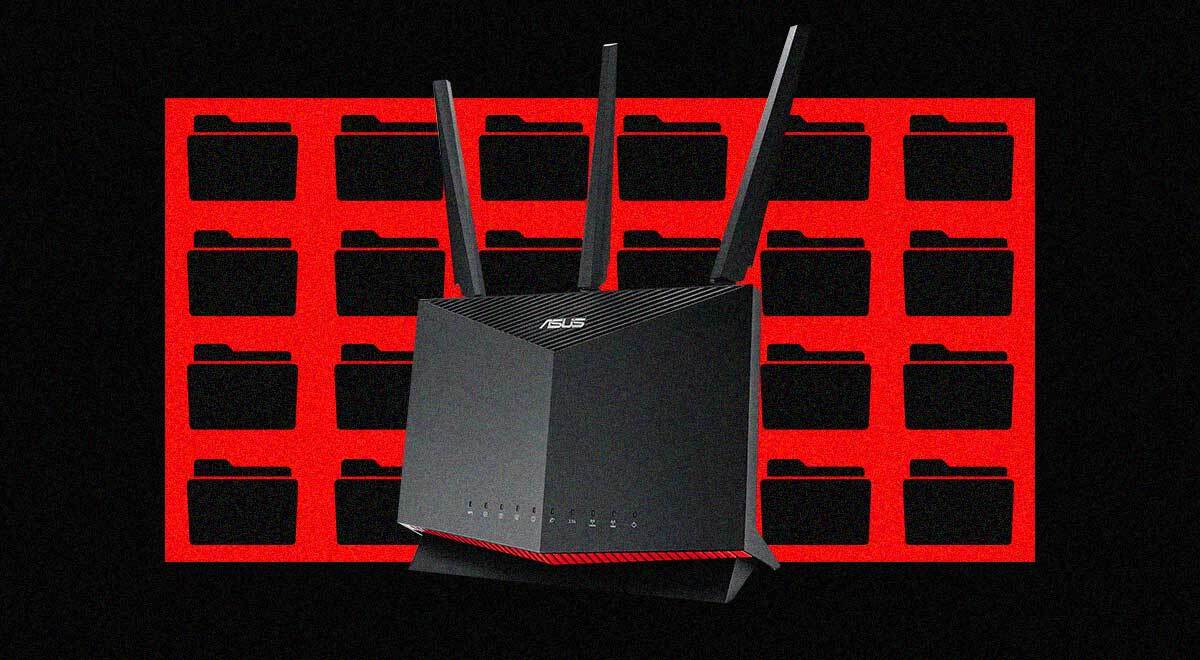
Image by Cybernews
 Follow us
- ASUS patched a critical router flaw that lets logged-in attackers run commands through malicious VPN files.
- The most serious issue affects routers using the ASUS 3.0.0.6_102 firmware series.
- ASUS says owners should install the latest firmware and avoid VPN files from unknown sources.
- ASUS has not said whether attackers have exploited the router flaws in real attacks.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
ASUS has rolled out an urgent security update for its routers after a critical VPN flaw exposed them to malicious attacks.
The flaw is in the router's web admin interface. A logged-in attacker could upload a malicious VPN file to run commands on the device, ASUS warns.
Tracked as CVE-2026-14157, ASUS rates the flaw as critical with a severity score of 9.4 out of 10.
It affects routers running ASUS firmware from the 3.0.0.6_102 series.

The risk is highest for people who import VPN client files.
The Taiwanese firm’s advisory warns owners not to import files shared online or obtained from unknown sources, and to avoid files they can’t verify.
The fix is to update the router
ASUS urges owners to install the latest firmware available for their model. Until then, they should only import VPN files from sources they trust.
ASUS also patched CVE-2026-13313, another router flaw rated 8.9 out of 10. It affects the 3.0.0.4_386 series, 3.0.0.4_388 series, and 3.0.0.6_102 firmware series.
An authenticated remote attacker could exploit the flaw to run commands with higher privileges.
The vendor advises users to protect their router with a strong, unique admin password, avoid untrusted scripts, tools and commands on devices connected to their home network.
Attackers may use social engineering to trick administrators into executing crafted commands that interact with the router's administration interface,warns ASUS advisory, issued October 1st.
Neither router advisory says whether attackers have exploited the flaws in the wild.
ASUS also fixed a third vulnerability, CVE-2026-93495, affecting 13 motherboard models.
Rated 7.0, the flaw requires physical access and a specially crafted device.
ASUS said owners should install the BIOS version listed for their model.
Why attack a router?
Routers have become a useful target for hackers because they sit between users and the internet.
Last year, a suspected Chinese cyber espionage campaign hijacked more than 50,000 ASUS home routers. The attackers exploited known bugs in older and unsupported devices.
The compromised routers became part of a covert network used to hide the source of malicious traffic.