Leaked GitHub key left lead US public health agency’s code exposed to poisoning
Hundreds of breached GitHub app keys still work.
- A leaked GitHub private key may have exposed CDC-linked private code and Azure cloud systems.
- GitGuardian says the key stayed usable from April 2025 until it was revoked in September.
- Researchers found 474 leaked GitHub App keys still worked, including some with write or admin access.
- GitGuardian recommends deleting unused keys and rotating any keys that may have been compromised.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
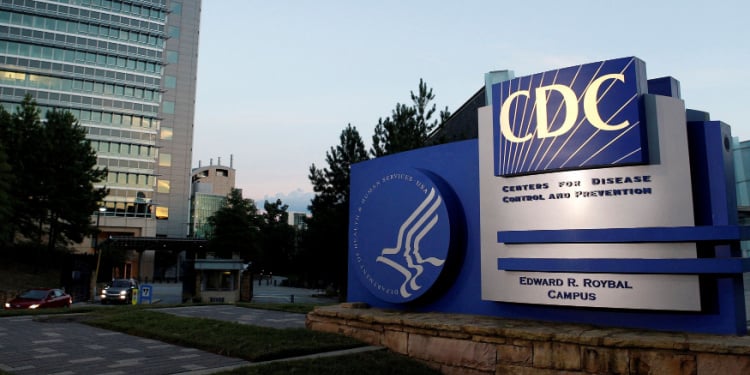
A leaked key may have exposed private code linked to the Centers for Disease Control and Prevention (CDC), potentially allowing attackers to alter software and gain access to its cloud systems.
The credential was exposed in April 2025 and remained usable until this month, according to research published by security company GitGuardian.
CDC is the main US agency for public health and infectious disease outbreak preparedness and response, charged with detecting and responding to disease threats in the US and overseas.
It is not known whether the exposed key was ever used by an attacker, and no breach tied to it has been publicly confirmed.
GitGuardian claimed the leaked credential was tied to a private GitHub app that could access CDC-linked repositories, including "cfa-cdcgov-actions", which appeared to link the agency’s main code repositories with its Microsoft Azure cloud environment.
Notably, the app had write permissions, according to GitGuardian researcher Gaetan Ferry’s report, so the leaked private key could have allowed someone to change code in those repos as well as to snoop around inside them.
“The app has write access. It can therefore poison the code stored in them,”– writes GitGuardian researcher Gaetan Ferry.
Although Ferry did not access the private repository itself, he said GitGuardian’s analysis suggested the credential could have been used to execute arbitrary code within the CDC’s Azure environment.
The security firm reported the issue through the Department of Health and Human Services vulnerability disclosure portal on September 4th and received an acknowledgement five days later.
The credential was revoked on September 18th after repeated follow ups, GitGuardian said.
Lesser known attack vector
The findings were part of a wider investigation against a backdrop of software supply-chain attacks involving ecosystems including npm, PyPI, Rust and GitHub.
GitGuardian describes GitHub Apps as a “lesser explored vector” despite their potential to hold powerful permissions across entire organizations.



Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
In order to “see what happens when their private keys fall into the wrong hands” researchers examined more than 500,000 publicly leaked RSA private keys from its dataset and identified 4,802 associated with GitHub Apps.
Of those almost 10% (474) still worked and more than 200 could modify repository contents and 44 held organization-admin privileges.
As Ferry notes, the longevity of such exposures is significant because GitHub private keys do not automatically expire. Often someone has to go in and manually delete them.
“A key committed by mistake in 2020 can still be authenticated today, long after the mistake is forgotten,” Ferry warns.
Whose problem?
GitGuardian recommends deleting unused keys and rotating any key that may have been compromised.
Yet it adds that part of the issue is ownership. Many exposed GitHub app keys, the firm said, belong to internal automation, CI bots and one-off tools that keep running long after the people or projects behind them have moved on.
The app keeps running. The keys keep working. Nobody is watching it,– warns GitGuardian researcher Gaetan Ferry.
Yet revoking those keys may not be straightforward, because some may support live software, production systems or deployment pipelines.