Hacked by email: attackers exploiting critical zero-day in Cisco’s secure email solution
An email security solution that filters malicious messages was bypassed by an email containing injected SQL code.
Image by Cybernews.
- Cisco confirmed attackers exploited a critical zero-day flaw in its email security products.
- The bug lets remote attackers gain root privileges by sending emails with malicious SQL statements.
- Cisco says it has secured affected cloud systems and contacted customers with possible compromise signs.
- Admins should install Cisco’s emergency update, review logs, and renew credentials.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Attackers have breached Cisco’s email security product using malicious SQL statements in emails. The US network technology giant disclosed a critical, actively exploited zero-day vulnerability: remote attackers can acquire root privileges without any authentication.
Cisco has identified a critical zero-day SQL injection vulnerability affecting its email security product and confirmed that attackers have already breached an undisclosed number of cloud instances.
Many organizations use Cisco’s Secure Email Cloud or on-premises gateway devices to protect against phishing, ransomware, spam, and business email compromise (BEC).
The severity of the flaw is nearly as bad as it gets – 9.8 out of 10 according to the CVSS (Common Vulnerability Scoring System) score.


Hackers can exploit it remotely over a network; the attack complexity is low and requires no user interaction, no privileges, not even an account. A successful exploitation of the bug, tracked as CVE-2026-76461, grants the attacker substantial access to sensitive information.
Cisco says it detected malicious activity and has since secured its cloud infrastructure.



Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
“Cisco has directly contacted customers who own Cisco Secure Email Cloud devices where indicators of possible compromise were identified. Cisco is engaged in remediation and recovery operations. Cisco has already deployed mitigations that are within Cisco's management,” the company’s security advisory reads.
Affected customers are strongly recommended to restore a device to a secure configuration by renewing credentials and any cryptographic materials installed on the device. Cisco also urges restricting access and implementing robust access control.
Cisco also released an emergency software update for both virtual and physical Cisco Secure Email Gateway appliances. There are no other workarounds, and Cisco is urging immediate installation of the fixed software.
The Cybersecurity and Infrastructure Security Agency (CISA) promptly included the bug in its Known Exploited Vulnerabilities (KEV) catalog, giving federal agencies three days, until September 17th, to apply mitigations.
How do attackers leverage the bug?
The SQL injection bug in Cisco AsyncOS software for Cisco Secure Email Gateway is caused by insufficient validation in the email parsing logic.
Hackers can send specifically crafted emails containing malicious SQL statements that are then executed, leading to command execution with root privileges on the underlying operating system.
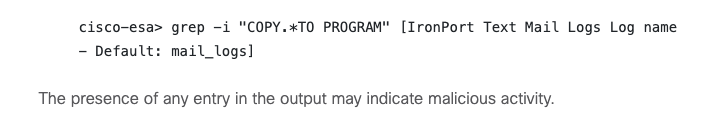
The advisory already contains indicators of compromise – malicious SQL statements that could be detected in the logs. Admins are advised to review the mail logs.
However, because attackers have root access, they might wipe their footsteps.
“Cisco strongly recommends that administrators cross-check the network logs and the firewall logs outside of the impacted device to identify any potential suspicious activity, including but not limited to unexpected uploads that were initiated from the affected device to external IP addresses or downloads from malicious IP addresses,” the advisory reads.
The company’s additional recommendations include keeping the appliances off the public internet, restricting access to known trusted hosts, separating mail and management functionality onto individual network interfaces, placing the appliances behind firewalls, monitoring traffic, disabling HTTP, FTP, and other network services that are not required, among other things.