Attackers target GitLab: thousands of exposed servers remain vulnerable to a critical bug
Twelve public exploit repositories have been discovered.

Image by Shutterstock.
- Hackers are actively stealing secrets from vulnerable GitLab instances.
- Exposed secrets can include credentials for cloud accounts, container registries, and source code repositories.
- Public scans found 86,231 exposed GitLab servers, and thousands of them remain vulnerable.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Hackers are actively exfiltrating secrets from GitLab instances potentially containing credentials for cloud accounts, container registries, and repositories. Public scans reveal over 86,231 exposed servers, and thousands of them remain vulnerable.
Threat intelligence platform Censys found at least 12 distinct public repositories with exploit code targeting unpatched GitLab Community Edition and Enterprise Editions, leveraging recently unveiled critical vulnerabilities.
The maximum-severity GitLab flaw, tracked as CVE-2026-85706, is actively exploited by threat actors – the US Cybersecurity and Infrastructure Security Agency (CISA) alerted federal agencies on September 11th, setting a three-day deadline to implement mitigation measures.
GitLab is a self-hosted software forge platform that allows collaboration across software development, security, and IT operations (DevSecOps), used by more than 50 million registered users and half of the Fortune 100 companies, according to an SEC filing.

Organizations use GitLab both as a workshop and a secure vault, storing source code for internal projects, automation scripts, security policies, and more.
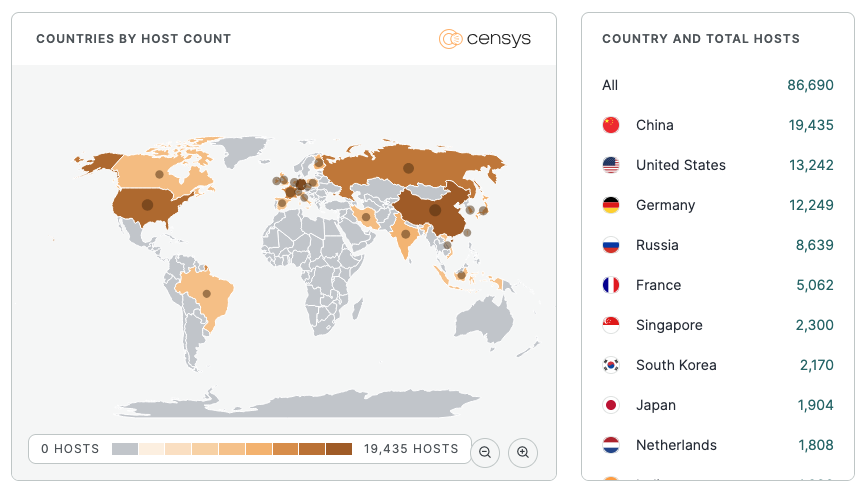
Censys’s scans also found over 86,000 exposed hosts running GitLab – a total of 208,186 web properties. Most of them are in China (19,435), followed by the US (13,242), Germany (12,249), Russia (8,639), France (5,062), and other countries.
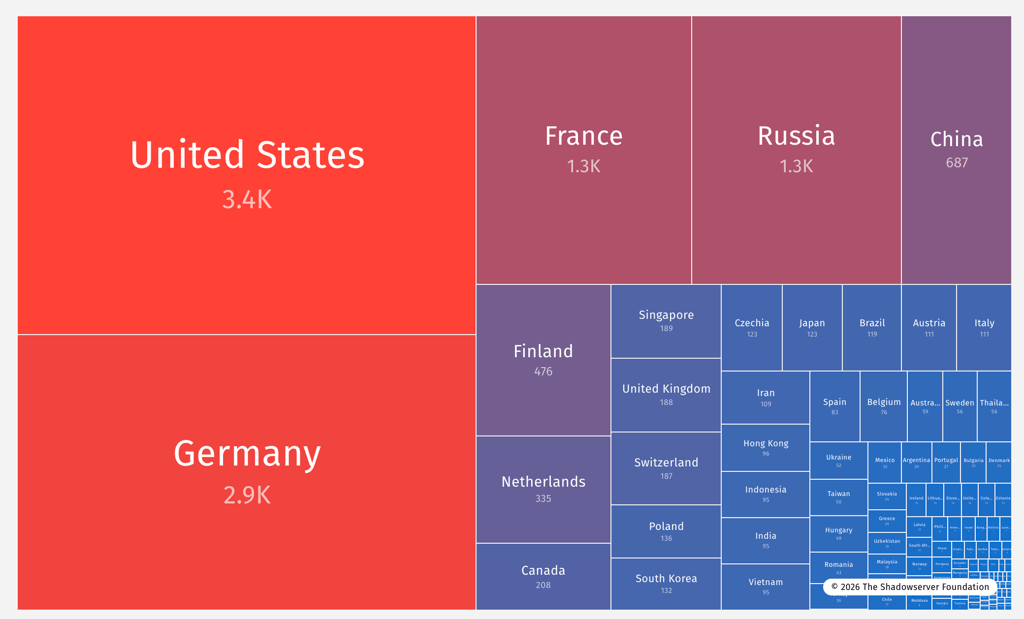
ShadowServer Foundation’s data suggests that at least 13,700 of the exposed servers remain vulnerable to CVE-2026-85706, with most in the US.
The critical bug is a path traversal vulnerability that allows unauthenticated attackers “under certain conditions” to read arbitrary files.
“Public exploit code demonstrates reading /etc/gitlab/gitlab-secrets.json, which holds the keys GitLab uses to encrypt secrets it stores, such as CI/CD variables, deploy keys, and integration tokens,” Censys warns in the report.



Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
These credentials, used by the pipelines, potentially expose cloud accounts, container registries, and repositories they authenticate to.
Any credentials stored in vulnerable instances accessible from the internet should be treated as potentially compromised.
Censys urges rotating them and reviewing the instance for any signs of potential compromise. Attackers can quickly escalate stolen credentials to even larger supply chain compromises.
GitLab earlier issued a critical patch release that fixed 18 security vulnerabilities, including two critical ones, and strongly recommends updating all self-managed GitLab installations to the latest versions: 19.3.2, 19.2.6, and 19.1.8.
It’s the second time in less than a month that GitLab has been found to be critically vulnerable to unauthenticated attackers. GitLab disclosed a critical GraphQL flaw on August 17th, and less than 24 hours later, attackers were already abusing it to modify or delete public projects and user data.