Hackers crack Samsung Galaxy S26 with single email in zero-day attack
The issue may also affect Google’s Pixel 10.
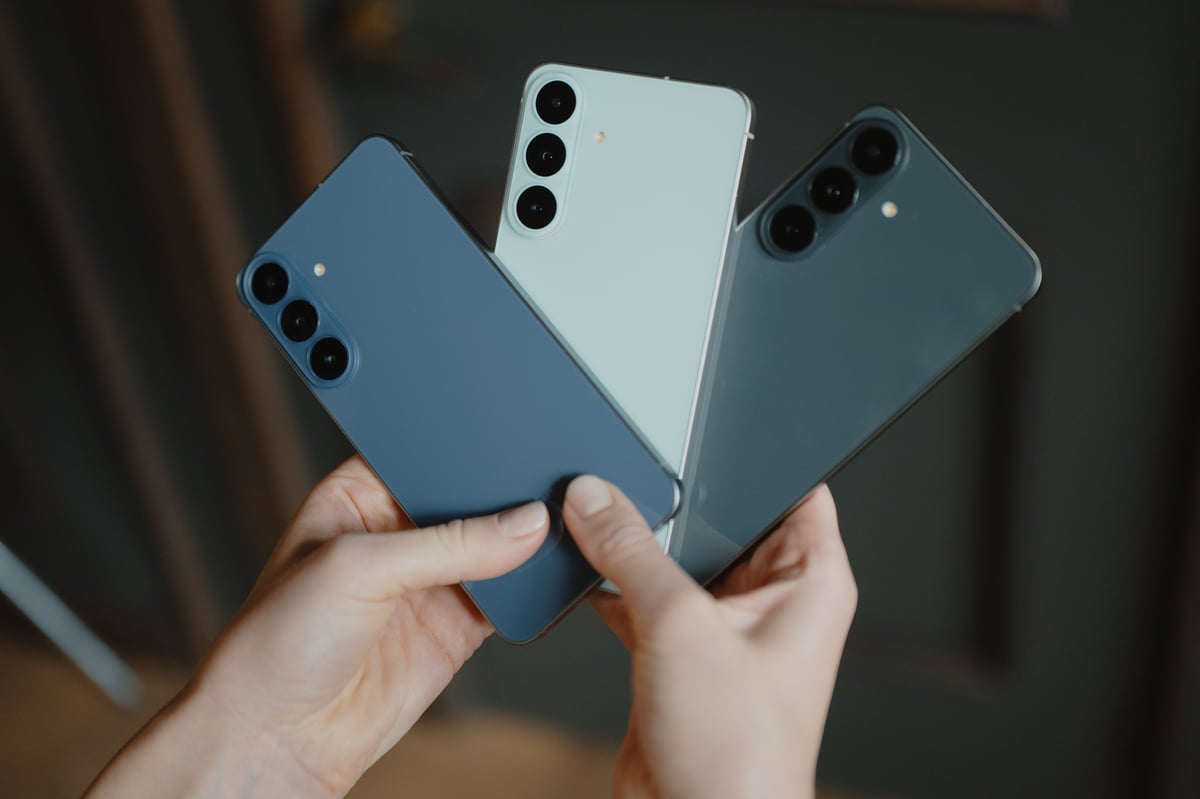
Samsung Galaxy S26 FE comes in three diferent colors. Image by Gabrielius Jauniškis
 Follow us
- Ikotas remotely ran code on a Samsung Galaxy S26 at Pwn2Own Ireland 2026 using one email.
- The attack chained four flaws; Samsung already knew about one before the demonstration.
- Researchers say the previously unknown flaw may also affect Google’s Pixel 10, but details remain unpublished.
- Pwn2Own showed three successful Galaxy S26 attacks involving five apparently new flaws.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Bug hunters say they’ve found a way to hijack a Samsung Galaxy S26 completely – just by sending it a single email.
The flaw lets security researchers at Ikotas Labs run their own code on the phone remotely, and they also have a second, unpublished trick that digs even deeper into the device.
Ikotas, a Japanese security company, successfully hacked the Galaxy S26 remotely on Tuesday at Pwn2Own Ireland 2026, an event run by Trend Micro's Zero Day Initiative (ZDI).
The remote compromise used a chain of 4 vulnerabilities, only 1 of which was already known to Samsung, which landed Ikotas an $11K reward at the event.
“We have successfully executed remote code on the Samsung Galaxy S26,” Ikotas posted on X, following its demonstration.
“While we received a $11,000 bounty, the joy of demonstrating our technical prowess on the global stage is even greater.”
In total, the event demonstrated 3 successful attacks on the Galaxy S26 involving 5 apparently new flaws.
Viettel Cyber Security's Nguyen Thanh Dat used 4 bugs, 3 of which were already known to Samsung, while Interrupt Labs used another 4-bug chain containing 3 collisions (bugs already found by others) and 1 zero-day.
The flaw may also affect Google’s Pixel 10
Ahead of the competition – which sees elite ethical hackers compete for cash prizes for attacks on mobile phones, smart home devices, printers, and coding agents – Ikotas said the zero-day it discovered affected both Samsung and Google’s flagship phones.

It's a zero-day that allows RCE [remote code execution] on the latest versions of Google Pixel 10 (probably works on 11 too) and Samsung Galaxy S26 with just sending 1 email,Ikotas CEO Satoki Tsuji said in an X post, dated October 1st.
“There's also a chain that enables LPE [local privilege escalation] afterward. Actually, I've discovered multiple RCE methods for each device, and I plan to report all of them to the vendors," he added.
According to the ZDI’s schedule, Ikotas is due to attempt a remote compromise of the Pixel 10 on Thursday (October 8th).
Law enforcement use case
In a post dated October 1st, Ikotas Labs suggested another use case for the flaw: offensive hacking. This echoes growing demand for tools that let police crack locked phones in criminal probes, as seen with Cellebrite's tool which cracked Trump’s shooter’s phone in 40 minutes, following his assassination attempt in 2024.
It also aligns with Japan’s push for "hack back" powers letting state agencies disable hostile servers and devices.

As Ikotas puts it in a post dated October 1st, "Amid growing demands for the adoption of remote smartphone analysis techniques in criminal investigations, we will showcase that a domestic company is technically capable of achieving this."
ZDI has not yet published CVEs, affected components, or technical details for any of the new flaws demonstrated at the event, meaning their severity ratings are not yet known.
Further Galaxy S26 hacking attempts were scheduled for Wednesday, so more bugs may be revealed as Pwn2Own Ireland continues.