Cyberattack on Japanese cloud firm hits railways, police and food suppliers, 495 organizations exposed
Ransomware tears through country's infrastructure via SoftBank-owned cloud service.
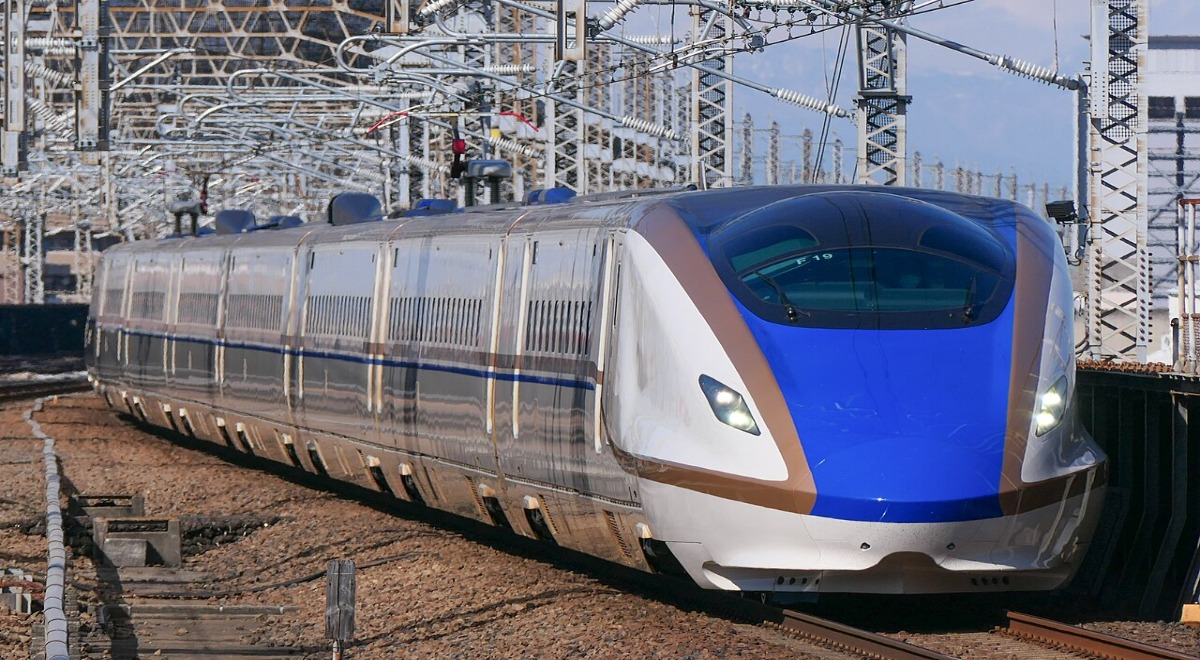
JR East E7 series. Source: CC BY-SA
 Follow us
- IDCF Cloud says 495 companies and local government services were affected by the cyberattack.
- Four cloud zones were badly damaged, and some customers may need to restore data from their own backups.
- JR East and View Card say up to 6.09 million records may have been accessed through cloud services.
- The fallout has disrupted services tied to railways, police, food logistics, travel, karaoke, and e-commerce.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Railways, police services, food logistics and even a Japanese girl band’s fan service have been caught up in a huge ransomware attack on Japanese cloud provider IDC Frontier, with some customers warned their data may be impossible to recover.
IDC Frontier (IDCF) Cloud – owned by Open AI investor SoftBank – is one of the main domestic alternatives to AWS, Microsoft Azure and Google Cloud, aimed at companies and public bodies that want their systems run on sovereign turf.
An attack on just one of its regions could impact hundreds of companies, thousands of virtual servers, and tens of millions of users of those services.
In a statement issued on Wednesday, IDCF Cloud said 495 companies and local government services had been affected by the attack, creating a sprawling cloud supply chain crisis across the country.
IDC Frontier said the breach took place in the early hours of Wednesday, knocking some of its servers offline.
In an update published Thursday, the cloud provider confirmed that four cloud zones had been so badly damaged that customers would need to rebuild their systems elsewhere and restore data from their own backups.
“We are working to identify the detailed cause and investigate the scope of the impact, but it is expected that it will be difficult to retrieve or restore customer data stored in a part of East Japan Region 1,” it said.
At this time, our view is that data restoration will only be possible from backup data held by the customer themselves,says IDC Frontier in customer update on October 8th, following cyberattack.
In 7 minutes hackers encrypted 3.6 petabytes of data
IDC Frontier has not said how the attackers got in, who was responsible, whether they demanded money, or how much information was stolen rather than just encrypted.
Meanwhile, screenshots claiming to be from the attackers, have been circulating on social media showing messages stating: “Your Cloud is Ours.”
The messages claim they accessed 239 systems that run virtual machines, locked 225 large storage systems holding 3.6 petabytes of data, sealed more than 16,600 virtual machine hard drives, and deleted 554,153 backup snapshots.
The threat actor claims the attack took just 7 minutes.
When Cybernews’ research team checked the cloud console displayed in the screenshot, it was inaccessible, while the ransom note does not include any self attribution to any known ransomware group.
Millions of railway customers potentially exposed
Japan’s largest railway operator, JR East, and credit-card company View Card confirm up to 6.09 million records may have been accessed through email-delivery services using IDCF Cloud, while JR Kyushu reported 1.3 million emails.
Both say credit card numbers, home addresses and telephone numbers were not exposed.
The disruption may also have hit Japan’s physical supply chain.
Frozen-food warehouse operator Nissui Logistics has reportedly suffered a systems outage preventing it from receiving and shipping goods.
Food supply chains under attack
Nissui operates 17 cold storage and distribution centers with around 400,000 tonnes of capacity, serving supply chains involving manufacturers, retailers, wholesalers, shops and restaurants.
Japan Cyber Watch reports that other organizations thought to have been caught in the fallout include:
- Ibaraki Prefectural Police
- News agency Jiji Press
- Credit card company View Card
- Messaging app for the Japanese girl band SKE48
- Travel booking adventure company Skyticket
- Karaoke operator Daiichikosho
- E-commerce platform FutureShop
Only a handful of firms have gone public so far, and more customer data breaches are likely to be disclosed as companies investigate their exposure.
Meanwhile on Friday the National Cybersecurity Office, set up last year to guard against such attacks, sent the instructions to government ministries, which will distribute them to local public bodies and private companies.
"This is no longer just a problem for the information systems department,” it warned, urging organizations to carry out basic cyber security hygiene such as ensuring updated security protections, using strong passwords and tightening cybersecurity guards throughout supply chains.
The office also warned that AI was is making vulnerabilities increasingly complex.