Nvidia monitoring bug could have knocked AI offline
It could’ve allowed attackers to crash monitoring and potentially disrupt AI workloads without authentication.
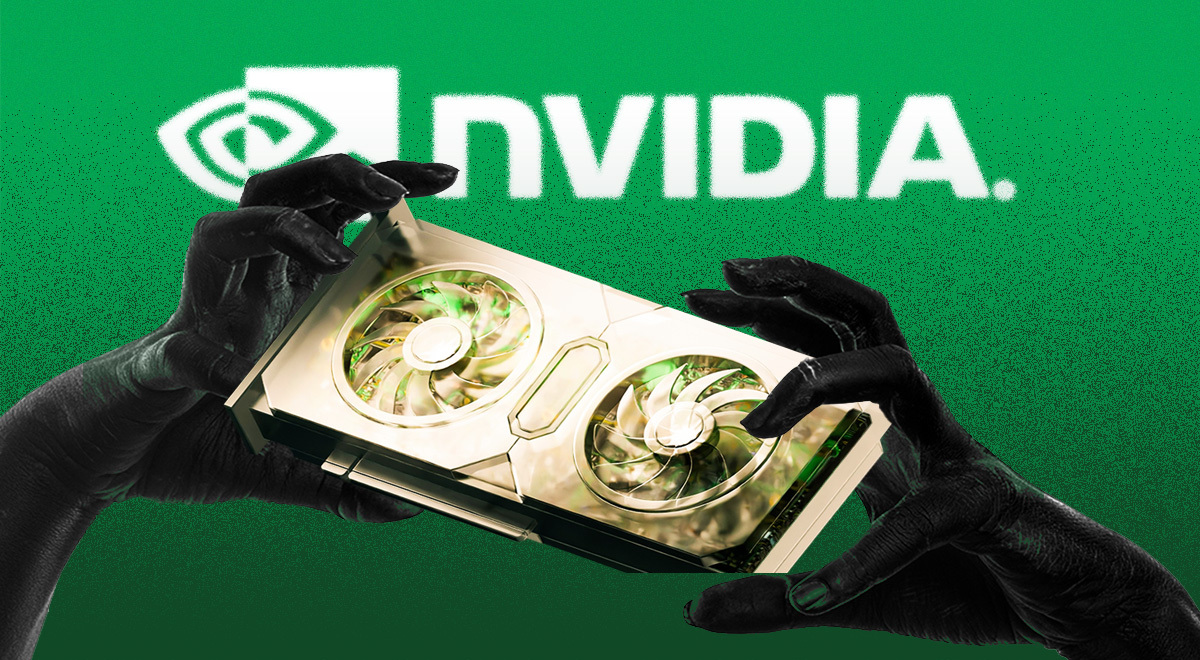
Researchers unveiled Nvidia GPU exploit. Image by Cybernews.
 Follow us
- Researchers found more than 2,000 GPU servers exposed Nvidia’s DCGM Exporter online without authentication.
- The flaw let unauthenticated attackers crash the monitoring service and potentially disrupt AI workloads.
- Exposed systems covered about 300 organizations and represented around $100 million in hardware.
- Nvidia confirmed the issue and released a fix for the high-severity flaw.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Thousands of GPU servers left Nvidia’s monitoring tool open to the internet, and hundreds were at risk from a serious flaw that let hackers crash it remotely – no login required – potentially knocking AI workloads offline.
The tool, called DCGM Exporter, reads telemetry from the GPUs on a host, including hardware information, memory usage and utilization, power consumption, and error events.
In Nvidia’s case, researchers from cybersecurity company Lava discovered a high-severity bug that allowed an unauthenticated attacker to trigger uncontrolled resource consumption on the GPU server, leading to denial of service and information disclosure.
By exhausting the exporter’s resources, an attacker could crash the monitoring service, blind operators to GPU health and activity, and potentially slow workloads running on the same host, the company said.
The scale of the exposure is impressive. In a blog post detailing their research, Lava researchers said they found more than 2,000 GPU servers exposing Nvidia’s DCGM Exporter directly to the web without authentication.
“The exposed systems included Nvidia Blackwell Ultra B300 GPUs, H200s and H100s used for large-scale AI workloads, as well as consumer RTX 5090 and 4090 systems,” said the researchers.
“Anyone who could reach these endpoints could see what hardware organizations were running, how heavily it was being used, and details about the AI infrastructure around it.”
Together, these exposed GPUs represented around $100 million in hardware and belonged to about 300 organizations, nearly half of them located in the US.
“Neoclouds are racing to add GPU capacity, and customers are racing to use it,” said Yakir Kadkoda, CTO and Co-Founder at Lava.
“That speed is creating security gaps on both sides - providers are moving faster than they can harden the environment, while customers often don’t know exactly what they’re inheriting or exposing.”
Lava reported the issue to Nvidia. The chip giant agreed the problem was indeed real and soon released a fix for the flaw, tracked as CVE-2026-47483. It's been given a 8.2 CVSS high-severity rating.
“The findings highlight a growing security gap in AI infrastructure: companies are spending millions on GPUs while leaving critical systems exposed,” Lava wrote.
“Those exposures can reveal how AI environments are built and, in some cases, allow attackers to disrupt them.”