Trump Mobile hackers threaten T-Mobile: “You're in big big trouble”
The hackers are threatening to expose T-Mobile.
 Follow us
- Ransomware gang BYOD listed T-Mobile on its site but has not released data samples.
- BYOD breached Trump Mobile last week and published data from 3,615 users.
- T-Mobile has about 142 million US customers and is majority-owned by Deutsche Telekom.
- Deutsche Telekom and its subsidiaries have faced repeated hacker claims, which the company denied.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
The German-owned telecom giant has been threatened by the same ransomware gang that breached Trump Mobile last week.
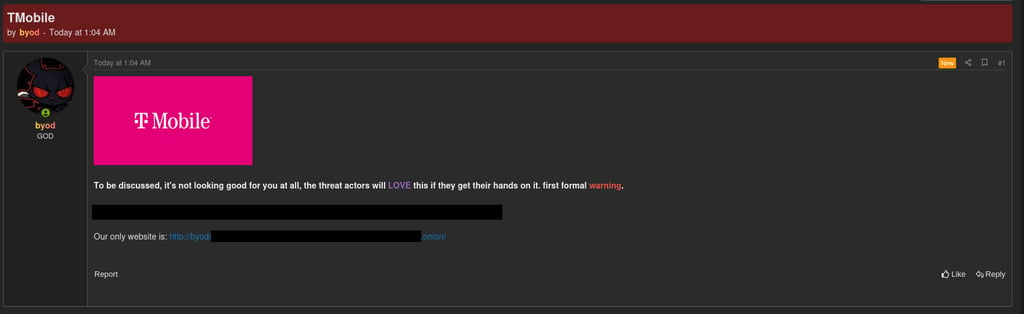
The ransomware operation BYOD listed telecommunications giant T-Mobile on its leak site on October 7th, claiming it had obtained data from the telecommunications giant.
“You're in big big trouble, oh no, what will you ever do in this situation?” BYOD wrote in its message to the company. The group then told T-Mobile to use the contact details on its site, adding that it would remove the listing once communication had been established.
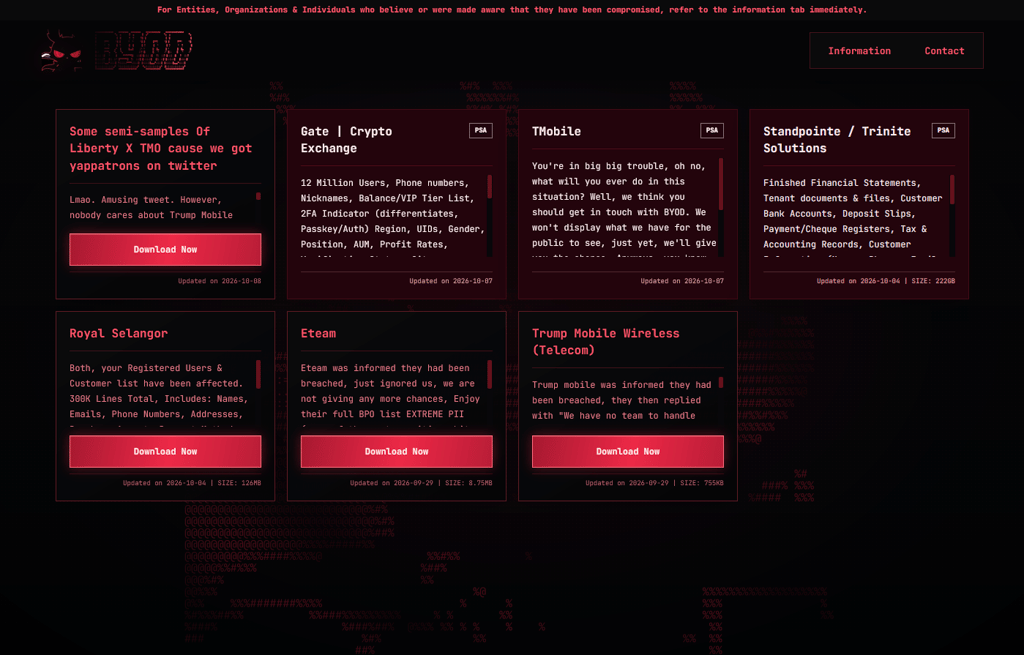
The gang also posted another warning on the well-known hacker forum to put additional pressure on the alleged victim. So far, the gang has not released any data samples to back up its claims.
While it is impossible to know at this stage what data may be involved, not releasing samples in the initial stages is a common tactic used by extortion gangs to build pressure.
T-Mobile US is primarily owned by the German telecommunications company Deutsche Telekom. The company is Europe's largest telecommunications provider and holds a 53% majority stake in T-Mobile. T-Mobile US has approximately 142 million customers in the United States.
We reached out to T-Mobile and are still waiting for their official statement.
Who is BYOD?
The gang is a newcomer to the ransomware scene, as it was first observed at the end of September this year. It has 8 victims posted on its leak site as of October 8th, 2026.
So far, the gang's business model is unconfirmed – whether it is a ransom-as-a-service (RaaS) model or an independent operation.
The gang published the data of 3,615 Trump Mobile users, including names, contact details, addresses, and orders, a week ago.
Hackers have claimed Deutsche Telekom multiple times
T-systems' parent company, Deutsche Telekom, has often been on the radar of cybercriminals.
In 2024, Deutsche Telekom was one of dozens of companies from around the globe posted on the infamous LockBit ransomware leak site.
In 2025, hackers claimed to have leaked 64 million records from T-Mobile. At the time, T-Mobile responded to Cybernews saying that the data hackers uploaded is not related to the company or its clients.
This May, hackers claimed that they had obtained a dataset belonging to Deutsche Telekom and put it up for sale. However, the company denied that the data was real.
Just a week ago, ransomware gang Safepay claimed another Deutsche Telekom subsidiary, T-Systems. After attackers set the public timer for negotiations to begin, the company confirmed to Cybernews that the gang has been pressuring it to pay a ransom.
However, the company denied that any sensitive data had been exfiltrated, stating that attackers had only breached a small test environment.