Trump Mobile data breach hits family’s own cybersecurity chief
The exposed details include other users’ personal information.

 Follow us
- Criminal gang BYOD published the data of 3,615 Trump Mobile users, including names, contact details, addresses, and orders.
- Cybernews researchers said the samples appeared legitimate and were not linked to earlier breaches.
- Eric Brunnett, the Trump Organization’s technology and security chief, appears among the exposed users.
- Hackers claim they still have live access to a Trump Mobile dashboard.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
A Trump Mobile data leak has exposed the personal information of almost 4,000 people, including the cybersecurity chief responsible for protecting the Trump family business.
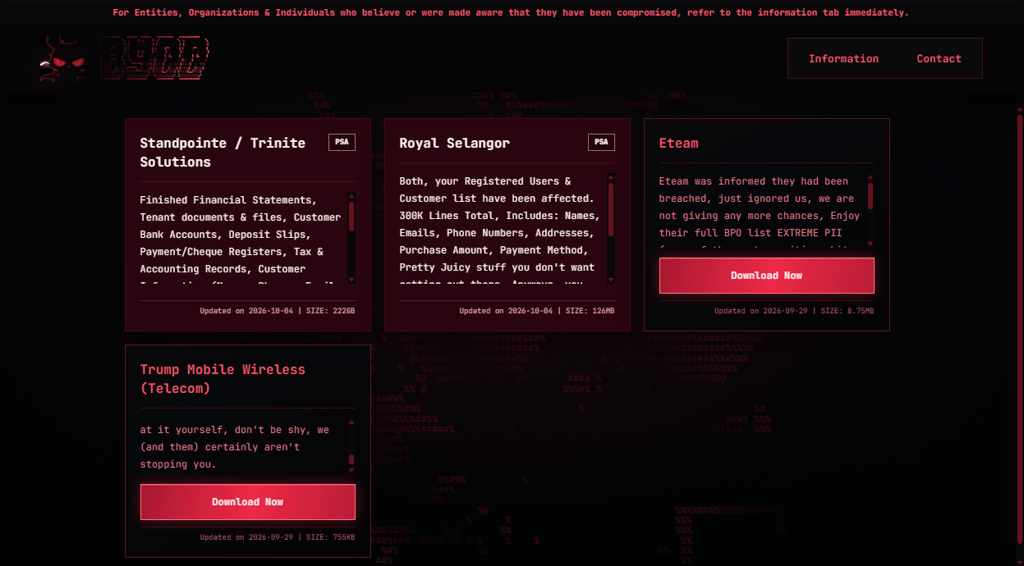
A dark web forum post revealed that a new criminal cyber group calling itself BYOD published data belonging to 3,615 Trump Mobile users on its leak site last week.
The exposed information reportedly included names, email addresses, phone numbers, home addresses and order details.
After examining the breached samples, the Cybernews research team confirmed that they appeared to be legitimate and were not tied to any previous breaches.

Among those exposed is Eric Brunnett, vice president and chief information officer of the Trump Organization, the entity which handles the family’s business affairs.
Brunnett’s LinkedIn profile says he oversees “all information technology and information security for all aspects” of the organization.
Last year, Brunnett told Hospitality Upgrade – in an interview that hailed him a “Technology Rockstar” – that there were an “unimaginable number of bad actors trying to infiltrate our network every day.”
“We have to maintain a security posture that doesn’t allow breaches of any kind,” he added.
While Brunnett’s personal information appears among data associated with Trump mobile users, no members of the Trump family appear among the customers whose information was exposed.
BYOD claims the breach
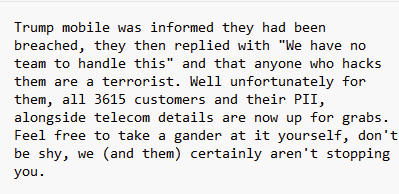
In its initial message announcing the breach, BYOD said they informed Trump Mobile of the breach but were told that the mobile carrier had “no team to handle this” and that “anyone who hacks them is a terrorist.”
“Well unfortunately for them, all 3615 customers and their PII, alongside telecom details are now up for grabs,” BYOD added.
It has been reported that BYOD gained initial access by infecting an employee at Liberty Mobile, a Florida-based mobile virtual network operator (MVNO) that powers Trump Mobile, with a remote access trojan.
The hackers claim they then pivoted to exposed Trump Mobile subdomains and exfiltrated the customer data. BYOD also claims it retains “live access” to a Trump Mobile dashboard.
Straight Arrow contacted several people listed in the dataset and confirmed details containing the leak.

One person said he had paid a $100 deposit for Trump Mobile’s T1 phone but never received the device.
Another woman told PCMag that she had never successfully signed up for Trump Mobile or pre-ordered its T1 phone.
She had provided the company with her email address and phone number, which later appeared in the leaked data set.
Trump Mobile was also breached in May
The incident is not the first time Trump Mobile has found itself at the center of a customer data exposure.
Cybernews previously reported that a vulnerability in the company’s T1 pre-order system exposed names, addresses, and order information belonging to roughly 30,000 people.
Trump mobile launched last June, with a $499 gold smartphone in a bid to court conservative consumers with a wireless service positioned as an alternative to major telecom providers.
Trump Mobile is operated by T1 Mobile, a Florida-registered company whose ultimate ownership has never been fully disclosed.