ShinyHunters targeting Oracle zero-day days after FBI attack, Google warns
A new ShinyHunters campaign is bypassing firewall defenses and deploying a newly discovered backdoor – is this how they breached the FBI?


- Google notified more than 100 organizations about renewed exploitation of Oracle PeopleSoft flaw CVE-2026-35273.
- ShinyHunters is bypassing web application firewall rules on systems that were not fully patched.
- Google says dozens of systems have web shells, with victims in healthcare, transport, government, and other sectors.
- The group is deploying SIDEEYE, a backdoor that can steal credentials and control compromised Windows servers.
ShinyHunters has relit the fire under Oracle PeopleSoft, launching a renewed mass-exploitation campaign using the same zero-day it previously exploited in June, Google announced Friday in a new report.
Google says it has notified more than 100 organizations worldwide about the recycled critical flaw (CVE-2026-35273).
ShinyHunters bypasses firewall defenses
According to Google, the gang is bypassing WAF firewalls in organizations that, instead of actually patching the PeopleSoft platform, simply adjusted their firewall rules as a stopgap in place of a permanent fix.
We observed a consistent sequence of events in targeted PeopleSoft environments, progressing from discovery and verification to web shell deployment and hands-on-keyboard activity,– Google Threat Intelligence Group
The Google blog post explains that ShinyHunters (UNC6240) has adapted to published defensive guidance, targeting organizations that implemented WAF rules but did not patch the vulnerability.
“UNC6240 is modifying its exploit to bypass web application firewall (WAF) rules blocking the vulnerable Environment Management Hub (PSEMHUB) endpoint,” Google said.
The new campaign appears to be targeting organizations that followed mitigation guidance but chose not to patch.
Connected to FBI attacks?
Google researchers say dozens of systems worldwide have had web shells deployed, with targets expanding well beyond universities to technology, IT services, healthcare, agriculture, transportation, and government.
It’s not clear if the FBI – which ShinyHunters claimed to have hacked earlier this week via a "newly discovered zero-day in Oracle PeopleSoft" – actually patched its systems or used the WAF workaround.
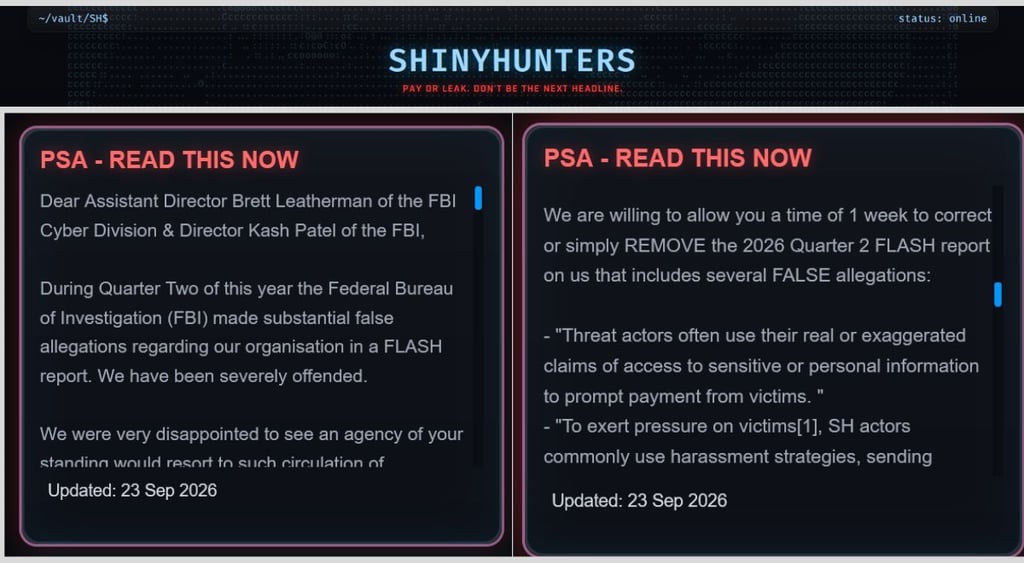
The group claims the motivation for stealing sensitive data on "almost all FBI agents/employees" is retaliation for an FBI advisory released in May, which they want the agency to partially retract.
While the FBI acknowledges the claims and has reported issues with several online portals, ShinyHunters gave the agency until Sunday to remove its statements about the gang's behavior or face retaliation, although the hackers haven't said what that might entail.
New SIDEEYE backdoor found in attacks
Google researchers say they've also uncovered ShinyHunters deploying a new multi-stage backdoor in the attacks dubbed SIDEEYE.
The backdoor is being deployed on compromised Windows PeopleSoft servers and is set to communicate directly with the hackers' command-and-control (C2) servers.
The hackers are disguising the trojanized malware as a “Light Alloy” media player installer, digitally signed with a valid certificate to make it appear legitimate. The certificate has since been revoked.
Once installed, SIDEEYE can steal credentials, manage files and processes, open a reverse shell, and proxy traffic, the report warns.
Meanwhile, Google is urging defenders to review the Indicators of Compromise, detection guidance, and remediation steps provided in Friday’s report, including:
- Patch CVE-2026-35273 now
- Inspect PeopleSoft servers for the web shells/backdoor
- Rotate exposed credentials
- Hunt for the campaign's network indicators




Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.