ShinyHunters claims FBI systems hack, sensitive data "on almost ALL FBI agents"
ShinyHunters says the FBI has 7 days to retract what it calls "false allegations" about the group, while refusing to say what happens if the deadline expires.
Image by Cybernews/Getty Images.
 Follow us
- ShinyHunters claims it breached the FBI, exposing sensitive agent and job applicant data, while the FBI says it is investigating.
- ShinyHunters told Cybernews some of the data included PII, employment, education, background, and sensitive medical information.
- ShinyHunters claims it stole 2TB to 3TB of FBI data, with some of the alleged stolen data independently verified.
- ShinyHunters gave the FBI seven days to remove a report disputing the group’s claims and has not said what happens next.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
The notorious ShinyHunters gang on Tuesday claims to have breached the FBI, compromising multiple systems and agent data – all in apparent retaliation against the law enforcement agency for publishing false allegations about how the hacker group operates.
In a direct email to Cybernews, ShinyHunters revealed new details about the alleged breach, claiming it gained access to FBI systems on Monday night "immediately after discovering a new z-day in Oracle PeopleSoft."
The FBI is aware of claims regarding unauthorized activity affecting FBIjobs.gov and is currently investigating,the federal agency said in a statement sent to Cybernews Tuesday evening.
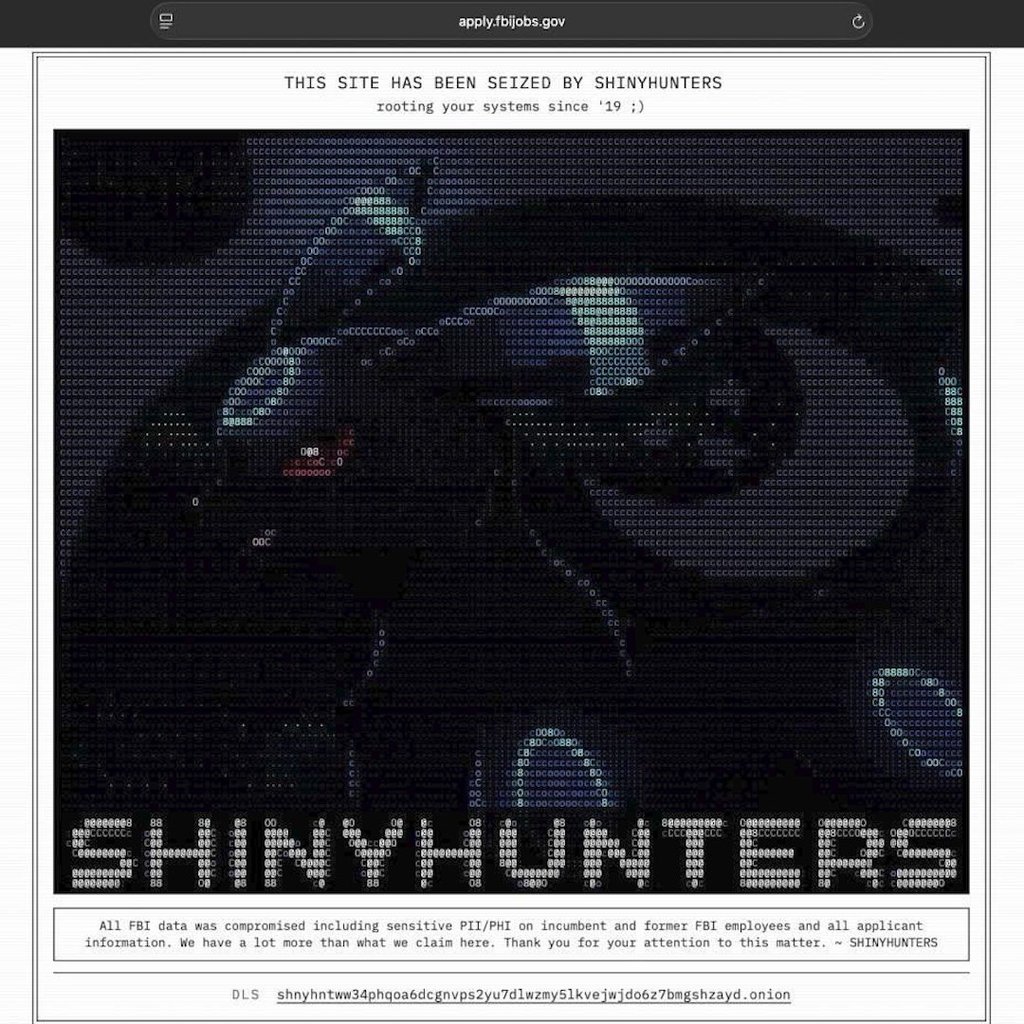
Earlier in the day, 404 Media reported the cybercriminals temporarily defaced the FBIjobs.gov website, replacing the landing page with a fake notice (shown above) stating, “This site has been seized by ShinyHunters.”
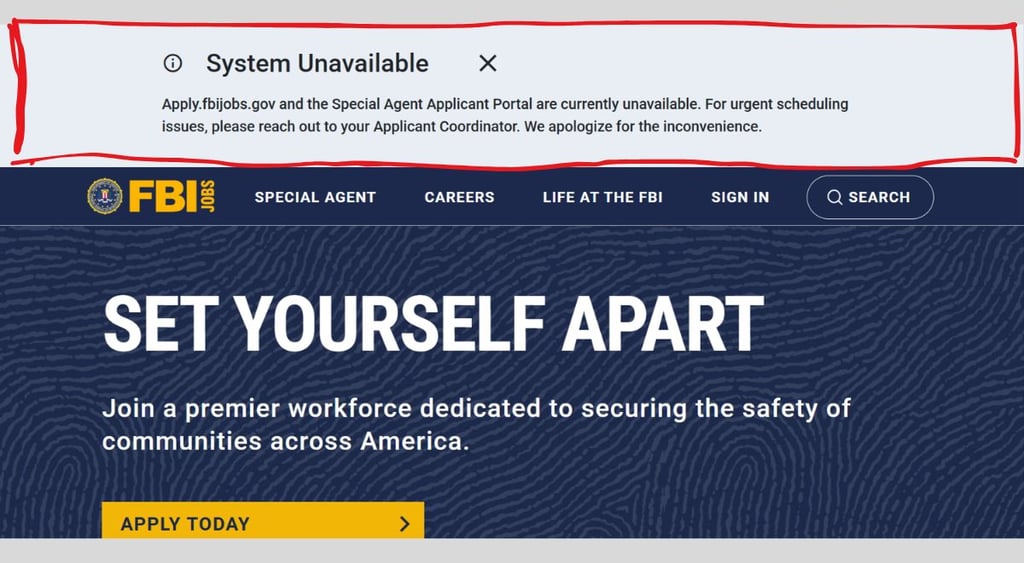
Now, a banner appearing on top of the FBI Jobs website states "The Special Agent Applicant Portal are currently unavailable," when Cybernews last checked Tuesday evening.
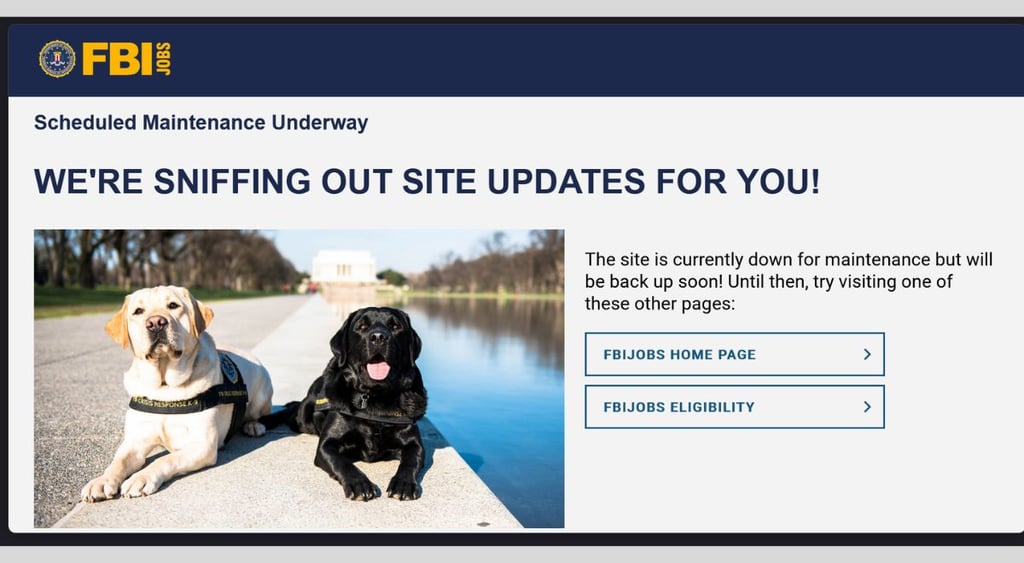
The FBI’s applicant portal, apply.fbijobs.gov, was also displaying an “under maintenance” notice.
To get an idea of how many individuals may have been exposed, the FBI's FY2027 budget requests more than 14,000 special agents and roughly 3,000 intelligence analysts, according to the FBI website.
As for applicants, the FBI lists more than 48,000 special-agent applications across 2022 and 2023 combined, or roughly 24,000 per year.
ShinyHunters claims access to FBI systems
ShinyHunters posted a lengthy message on its dark leak site early Tuesday, addressed directly to FBI Director Kash Patel and Assistant Director of the FBI Cyber Division Brett Leatherman.
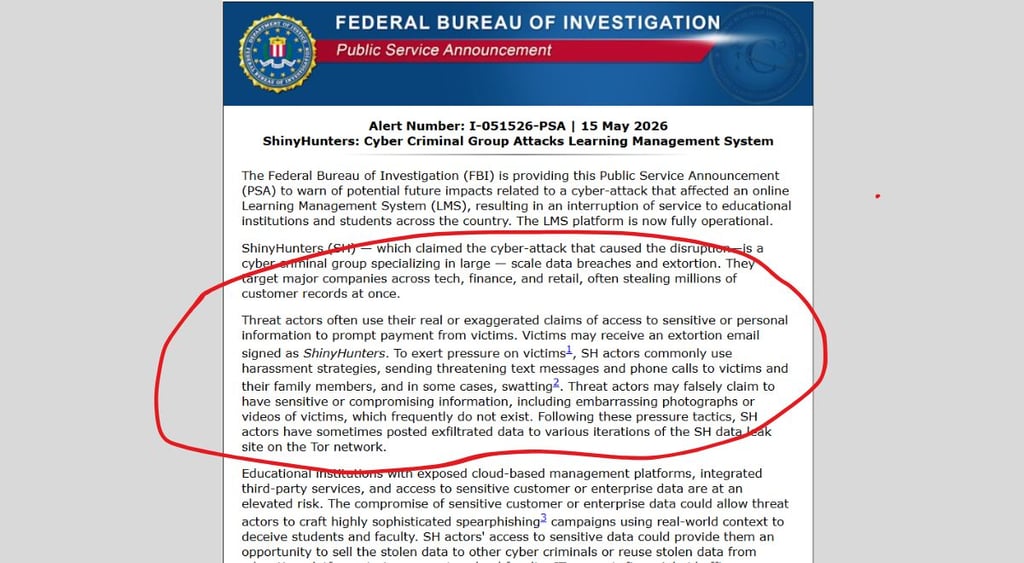
In the 567-word missive, ShinyHunters says it is “severely offended” by the “circulation of disinformation” that apparently was part of an FBI public service announcement (Alert Number: I-051526-PSA) on the gang from earlier this year.
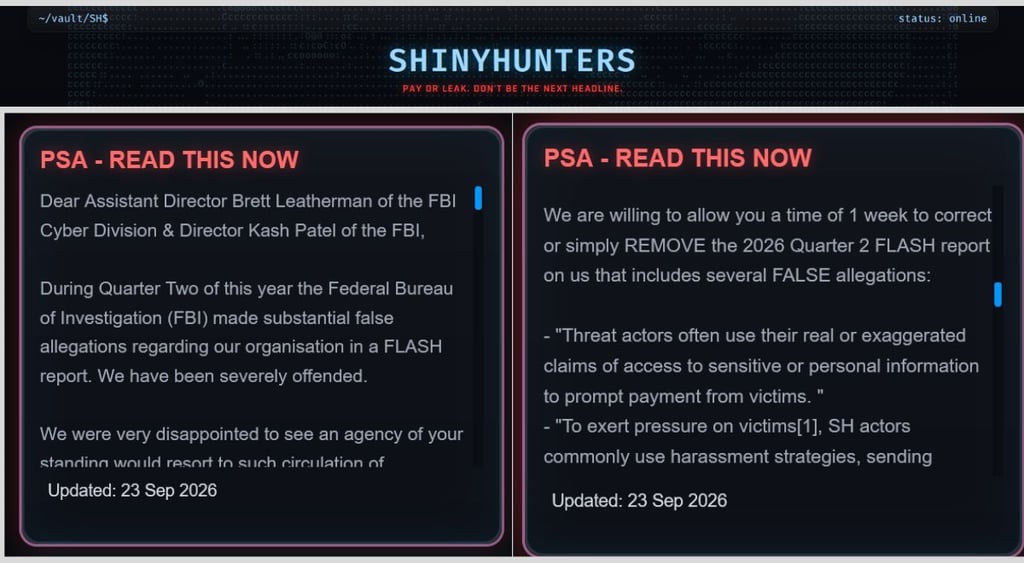
Apparently because of the alleged diss, the seasoned hacker gang decided to hack the federal agency as payback or at least to make a point.
“Whether it be a Special Agent or any other role within your agency. The following FBI services were compromised: Criminal Justice (CJ), HR, Medlink, and more,” the group wrote.
We have compromised the FBI.ShinyHunters posted in the leak site entry.
We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job.
If ShinyHunters is referring to the FBI's Criminal Justice Information Services (CJIS), the potentially exposed information could be extremely sensitive.
CJIS is the FBI's central repository for criminal justice information, including criminal histories, fingerprints, and other biomentric data, wanted and missing persons records, background checks, arrests, charges, case dispositions, and other law enforcement and identifying information.
What FBI data was allegedly compromised?
Inviting journalists to contact the group for more information on the alleged incident, this journalist took a chance and fired off an email, receiving a response in less than 10 minutes.
ShinyHunters provided some basic information about the hack, albeit already circulating among other journalists who obviously had the same idea I did.
ShinyHunters claimed to to 404 Media it had stolen between 2TB and 3TB of data from the federal law enforcement agency.
ShinyHunters also gave the media outlet a sample appearing to contain information on 5,000 FBI employees, including alleged home addresses, phone numbers, dates of birth, and, in some cases, spousal information.
The outlet reported it matched some phone numbers in the sample to individuals named in the files, with additional checks linking some numbers to US Department of Justice personnel.
Meanwhile, ShinyHunters shared with Cybernews that the breach took place on Monday following the group's apparent discovery of a zero-day vulnerability in Oracle's PeopleSoft enterprise software.

Oracle's PeopleSoft platform is used by large organizations to manage human resources, recruiting, employee records, and other workforce operations – which tracks with the job-related data potentially involved.
Cybernews has reached out to Oracle for comment and is awaiting a response.
Curious what others think about this story? Contribute your thoughts to the debate below.
And although the group was stingy with other details, such as how many FBI agents and job applicants may have been compromised, and whether we could view some proof samples (maybe, they insinuated), the gang did provide a list of “sensitive data” accessed, presumably from the FBI’s HR systems.
We are confident that we hold data on almost all FBI Agents/Employees and we possess a substantial number of job applications,ShinyHunters told Cybernews.
They went on, calling the information found inside the job applications “a wide variety of data,” including:
- Full personally identifiable information (PII)
- Background information
- Educational data: Specific grades and degrees
- Former US government employment information
- Serious and sensitive medical and drug-related information
- More stuff we can go on and on for
ShinyHunters also did not tell Cybernews whether the data itself had been exfiltrated or if they still had access to any of the FBI systems allegedly breached.
The ransomware operators have now given the FBI exactly seven days “to correct or simply REMOVE the 2026 Quarter 2 FLASH report” and the “FALSE allegations.”
ShinyHunters stressed “unequivocally” that they are exercising their First Amendment rights, actively combating disinformation, and that “our threats and claims are very real.”
Furthermore, ShinyHunters did not say what would happen with the data if the FBI does not remove the content by September 30th, simply telling Cybernews “No Comment.”
Why ShinyHunters is threatening the FBI
The FBI’s PSA, titled ShinyHunters: Cyber Criminal Group Attacks Learning Management System and published May 15th, profiles the group in reference to the recent Canvas by Instructure e-learning platform hack.
Ironically, Canvas admitted it paid ShinyHunters an undisclosed ransom to protect student data and regain access to the platform, which the group hacked during spring finals week, causing chaos at thousands of schools worldwide. In fact, unconfirmed rumors put that amount at $10 million, but I digress.
The passages ShinyHunters is at odds with include three main points, claiming the group:
- Exaggerates claims of access to sensitive or personal information to prompt payment from victims.
- Commonly uses harassment strategies to pressure victims and their family, including threatening text messages, phone calls, and swatting.
- Falsely claims to have sensitive or compromising information on victims, including embarrassing photographs or videos.
“We wish to state unequivocally we have NEVER conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats," ShinyHunters says in Tuesday’s post to the FBI.
The group also argues that it has unequivocally “NEVER claimed to have sensitive or compromising information,” further noting in all caps that “WE ARE NOT SEXTORTIONISTS.”
The group also made clear it has nothing to do with “The Com” – a decentralized network of cybercriminals where nihilistic hackers often brag about their hacking exploits and promote violence against victims.
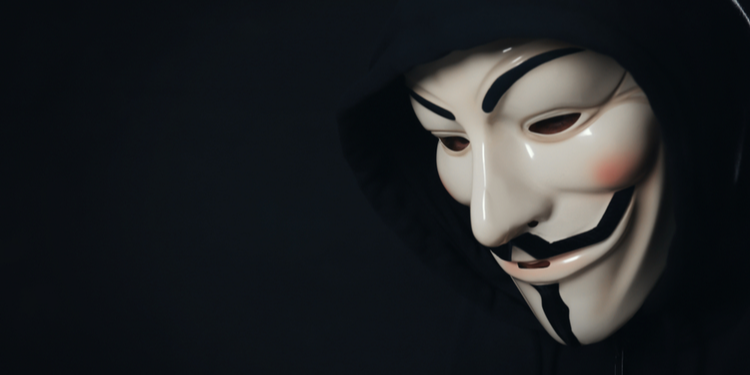
We wish to STATE UNEQUIVOCALLY we are NOT apart of "The Com". We have NEVER been apart of "The Com,ShinyHunters states.
The group further claims the criminal network is simply “a propaganda started by the InfoSec Industry, which has brainwashed past FBI and DOJ officials into formalising this nonsense.”
Finally, ShinyHunters took a swipe at “biased public reporting” from journalists without naming anyone in particular.
The attack on the FBI comes just weeks after the Qilin ransomware gang breached the US Bureau of Alcohol, Tobacco, Firearms and Explosives, otherwise known as the ATF, leaking more than 6.3 GB of sensitive data tied to criminal investigations, phone records, and forensic evidence.
Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.