NEW: H&M faces data leak threat as suspected breach trail leads to warehouse supplier
Something about this breach doesn’t add up.

Photo By Raymond Boyd, Getty Images.
 Follow us
- Previously, H&M said it is investigating breach allegations and says it currently sees no signs of compromise.
- Cybernews researchers found no matching H&M post on ShinyHunters’ usual channels or server.
- Hackers now threaten to leak data within 3 days unless H&M contacts them.
- Sample records point to GreyOrange warehouse software, but they do not prove employee data exposure.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
H&M is investigating breach claims, with hackers giving the company 3 days to respond. New details suggest the attackers may have targeted a warehouse inventory provider.
Swedish fast fashion giant H&M has faced breach allegations. As many media outlets reported, ShinyHunters was behind the data breach. The company said it is investigating and, at the moment, sees no signs of a compromise.
Allegedly, the breached data included sensitive operational information, including inventory records, logistics data, sales analytics, and details about the infrastructure used to manage stores and fulfill orders.
New data has since come in, suggesting it may have been a third-party breach affecting H&M. The attackers are threatening to leak the data in 3 days.
Is ShinyHunters not behind the attack?
According to cybersecurity tracking tool Vercert, the H&M dataset appeared on underground forums last week.
The threat actor who posted it was identified as ShinyHunters. However, when Cybernews researchers checked the specific entry, the ShinyHunters' account was marked as retired, and no such post was found. Other underground marketplaces have no similar entries.
“What I find weird is that ShinyHunters usually put up their warnings, datasets, etc., on their onion site. Their onion site is offline currently. However, the server where the datasets are kept is still online, and it does not have anything related to H&M,” our research team explained.
According to ransomware[.]live ShinyHunters was active up until the end of September, which is quite a bit of time before this alleged listing went up. ShinyHunters updates are usually pretty fresh and regular.
At the time of publishing, ShinyHunters has still not posted anything related to H&M on its server. “Combining this with the fact that the dataset is thrown around multiple Telegram channels, it makes it even less likely that this is actually done by Shinyhunters,” said our researchers.
“This could be the case where some random hackers claim to be ShinyHunters.”
H&M’s warehouse inventory software may have been breached
A new communication appeared on the hacker channel, suggesting that the H&M cyber incident may have been a third-party breach.
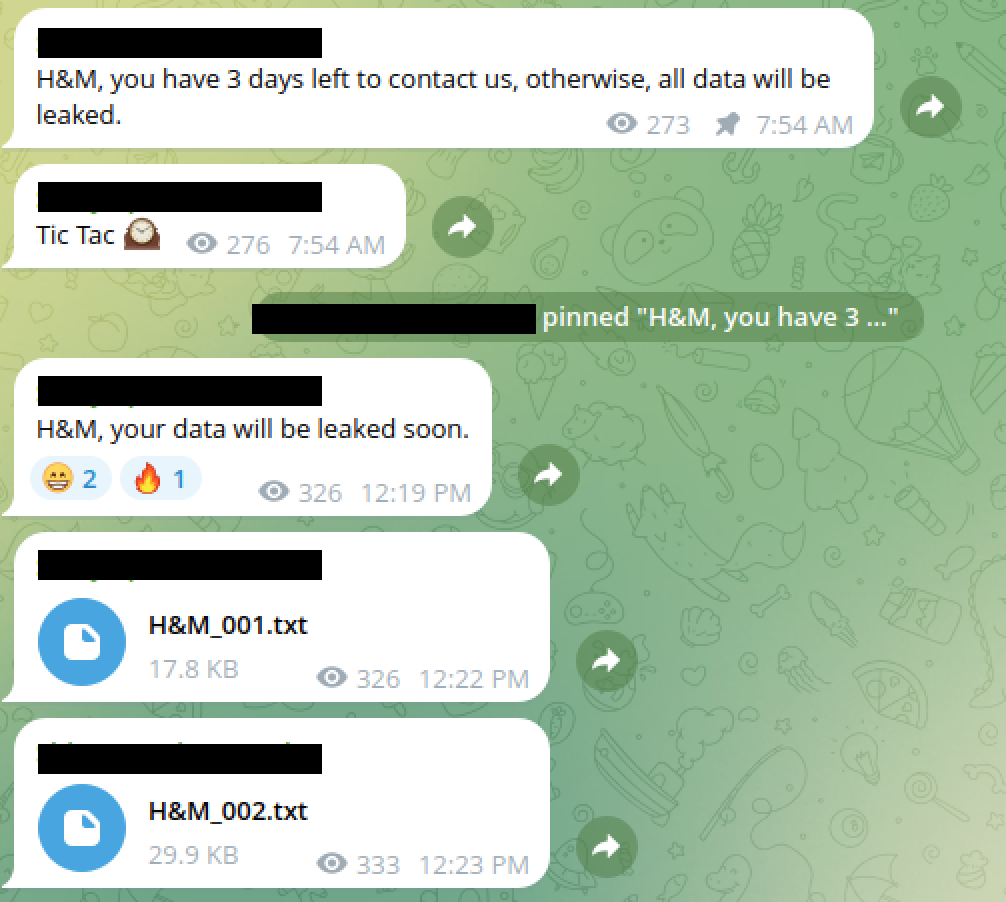
Threat actors, who are definitely not ShinyHunters, posted on their Telegram channel that H&M has 3 days to contact them or the data will be leaked.
They also added a file with a few JSON records of various product information. Our researchers investigated the samples and found they were linked to GreyOrange, a software platform used by shops to manage warehouse inventory. According to the company’s website, H&M is one of its clients, along with Walmart Canada.
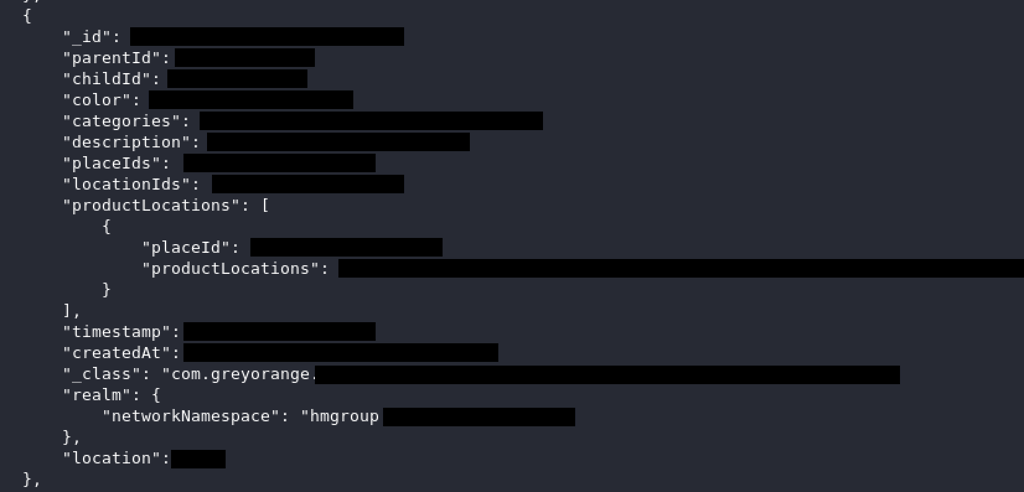
The samples include data that could be attributed to H&M, such as product image URLs and various identifiers.
“This does not mean that threat actors necessarily have more sensitive info, such as personal employee data. It highly depends on how the specific system architecture is built and how GreyOrange could be integrated into it,” our researchers said.
We reached out to GreyOrange and H&M for comment and will update this article once we receive a response.

Check if your data was exposed
Find out if your email and related personal information have appeared in known data breaches.