Only 12% of the top AI companies have a bug bounty or CVD program, according to Cybernews research
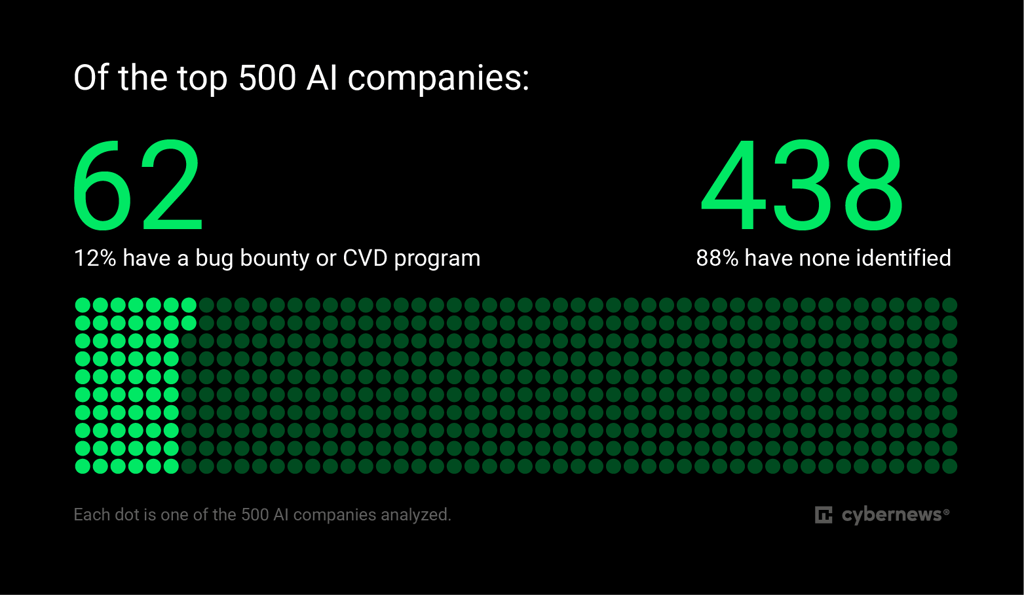
The Cybernews AI Trustworthiness Ranking reveals that only 62 of top 500 AI companies have public programs for reporting security vulnerabilities.
Image by Cybernews.
 Follow us
- OpenAI recently announced that it will be increasing its rewards in its Security Bug Bounty Program.
- According to the Cybernews AI Trustworthiness Ranking, only 12% of the top 500 AI companies have a bug bounty or coordinated vulnerability disclosure (CVD) program.
- Alongside OpenAI, they include Google, Microsoft, Meta, Anthropic, Mistral AI, Perplexity AI and Hugging Face.
- Other prominent AI companies have no identified program. They include Midjourney, ElevenLabs, DeepSeek, Cursor, Runway, and Suno.
OpenAI recently announced that it will be increasing its rewards in its Security Bug Bounty Program. A researcher who finds a critical vulnerability in ChatGPT, Codex or the API Platform can now earn up to $30,000, while exceptional findings can earn up to $172,000 with bonuses.
According to OpenAI’s announcement, “independent security researchers play an essential role in protecting technology across the industry.” Cybernews looked at whether other AI companies give researchers any public way to report flaws.
According to the Cybernews AI Trustworthiness Ranking, which evaluates the top 500 AI companies, only 12% of them have a bug bounty or coordinated vulnerability disclosure (CVD) program.

Why should users care about bug bounty programs?
People often share sensitive data with AI tools, including health information or work documents. An undiscovered security flaw related to how that data is stored could expose it even if the user doesn’t do anything wrong. That’s why OpenAI and other companies have set up public bug bounty and disclosure programs – so that they spot flaws with the help of security researchers, before bad actors do.
According to Voldemaras Kadys, Head of Security and Platform Engineering at Mediatech, the digital publishing house behind Cybernews, “Internal teams tend to focus on how the system functions and how to improve it, because that is the business goal and they stick to it. Bringing in outside researchers through a bug bounty program changes that. They focus on breaking the system, so they may look at the software in ways the internal team never did.”
The Cybernews AI Trustworthiness Ranking identified 62 AI companies that have a bug bounty or CVD program. Alongside OpenAI, they include Google, Microsoft, Meta, Anthropic, Mistral AI, Perplexity AI and Hugging Face. Meanwhile, other prominent AI companies have no identified program. They include Midjourney, ElevenLabs, DeepSeek, Cursor, Runway, and Suno.
That doesn’t mean these companies don’t test their security. The research counts only publicly identifiable programs, so a company may run internal security teams, hire penetration testers, commission audits or operate a private, invite-only bounty that isn’t visible from the outside.
Still, a public reporting channel gives outside researchers a clear place to send what they find. For the 438 companies for which the ranking found no bug bounty or CVD program, researchers do not have that option. Meanwhile, OpenAI’s announcement shows why it can matter: the company says independent researchers can catch vulnerabilities its own testing may have missed.
For more information on the AI Trustworthiness Ranking, click here.