Critical Authlib authentication bypass flaw leaves countless apps in danger
Authlib maintainers could not be reached to coordinate the vulnerability.
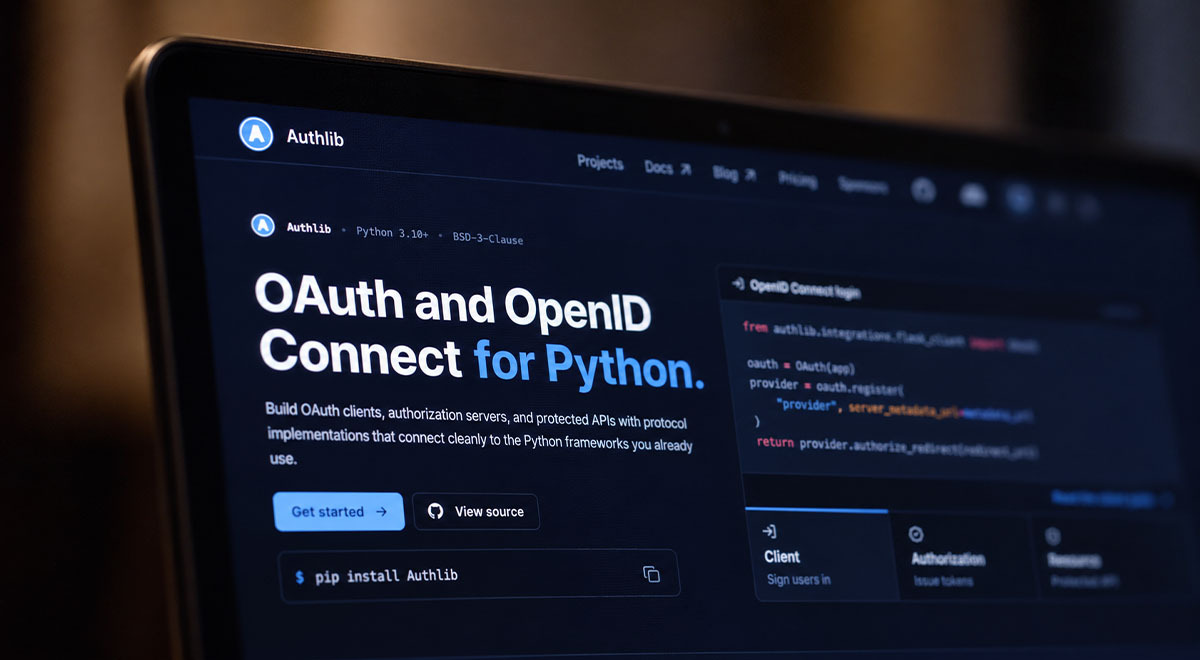
Authlib. Image by Cybernews.
 Follow us
- CERT/CC says Authlib can accept unsigned data as trusted, which may let attackers bypass login checks.
- The flaw affects Authlib versions up to 1.7.2, CERT/CC has not confirmed a fixed release.
- Attackers may need only a crafted payload, not keys or credentials, to forge identity or privilege claims.
- Authlib is widely used and was downloaded 103.3 million times from PyPI last month.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Authlib, a Python library downloaded over 100 million times a month and widely used for authentication, contains a severe flaw that allows attackers to pass off forged, unsigned data and bypass login checks.
The CERT Coordination Center (CERT/CC) at Carnegie Mellon University warns of a serious flaw in Authlib: attackers can bypass authentication, inject fake messages, forge authorization claims, and other payloads.
Authlib is a popular Python library that provides tools for implementing multiple modern authentication and authorization standards, including OAuth, OpenID Connect, JSON Web Token, JSON Web Signature, and JSON Web Encryption (JWT, JWS, JWE).
Many web applications, mobile apps, microservices, and APIs depend on it to handle token creation, cryptographic validation, and secure communication.
Last month, Authlib was downloaded 103.3 million times from PyPI, according to data from pypistats.org.
The vulnerability affects the library’s JSON Web Signature handling. JWS is used to prove that digital information was signed by a specific sender, but a faulty function, deserialize_json(), accepts JWS objects even when the “signatures” section is empty.
“Because the function starts by assuming the signatures are valid and never performs any checks when the list is empty, it ends up treating unsigned data as if it were properly signed,” CERT/CC warns in a security advisory.
Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
A potential attacker can provide a JWS with no signatures or credentials at all, and Authlib would still treat it as trusted.
This leaves systems that rely on Authlib’s JWS verification vulnerable – they might accept attacker-supplied content as legitimate.
CERT/CC lists several potential attack scenarios:
- Forged identity or privilege‑escalation claims (e.g., sub=admin) can lead to authentication bypass.
- Attackers can inject signed messages between microservices using JWS.
- Attackers can elevate privileges by forging authorization claims, such as scopes, roles, or permissions.
- Integrity can be bypassed in systems relying on signed JWS data.
The barrier to attack appears to be low – no key or credentials needed, just the ability to send a crafted payload.
The watchdog also warns that there is no official patch – the vendor couldn’t be reached to coordinate the vulnerability. Over 5 weeks passed after the initial responsible disclosure.
The bug, tracked as CVE-2026-96760, affects Authlib versions up to and including 1.7.2. This version was released in May and was later replaced by a newer version 1.8.0 on August 30th, 2026.
CERT/CC advisory doesn’t say whether 1.8.0 addresses the flaw. The 1.8.0 release notes or commit titles do not mention JWS or the affected function. The code changes on GitHub don't appear to touch the affected function.
“Users are advised to monitor the project's GitHub repository for updates and install the latest version of this library once a fix has been released,” the CERT/CC’s advisory reads.