Citrix NetScaler under active zero-day attack: critical patches available, 22K servers exposed
Administrators are urged to investigate systems for potential compromise.

Image by Shutterstock.
- Citrix patched eight NetScaler flaws, including two zero-days attackers already exploit.
- CISA says both exploited bugs can enable remote code execution without passwords or user interaction.
- ShadowServer found about 22,000 exposed NetScaler instances, with 8,800 in the US.
- Citrix urges admins to patch quickly and check systems for signs of compromise first.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Citrix and cyber authorities are sounding the alarm over critical NetScaler zero-day vulnerabilities, with attackers targeting servers globally and gaining remote code execution. Nearly 22,000 servers are visible on the open internet, most of which are in the US.
Citrix has released critical patches for NetScaler Application Delivery Controller (ADC) and Gateway, and urges users to update ASAP.
Eight security vulnerabilities affect the software, and 2 of them are already actively exploited in the wild as zero-days.
Companies widely deploy Citrix Netscaler to manage traffic – it handles load balancing, security (including Web Application Firewall), caching, and access management. The appliance typically sits at the edge of the enterprise network, which makes it a lucrative target for attackers.
Attackers need no passwords or victim interaction, and can exploit the most severe vulnerabilities over the network. The attack complexity is low, requires no additional features, and works on default configurations. The blast radius can extend beyond the vulnerable NetScaler instance itself.
“Cloud Software Group strongly urges affected customers of NetScaler ADC and NetScaler Gateway to install the relevant updated versions as soon as possible,” the advisory reads.

Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
Due to the severe potential consequences of successful exploitation, the US Cybersecurity and Infrastructure Security Agency issued an alert and added the 2 bugs to its Known Exploited Vulnerabilities (KEV) catalog, setting a 3-day deadline for federal agencies to update.
“Both are critical, zero-day vulnerabilities that can independently enable remote code execution. CISA has received reports and partner threat intelligence confirming that threat actors are actively exploiting these vulnerabilities globally,” CISA said in the alert.
Administrators are also encouraged to investigate for indications of compromise prior to patching. Citrix made generic IoCs available through NetScaler Console and released additional guidance.
The first attacks surfaced on September 26th, 2026. NetScaler administrators reported being told by their suppliers and security teams to shut their appliances down entirely, following a private pre-notification from the Dutch National Cyber Security Centre (NCSC-NL), according to watchTowr.
“We ended up just shutting down outside access to Netscaler this afternoon until we got a clean bill of health from Citrix,” one of the admins shared on Reddit.
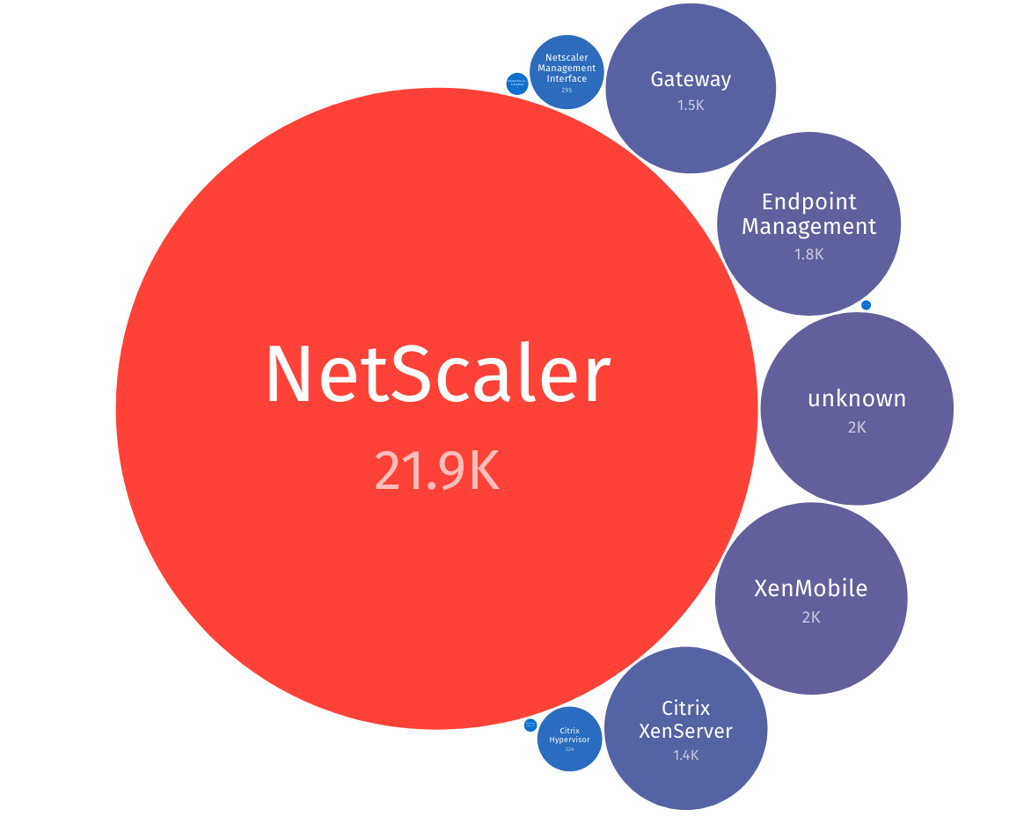
Public scans by Shadowserver Foundation reveal around 22,000 exposed NetScaler instances, many of which may still remain vulnerable.
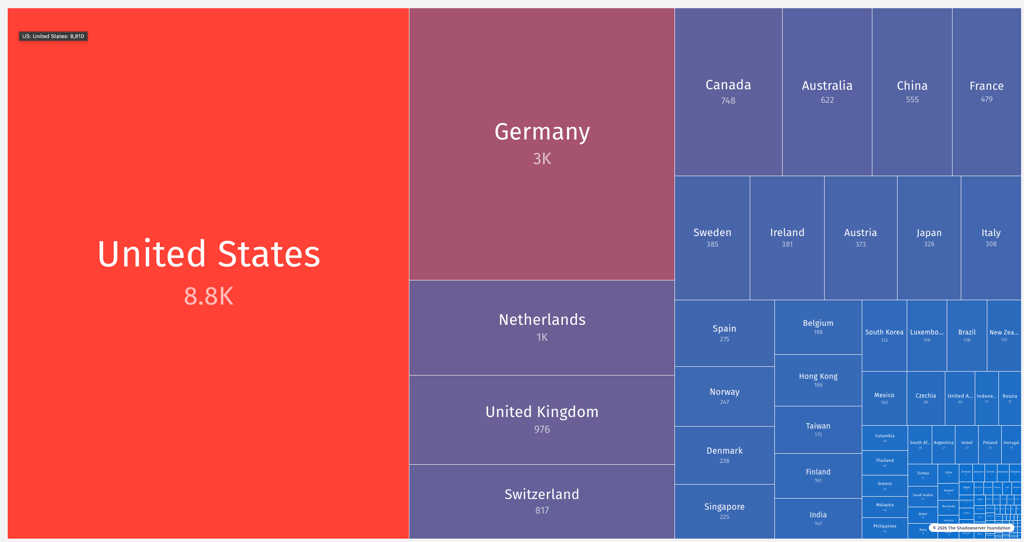
Most exposed IPs (8,800) are in the US, followed by Germany (3,000), the Netherlands (1,000), and hundreds in other countries.
The first critical bug, rated 9.5 out of 10, is an input validation vulnerability tracked as CVE-2026-88771. Another bug with exactly the same rating is a memory-overflow vulnerability, CVE-2026-88772. Six other critical or high-severity bugs include HTTP request smuggling and denial-of-service issues.
Citrix said it is notifying customers and channel partners. Only unpatched customer-managed Netscaler instances remain vulnerable – on Citrix-managed cloud services, the necessary software updates are applied by the Cloud Software Group.
The following supported versions of Citrix NetScaler ADC and Citrix NetScaler Gateway are affected:
- Citrix NetScaler ADC and Citrix NetScaler Gateway 14.1 BEFORE 14.1-73.37
- Citrix NetScaler ADC and Citrix NetScaler Gateway 13.1 BEFORE 13.1-64.23
- Citrix NetScaler ADC FIPS BEFORE 14.1-73.37 FIPS
- Citrix NetScaler ADC FIPS and NDcPP BEFORE 13.1-37.279