Flink hackers turn to customers, demanding ransom to keep their data off the dark web
They’re squeezing customers for €10 after demanding €238,000 from the company.
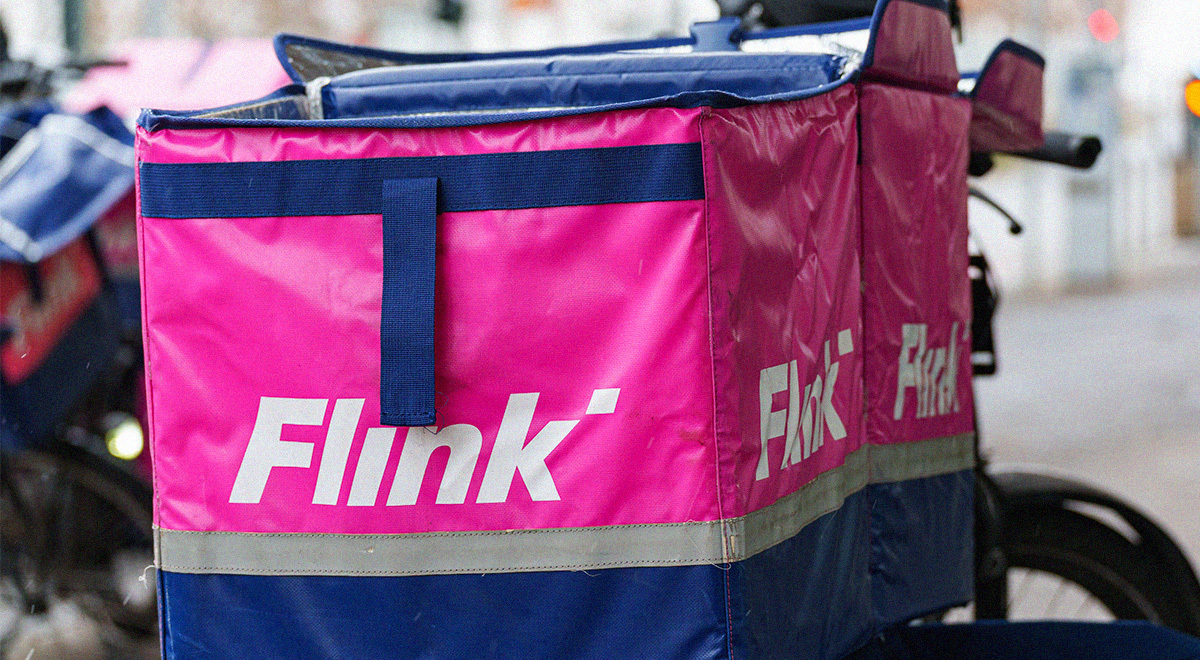
Hackers want Flink customers to pay up. Image by Shutterstock.
- Flink says an unauthorized party accessed an internal system and exposed customer contact and delivery data.
- The company says passwords were not at risk and it has stopped the unauthorized access.
- LPG Group claims it stole data on over one million shoppers and 13,000 employees.
- Hackers demanded payment from Flink and affected customers, a tactic known as triple extortion.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Ransomware extortion group LPG Group has attacked the food delivery service, Flink. Victims are being urged to either pay a small ransom or to convince the company to come up with the money.
In an email to affected customers, which has been seen by Cybernews, Flink states that an “unauthorized party” gained access to one of its internal systems, thereby compromising customer data.
The breach leaked names, email addresses, postal addresses, and telephone numbers. For some customers, delivery information such as the floor, the name on the doorbell, and delivery instructions was also exposed.
Flink reassures victims that no passwords were at risk.
When the data breach first came to light, the food delivery company initiated “comprehensive countermeasures,” without providing further details, and put a stop to the unauthorized access.
With help from external IT forensics and cybersecurity experts, the company launched an investigation to determine the incident's scope.
“Be cautious with unexpected emails, messages, or phone calls referring to Flink,” the food delivery service says in its email to affected customers, asking them not to reply to these messages or to make any payments.
LPG Group has claimed responsibility for the attack. According to the German trade magazine Retail News, the hackers gained access to Flink’s internal systems using “compromised login credentials” from one of the company’s workers.

Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
The ransomware extortion group claims to have stolen personal information of over a million shoppers and 13,000 employees.
In a message addressed to the company, LPG Group, which started its extortion practices just this month, has demanded 100 Ethereum (approximately €238,000) to delete all the stolen data.
In the same email, victims are being asked to pay a ransom as well.
“If you refuse to pay 0.005 ETH (about €10) by October 2nd, your personal information will be sold on the dark web. You can forward this email to Flink to get their attention,” the hackers write.
This tactic, in which both the company and affected individuals are being extorted by hackers, is known as triple extortion.
