One bad Android app could hijack your OnePlus 15, researcher warns
There’s no fix in sight.
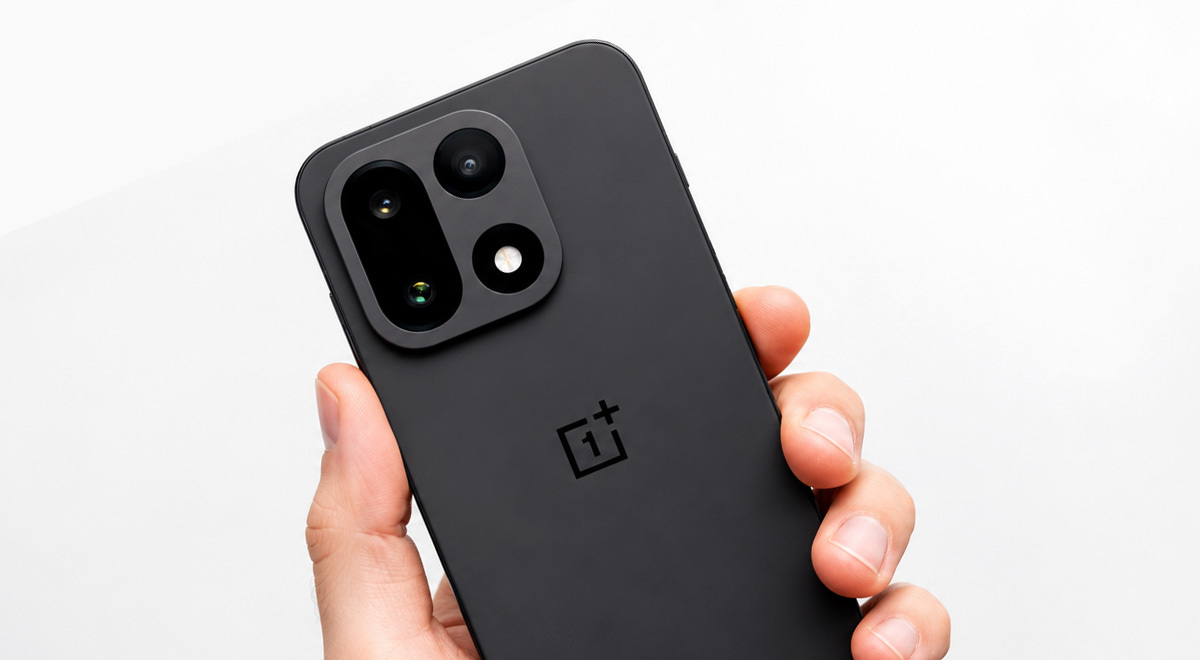
Researcher claims a malicious app could get root access to OnePlus 15. Image by Cybernews.

- A malicious app can gain root access on the OnePlus 15 without asking for suspicious permissions.
- Researcher Rasmus Moorats says he reported the flaw in May, but OnePlus has not provided a user fix.
- OnePlus told the researcher the issue also applies to all OPPO terminal product series.
- The exploit abuses built-in debugging tools to escape Android’s normal app restrictions.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
A malicious app can root the OnePlus 15, running the latest OxyGen OS, without asking the owner for any dubious permissions. The researcher behind the discovery says OnePlus has had since May to address the issue, but has so far offered no fix.
OnePlus 15 device software allows apps to break out of Android’s safety barrier and gain root access, security researcher Rasmus Moorats recently discovered. This means a malicious app could take over users’ devices without permission.
Moreover, users don’t need to click any dubious links or install software from shady vendors. Once installed, the app could enable malicious actors to do whatever they want with the device, from spying to stealing users’ data.
OnePlus is a subsidiary of Chinese manufacturer Oppo, with estimated revenues in the tens of billions of dollars.


Interestingly, after Moorats disclosed the issue with OnePlus in May, the Chinese consumer electronics maker acknowledged it, adding that the vulnerability’s impact extends beyond OnePlus devices and is “applicable to all series of OPPO terminal products.”
The company also told the researcher that he is “not entitled to independently compile and publish” a vulnerability analysis, even after OnePlus issued a fix. Additionally, the OnePlus security team told Moorats that EU cybersecurity regulations “merely urge” manufacturers to acknowledge vulnerability submissions, but do not allow them to disclose vulnerabilities independently.
However, “mere urging” is actually a mandatory requirement to adhere to the bloc’s laws. Moreover, the EU doesn’t allow researchers to publish vulnerabilities without giving companies time to fix them or to publish their findings.



Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
“In practice, this means you must actively engage with researchers, not simply receive their reports and act unilaterally. If a researcher sets a 90-day deadline for public disclosure, you need to either fix the vulnerability, provide a workaround, or negotiate an extension – not ignore the deadline,” the EU’s Coordinated Vulnerability Disclosure (CVD) body explains.
However, according to correspondence between OnePlus and the researcher, published by Moorats, the OnePlus security team threatened “legal liabilities” if the vulnerabilities were published without the company’s written consent.
Moorats published the findings over 5 months after the initial disclosure to OnePlus, without the company issuing a fix that users could apply to the problem.
We have reached out to OnePlus for comment and will update this article once we receive a reply.
Check if your data has been leaked
How does the OnePlus exploit work?
According to Moorats, the exploit works by abusing 2 built-in OnePlus software components. A typical app can first interact with an OxygenOS service called AtlasService, which appears to be tied to telemetry and debugging.
That service accepts input from apps and can trigger another system component, audioDumpInfo, a root-level diagnostic tool that collects audio-related debugging information. The problem is that the app-controlled input is passed along in an unsafe way, allowing a malicious app to add its own commands.
Once that happens, the phone launches audioDumpInfo with root privileges. Moorats explained that this first step does not appear to require special Android permissions. In effect, the exploit uses OnePlus’s own debugging machinery as a bridge out of Android’s normal app restrictions.
From there, the exploit moves to a second OnePlus component, a vendor hardware interface known as olc2, which includes a function called doShell. The interface will run shell commands for callers it recognizes as root. After the first flaw gives the malicious app an elevated foothold, the second flaw can be used to launch an even more powerful shell inside a privileged vendor context.
That gives the attacker broader control over the device than the initial step alone. In essence, the exploit allows moving through trusted OnePlus services that were meant for internal support and debugging.
