Hacker gang says it breached Deutsche Telekom’s IT arm
The German IT giant faces a hacker ultimatum.
Image by Cybernews
 Follow us
- SafePay listed T-Systems on its leak site and gave the company two days to negotiate.
- T-Systems is a Deutsche Telekom subsidiary with operations in 26 countries and more than 26,000 employees.
- Deutsche Telekom spokesperson said the ransomware affected test environment, and no sensitive data was accessed.
- Researchers link SafePay to the Conti ransomware lineage, but confidence levels vary.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
A ransomware gang has put one of Germany’s biggest IT service providers on its dark web leak site, threatening to turn the alleged breach into a public data dump if negotiations fail.
The Safepay ransomware operation has listed T-Systems, a major German information and communications technology provider and subsidiary of Deutsche Telekom, on its leak site.
The group has reportedly given the company just 2 days to negotiate, a common extortion tactic. Victims are given little time to assess what happened, investigate potentially compromised systems, and decide whether the criminals' claims are credible.
If the claims are legitimate, the alleged victim would be a significant prize. T-Systems is a subsidiary of Deutsche Telekom, which is one of Europe's largest telecommunications companies, with a customer base exceeding 300 million worldwide. The company holds a 53% majority stake in T-Mobile US.
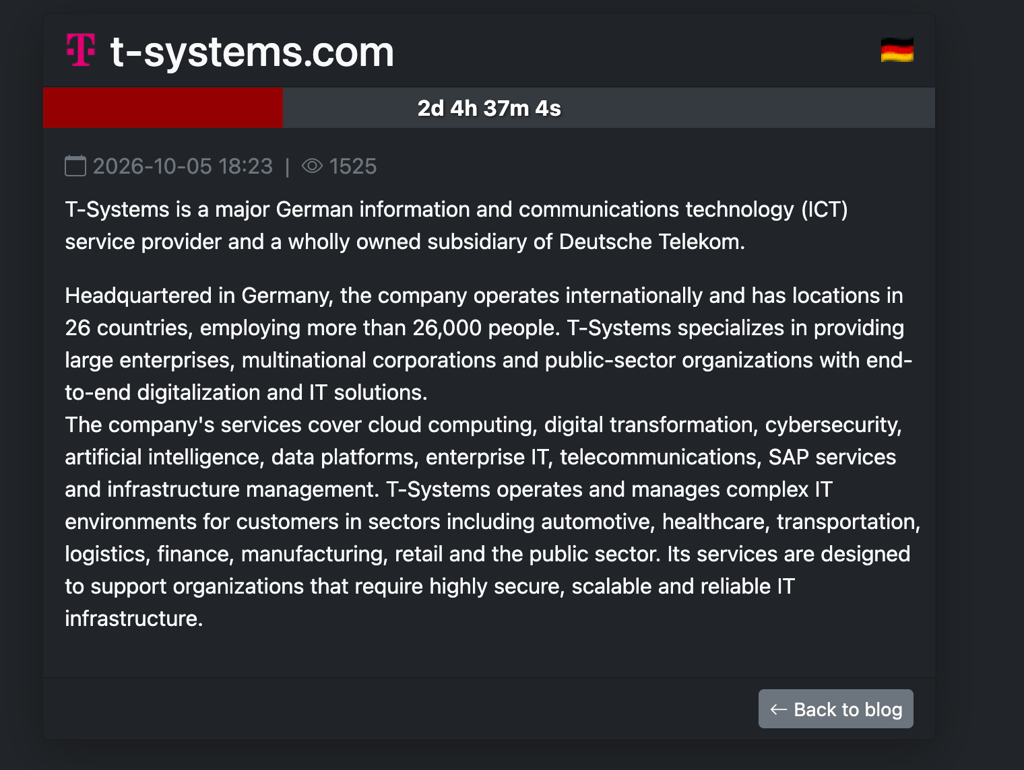
T-Systems is one of Germany's major enterprise IT providers and operates internationally, with locations across 26 countries and more than 26,000 employees.
Deutsche Telekom responds: Only the test environment was affected
A Deutsche Telekom spokesperson told Cybernews that, since October 5th, cybercriminals calling themselves Safepay have been trying to extort ransom money from T-Systems.
The company stated that the stolen data mainly includes slides for project presentations and system log files.
"These were stored on a test environment. At the beginning of September, Deutsche Telekom followed up on indications of Safepay's activities," the spokesperson said.
"Ransomware was found on a small test system, isolated and cleaned up before any significant damage could occur. The stolen data does not contain any sensitive information," they added.
Who is Safepay?
SafePay is a double-extortion ransomware operation first observed in the autumn of 2024, which rapidly grew into one of the most prolific ransomware groups globally.
SafePay explicitly rejects the ransomware-as-a-service (RaaS) model. It keeps a closed, in-house team that handles initial access, deployment, and extortion itself rather than recruiting affiliates.
Researchers assess, with varying degrees of confidence, that SafePay is linked to the Conti ransomware lineage. SafePay claimed breaches of 76 German companies in 2025, accounting for 25% of all German victim posts that year. In 2025, Safepay hit Ingram Micro Holding Corporation.
The Deutsche Telekom ecosystem has been targeted before
T-systems' parent company, Deutsche Telekom, has often been on the radar of cybercriminals.
In 2024, Deutsche Telekom was one of dozens of companies from around the globe posted on the infamous LockBit ransomware leak site.
In 2025, hackers claimed to have leaked 64 million records from T-Mobile. At the time, T-Mobile responded to Cybernews saying that the data hackers uploaded is not related to the company or its clients.
This May, hackers claimed that they had obtained a dataset belonging to Deutsche Telekom and put it up for sale. However, the company also denied that the data was real.
Updated on October 8th, [2PM GMT+3] with statement from Deutsche Telekom.

Check if your data was exposed
Find out if your email and related personal information have appeared in known data breaches.