US security firm N-able pulls the plug on N-central, its key platform, following disclosure of 33 zero-days
Compromising remote monitoring and management (RMM) servers could open doors for attackers to access many customer systems.

Image by Shutterstock
 Follow us
- N-able took hosted N-central environments offline after 33 critical flaws were publicly disclosed.
- Some reported exploit chains could let attackers steal credentials, create admin accounts, or fully compromise servers.
- N-able says it has not observed active exploitation, but urges customers to keep affected servers offline.
- Admins should review logins, privilege changes, scripts, configurations, and remote-control sessions from November 8 onward.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
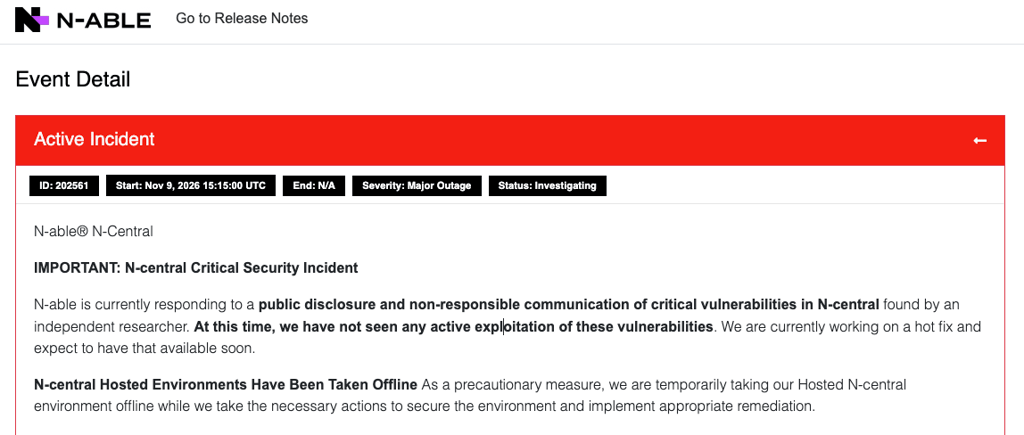
Hackers have publicly disclosed 33 critical flaws in N-central, a popular remote management platform that firms use to manage computers, servers, and networks. Its developer, N-able, has taken its hosted environments offline as a precaution.
On November 9, N-able, a US-based security company, shut down its N-central environments and urged customers with on-premises deployments to take their servers offline as well.
The firm believes the servers are at risk after an anonymous researcher publicly released proof-of-concept exploit code and technical details for 33 previously unknown vulnerabilities. Several exploit chains reportedly lead to full server compromise. Active exploitation hasn’t been observed in the wild yet.
“The disclosures affect the management platform itself. If the reported exploit chains function as described, they could provide a path to the systems, credentials, and administrative functions already trusted by N-central,” the company’s security advisor reads.

N-able is working on a hotfix and warns that compromising its Remote Monitoring and Management (RMM) servers could enable attackers to gain broad access to customer systems. They could leverage existing trust relationships to deploy malicious software, execute scripts, modify configurations, and steal credentials.
The scope of N-able’s response indicates the company considers the vulnerabilities capable of meaningful operational impact if exploited,N-able warns.
The hotfix is expected to land soon – the current estimate is mid-day on November 10, 2026.
What do we know about the vulnerabilities?
The vulnerabilities were disclosed by an independent researcher who goes by the alias BinaryNinja. They published the findings on a GitHub account named Oracle-Security. The account describes its operator as a security researcher and zero-day enthusiast, and says they are not affiliated with the company behind a reverse-engineering tool of the same name.
The repository lists 33 vulnerabilities, ranging from information leaks and weak access controls to flaws that allow attackers to execute commands. Exploitation of some flaws requires no authentication at all.
The researcher claims that multiple N-central zero-days enable anonymous credential theft, creation of an administrator account, and remote code execution with root privileges.
“All exploits were tested on their latest pre-release version,” the researcher posted on X.
Huntress, a cybersecurity firm, said three of the disclosed exploits lead to remote code execution, while one exploit leads to privilege escalation to root.
Many other bugs reportedly enable arbitrary file writes, traversal, credential disclosure, and other attacks.
N-able faced major security incidents earlier this year. In July and August, attackers exploited an authentication-bypass vulnerability (CVE-2026-18577) to gain administrative access to N-central and pivot to managed systems through the platform’s built-in remote management functionality.
In September, N-able addressed several more vulnerabilities, including a pre-authentication remote code execution bug that was later added to CISA's Known Exploited Vulnerabilities catalog.


Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
Better keep servers offline
N-able and other third-party security companies recommend keeping affected N-central deployments offline until remediation guidance and hotfix information are available. Customers who use N-able’s hosted service should expect an outage, as the infrastructure has been taken offline.
“Check whether N-central management interfaces are accessible from the public internet, and restrict access to dedicated administration networks wherever possible. Several of the published PoCs describe unauthenticated attack paths, so if they work as described, network reachability is a prerequisite for exploitation,” the advisory explains.
Admins should already be scrupulous and review login and authentication activity from November 8 onward for any unexpected access. Nable also recommends reviewing privilege changes, configuration modifications, software, scripts, remote-control sessions, and any other unexpected behavior.
The advisory lists additional systems that admins should investigate for potential secondary indicators of compromise.
“The work remains on track with no setbacks, and our teams are progressing as quickly as possible while maintaining the validation required for a safe remediation,” the latest update reads.