Hisense faces $5 million ransom demand over alleged 19GB data theft
A new extortion gang is currently listing 6 victims on its data leak site.
Hisense. Image by Robert Way / Shutterstock.
 Follow us
- WhiteArmor claims it stole 19GB of Hisense data and demands $5 million in Bitcoin.
- The alleged data includes Malaysia and Singapore warranty records with customer details, invoices, contracts, and supplier information.
- Hisense has not confirmed the breach, and the leaked sample was inaccessible at publication time.
- A Cybernews researcher says verified claims would mainly expose customer personal information and warranty data.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Hisense, a major Chinese electronics and home appliance manufacturer best known for TVs, has reportedly suffered a major data breach. A new ransomware gang, WhiteArmor, claims to have obtained 19GB of sensitive data and is demanding $5 million in ransom. The breach hasn’t been officially confirmed.
The threat actor has posted Hisense on its data leak site on the dark web, and the countdown timer leaves over 28 days for the company to react.
“Our demand is $5,000,000 in BTC. Good luck,” the post by WhiteArmor ransomware operator reads.
The threat actor has already released a small data sample of 348KB and is threatening to release the full 19GB archive, currently sealed. However, at the time of writing, the sample was inaccessible – the hosting server was not responding.
The hackers claim to have obtained “Hisense’s entire GCRM production document store, the full warranty-claims archive for Malaysia/Singapore: customer names, phones, emails, ID numbers, 2,549 suppliers, hundreds of invoices, payments, contracts, RMA forms, claim evidence, plus their internal CRM app binary.”
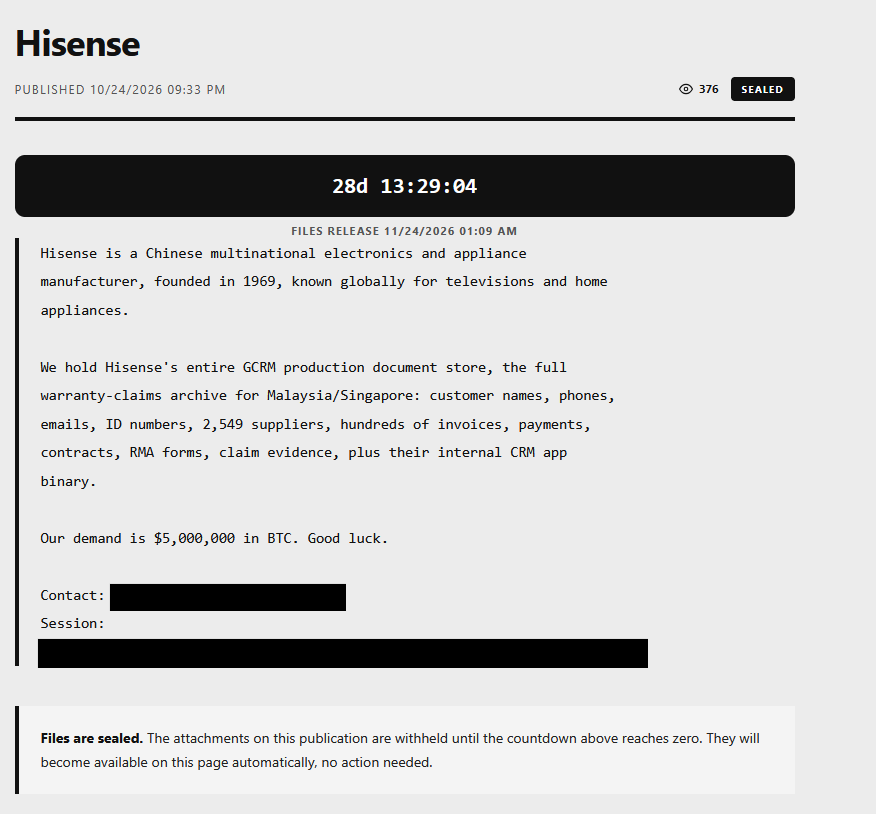
Some posts on X suggest that the attackers increased their demands from an initial $500,000.
Cybernews has reached out to Hisense for comment and will include its response.
“If claims are true, the impact is limited to warranty claims for Malaysia/Singapore, together with customer details,” noted Aras Nazarovas, security researcher at Cybernews.
“It mostly affects the confidentiality of customers’ personally identifiable information, such as names, phone numbers, email addresses, and invoices.”
The attackers could potentially reverse-engineer the CRM app binary to target Hisense’s warranty claims processing systems with return fraud or to extract additional customer PII.
WhiteArmor is a new data-theft and extortion group that emerged only a few days ago – the first victim was claimed on October 21st, 2026. Currently, its data-leak site lists 6 victims.
The operator charges its affiliates only a 5% fee on successful ransom payments. DarkFeed, a cyber threat intelligence platform, reported that the threat actor is recruiting pentesters, web exploitation experts, and zero-day researchers. However, its claims remain unverified.
Ernestas Naprys is a senior journalist at Cybernews covering information security, open-source software, hardware, data breaches, vulnerabilities, hacking, and digital privacy. With 12 years of journalism experience, his reporting combines technical research with hands-on experimentation, helping readers understand complex cybersecurity risks and technologies. Before joining Cybernews, Ernestas worked as a financial markets reporter at Verslo Žinios and as a business journalist at 15min and DELFI. He was recognized as Lithuania's Journalist of the Year in 2018 for his analysis of EU investments.