KillSec suspected leader unmasked as teen after police seize notorious leak site
The ring leader may be as young as 16 years old.
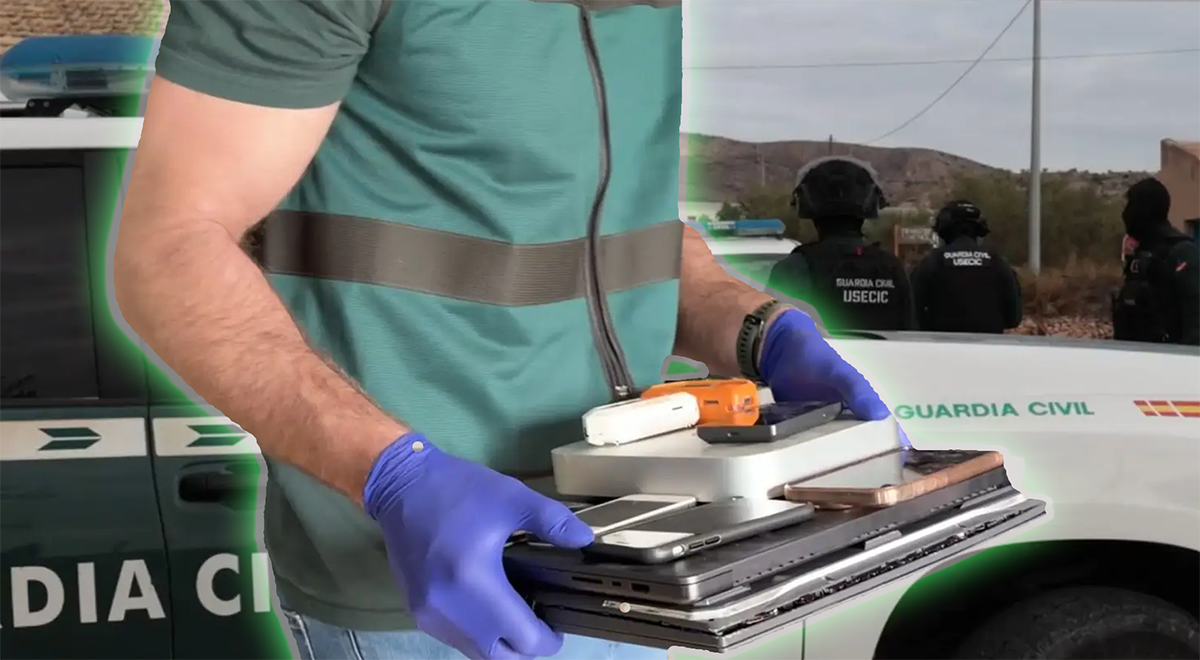
Enforcement seizes KillSec servers and leak site. By Europol/Illustration by Cybernews
 Follow us
- European authorities seized KillSec’s leak site and secured at least 110 terabytes of data.
- Authorities identified a 16-year-old as the suspected administrator and main operator.
- Three other suspects were arrested, and searches took place in 4 countries.
- KillSec stole data and threatened to publish files unless victims paid ransoms.
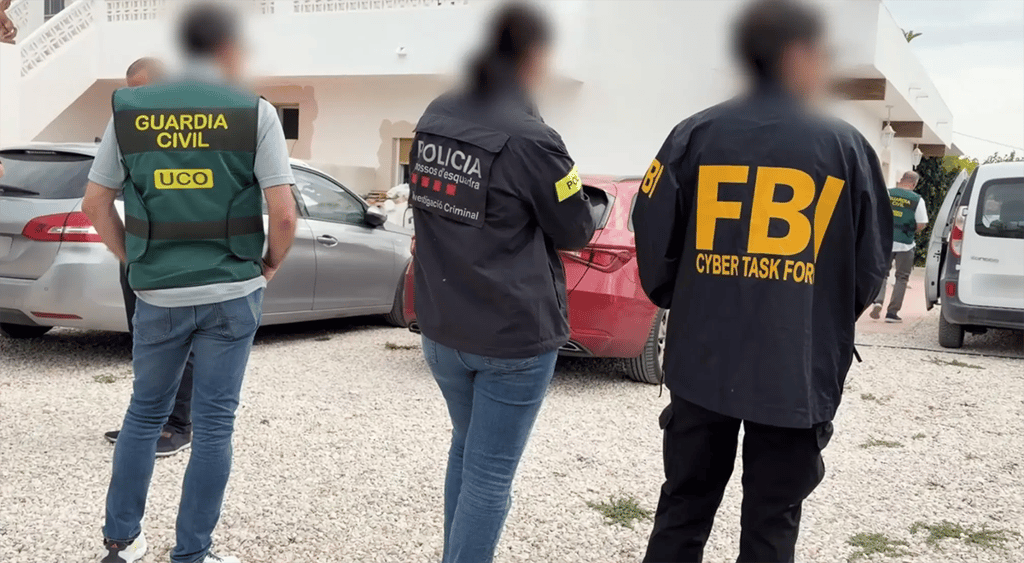
KillSec, the ransomware gang responsible for thousands of global attacks, has been disrupted by law enforcement after officials seized its leak site and made multiple arrests.
An operation led by European authorities took control of KillSec’s leak site and secured at least 110 terabytes of data surrounding further hacks.
The group used the site to threaten organizations with data leaks unless they paid a ransom.
Authorities have identified a 16 year old as the main suspect behind the operation, who worked as KillSec’s administrator and main operator.
Daniel Wilcock, threat intelligence analyst at Talion Cyber Security told Cybernews that the operators age is a real cause for concerns.
"Many of the ransomware operations today consist of young kids, and we must ask why they are choosing careers in crime over legitimate careers in cyber defense."
Not enough is being done to deter young children with "expert technical skills" from a life of cybercrime and additionally, young people may be attracted to cybercrime because it's lucrative.
"Hearing that a 16-year-old was behind one of the world’s most dangerous ransomware operations is highly concerning and, quite frankly, a complete waste of what could have been a promising career," Wilcock told Cybernews.
Another 3 suspects were arrested, including a suspected developer who turned 18 years old in August and was a minor when the offenses took place.
“Investigators also identified one person believed to be in a negotiator role and another in an affiliate role. Inquiries into other possible members are continuing,” according to Europol.
Alongside the arrests, 8 properties in Greece, Romania, Spain, and the United Kingdom have been searched.
Law enforcement also investigated the group’s finances and criminal proceeds.
Who is KillSec?
KillSec became active around 2024, exploiting vulnerabilities and poorly secured access points to steal data from organizations and then hold it for ransom.
The group is responsible for hundreds of successful attacks on which have cost victim organizations millions of dollars in damages, not just in ransom payments but in operational disruptions and perhaps reputational damages.
Its victims would then be named on its dark web leak site and threatened with exposure unless the victim organization paid up.
If the victim didn’t pay, the stolen files would be made available for free download.