LA freeway sign hijacked to doxx political dissidents in latest Iran-linked hacking
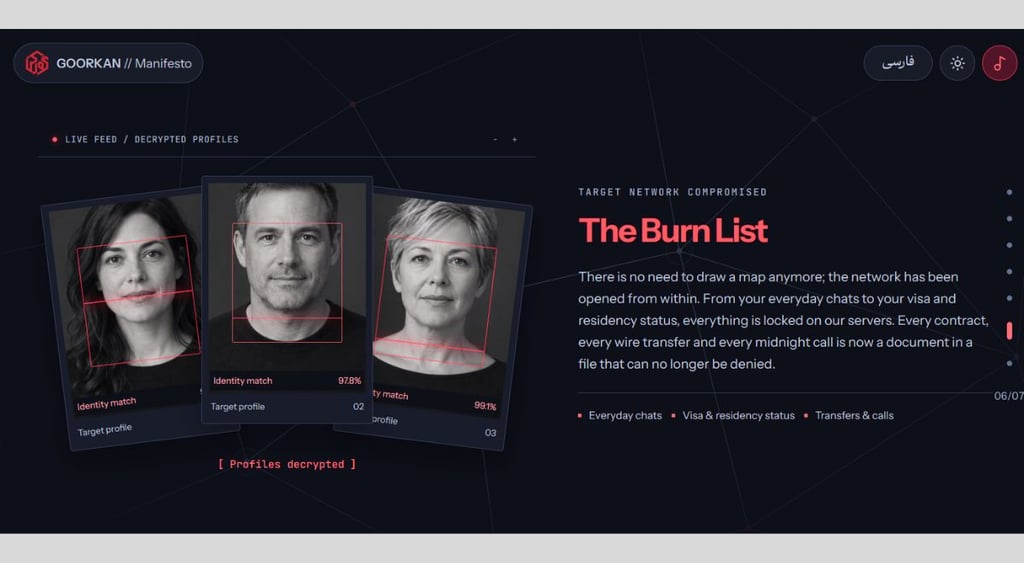
The hackers allegedly possess a “Burn List” outing names, faces, and personal information of Iranian dissidents – including some local residents.
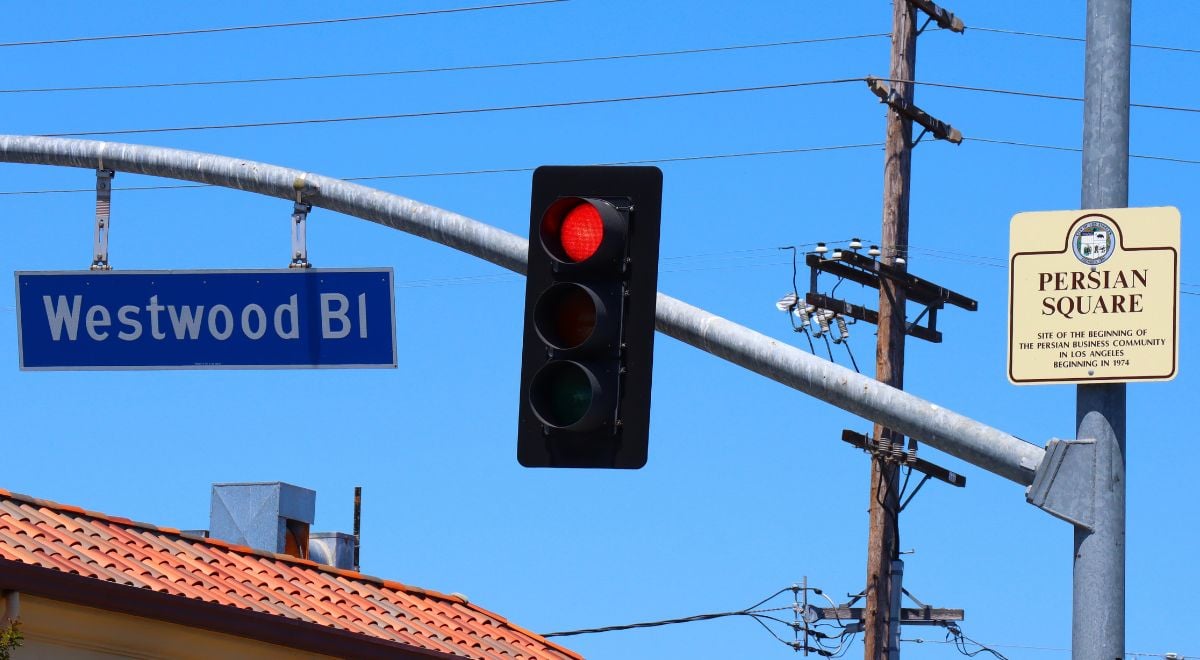
Image by Walter Cicchetti | Shutterstock
 Follow us
- Hackers hijacked a digital sign on the I-405 near LA's well-known Persian enclave, stoking fear among the Iranian diaspora.
- The sign promoted a website known for publishing the names, photos, and personal details of Iranian dissidents – including some living in LA.
- The unauthorized freeway message went unreported for a week.
- A linked Telegram channel asks followers to submit information about people it accuses of treason.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
An LA freeway sign – located near a well-known Persian enclave in the city – was hijacked by pro-Iranian hackers, flashing the URL of a website used to expose the names and faces of Iranian dissidents worldwide.
The unauthorized digital message – spelling out the website address Goorkan[.]com – was first seen by a driver traveling north on the I-405 at the Santa Monica Boulevard exit, just south of the Westwood community district on Tuesday, September 8th, according to the New York Post.
The website is known for publishing names, photos, and personal information on members of the Iranian diaspora who oppose the current regime.
For those unfamiliar, Westwood is a neighborhood in LA populated by Iranians, many of whom emigrated to the US during the 1979 Islamic Revolution, and even boasts its own Persian Square. An estimated 141,000 Iranian Americans live in LA County, the Post says.
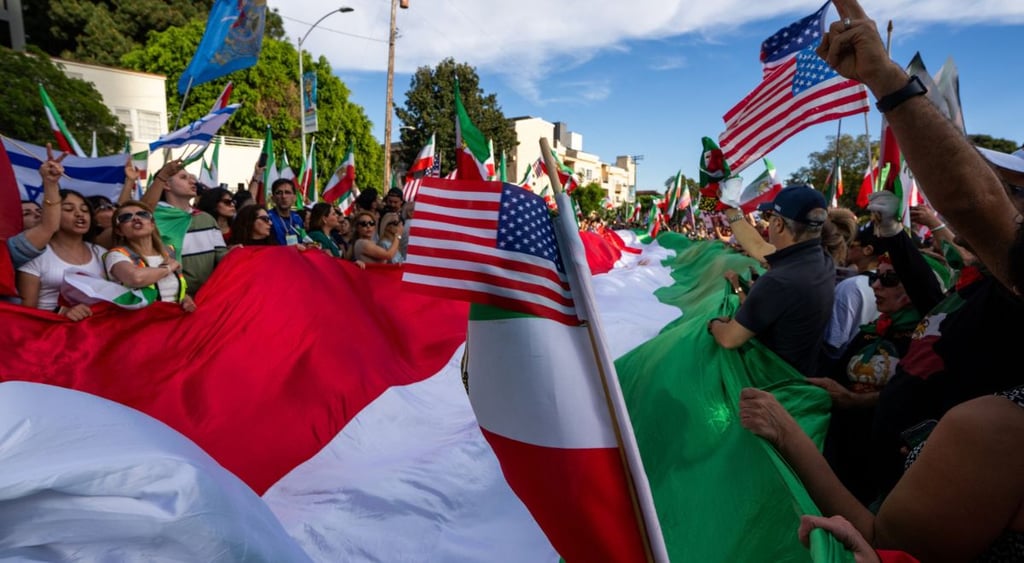
Its main drag, Westwood Boulevard, is a hotbed for anti-regime demonstrators, who took to the streets earlier this year to celebrate the death of the Ayatollah Khamenei and support the US-Israel War in Iran.
The hijacked sign was up for a full week before it was reported to the California Department of Transportation (CALTRANS), which, in a statement sent to Cybernews, said it quickly addressed the incident.
This Portable Changeable Message Sign (PCMS) unit is one used for the I-405 Sepulveda Pass Pavement Rehabilitation Project.the California Department of Transportation (CALTRANS) told Cybernews.
The Caltrans project team was alerted to the unauthorized message Sept. 15, and alerted the contractor to restore normal operations,
CALTRANS, which also says it is now investigating the sign's access history, listed the joint contractors as C.A. Rasmussen, Inc. and FBD Vanguard Construction, Inc.
What is Goorkan?
The website “Goorkan” – translated from Farsi to “Grave Digger” in English – describes itself as an intelligence ecosystem dedicated to doxxing Iranian dissidents, who are also accused of being agents for Israel.
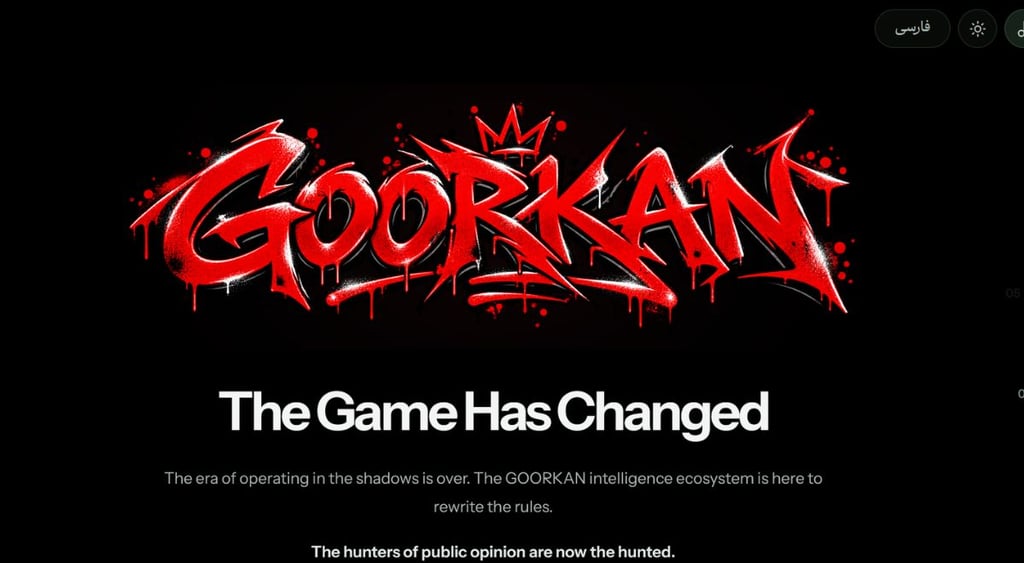
The site, which boasts its own Burn List of targeted dissidents, also calls Iran “A nation with zero history of aggression.”
From your everyday chats to your visa and residency status, everything is locked on our servers.Goorkan claims about its alleged "Burn List."
Every contract, every wire transfer, and every midnight call is now a document in a file that can no longer be denied,
At least one member of LA's Iranian community has already reported finding her own name, photograph, and personal information on the Goorkan website, according to the New York Post report.
Iranian-born Los Angeles resident, Emel Karsaz (pictured in X post above), told the newspaper she reported the incident to the FBI following the discovery and after receiving threats on social media.
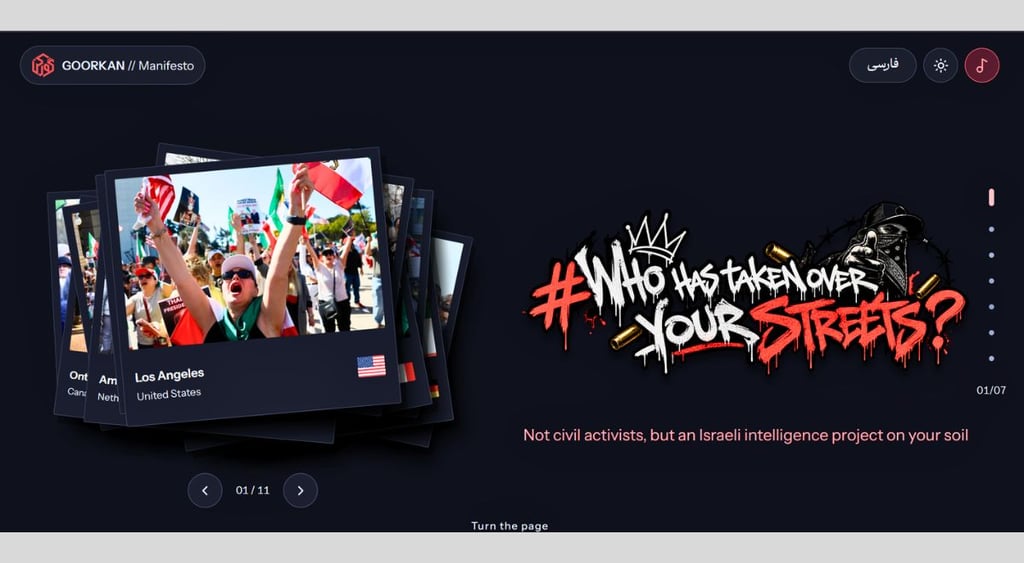
Meanwhile, whoever is behind the Goorkan website also appears to be operating a Telegram channel used to solicit information about people abroad, publish allegations against identifiable individuals, and advertise alleged arrests.
On September 1st, the channel announced a "National campaign to identify and expose traitors to the homeland."
The text, translated from Farsi, describes a collective effort to identify and expose people it accuses of treason and supporting hostile actions against Iran.
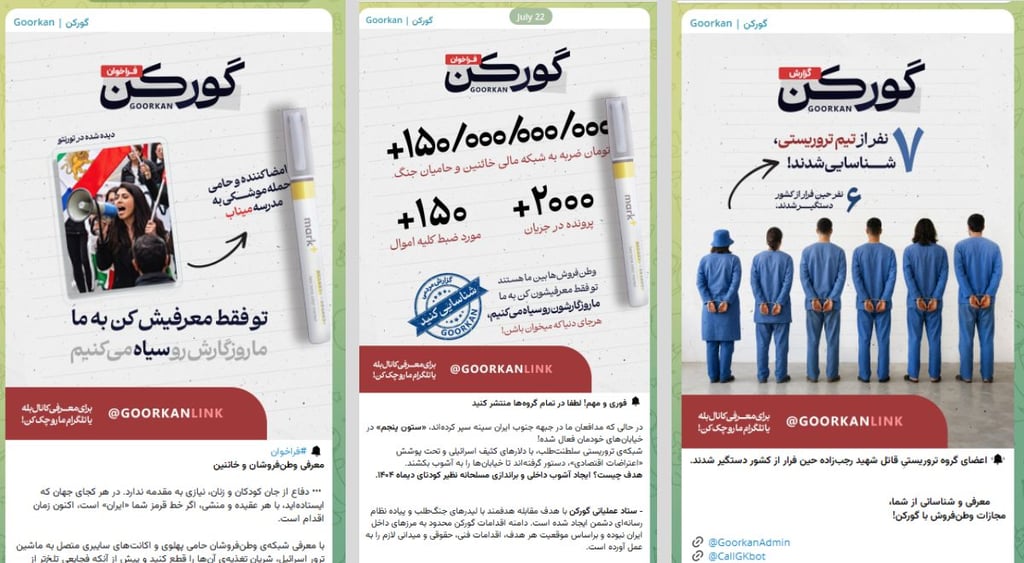
Alarmingly, the post provides two links, asking its followers to submit information or view profiles.
The text says: "Just introduce them to us. We'll take care of the rest."
In another post, the channel identifies a woman photographed at a demonstration in Toronto, accusing her of organizing and supporting the unintentional US bombing of an elementary school in Southern Iran back in February.
Iranian dissidents increasingly targeted abroad
The campaign is just one of many cyber espionage efforts launched by Iran-aligned hackers over the years, with some directly linked to Iran’s own Ministry of Intelligence and the Islamic Revolutionary Guard Corps.
Last week, the US, UK, and Dutch cyber authorities warned of a new malware deployed by Iranian-linked hackers to spy on dissidents, activists, and journalists living in the Western nations and abroad.
The spyware – dubbed Chosen Brick and built with Telegram infrastructure – enables Iranian state actors to collect information on a target’s contacts, emails, social media messages, screenshots, and even microphone audio – all of which could allow location tracking.
The hackers are said to use spear-phishing tactics, gaining the target's trust before tricking them into opening a malicious link on their devices and installing the spyware.
In one case, the hackers even sent a fake set of MRI scans as a phishing lure.
Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.