Hackers claim they breached Disney: here’s what we found
Over 2,500 records were allegedly leaked from the Pixar, Marvel, and Star Wars owner. There could be more.
Image by Dado Ruvic | Reuters
 Follow us
- WhiteArmour ransomware gang claims on a hacker forum that it breached the Disney staff directory data
- Cybernews reviewed a sample with nearly 2,800 records containing names, work emails, and internal IDs.
- Many emails appear tied to Disney-owned businesses, especially ABC News; ESPN also appears in the sample.
- Exposed records could help criminals send targeted phishing messages to Disney employees.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
One of the most recognizable names in the entertainment industry has been claimed by hackers.
Disney, or Walt Disney Company, is known worldwide for its iconic animated and live-action films, beloved characters like Mickey Mouse, global theme parks and resorts, and massive media franchises such as Pixar, Marvel, and Star Wars.
The mass media conglomerate was recently claimed by WhiteArmour ransomware. The alleged attackers are trying to gain attention by putting Disney employee data on a well-known hacker forum.
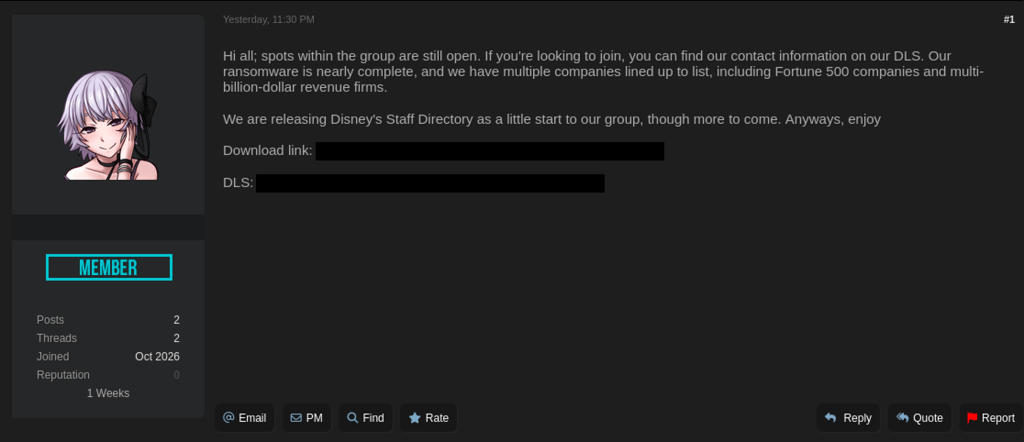
“We are releasing Disney’s Staff Directory as a little start to our group, though more to come. Anyways, enjoy,” the attackers wrote in a post, adding that more victims, including Fortune 500 companies, are "lined up" for its leak site.
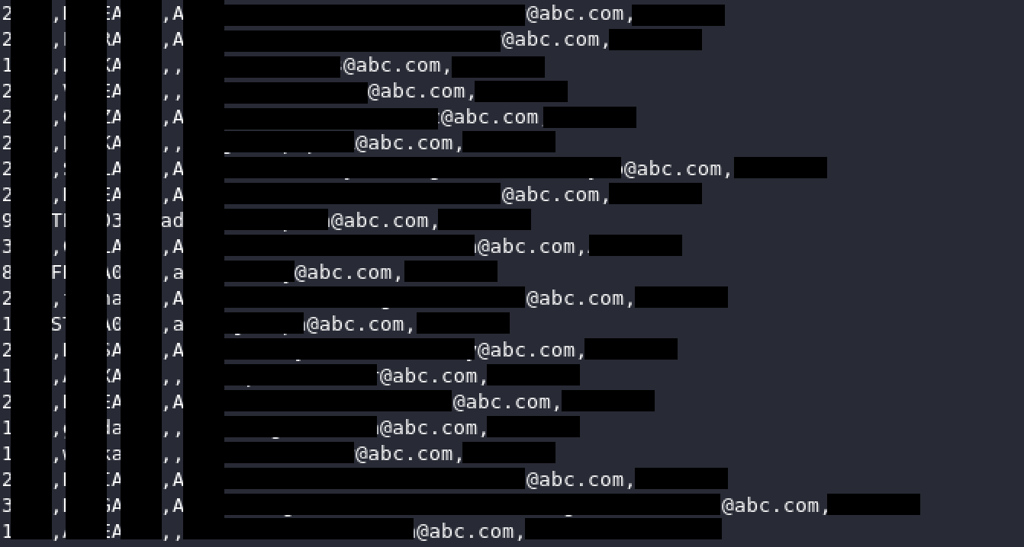
We examined a data sample of the allegedly stolen information provided by the attackers. A CVS file contained nearly 2,800 records containing full names, internal system IDs, and work email addresses associated with Disney and several of its subsidiaries.
The apparent authenticity of the records lends weight to the possibility that the data is genuine.
However, in the forum listing, there's no claimed count or record size, nor a set price. It is likely that the gang will operate as a run-of-the-mill ransomware gang, primarily contacting affected companies for money.
“Most emails in the dataset are not from Disney directly, rather from various companies owned by Disney, the largest portion being ABC News,” Cybernews researchers said.
Other names appearing in the sample included Disney itself and ESPN.
Increased risk of targeted phishing attacks
Exposed employee information can provide attackers with a starting point for more targeted phishing campaigns.
A collection of employee records from across Disney businesses could give attackers a more detailed picture of the people working inside the organization.
With names, corporate email addresses, and internal identifiers, criminals could attempt to craft convincing phishing messages that appear to come from colleagues or IT departments.
According to our researchers, Disney employees should be cautious of unsolicited messages that use real names, reference internal work details, or request login credentials.
We’ve reached out to Disney and will update this article once we receive a response.
Has your password leaked?