Amadeus breach compromises 116,000 Finnair bookings
The airline assures payment card data and passwords weren’t accessed.
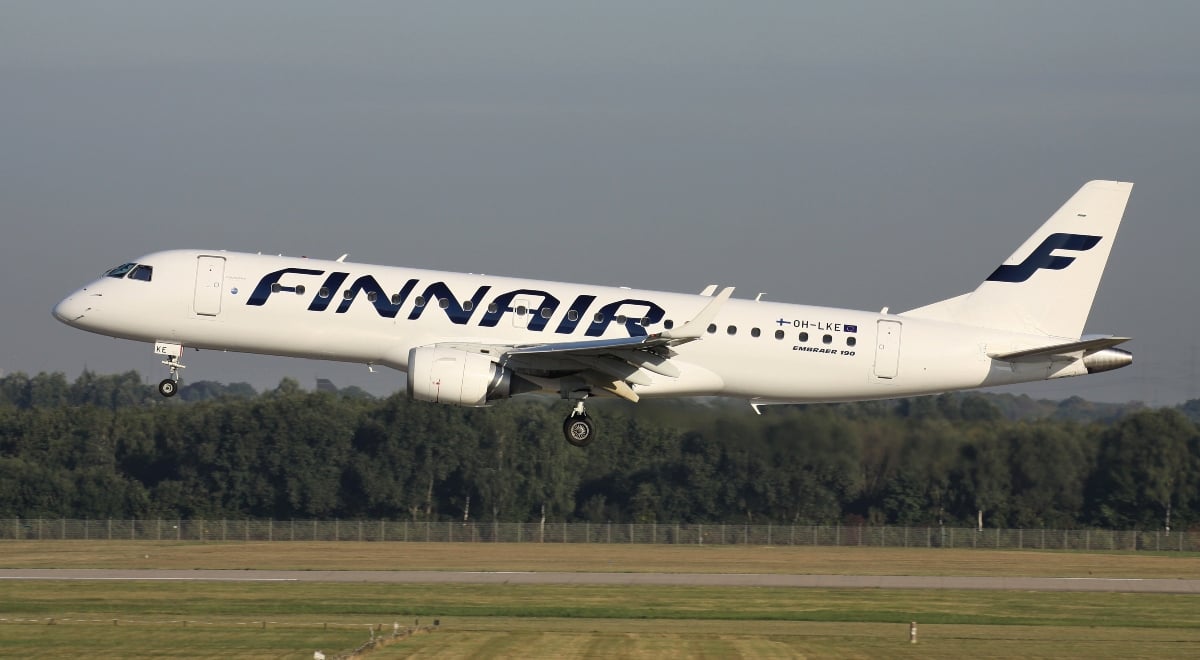
Finnair customer data exposed. By Shutterstock.
 Follow us
- Amadeus told Finnair that about 116,000 bookings were involved in the breach.
- Finnair says its own systems were not compromised, and Amadeus confirmed no credit cards or passwords were accessed.
- Around 750 Finnair reservations were opened for examination, including 30 linked to Aurinkomatkat travel packages.
- Finnair issued new booking numbers for active affected reservations to reduce the risk of misuse.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
At least 116,000 Finnair reservations have been compromised in a huge data breach connected to Amadeus, a third-party software vendor that supplies the Finnish airline with its booking and flight management systems.
Finnair says Amadeus informed the airline of a data breach involving flight lists of several airlines, including approximately 116,000 Finnair bookings.
The data breach is believed to have taken place over a three-year period between August 2023 and September 2026.
However, Amadeus, one of the world’s largest suppliers of airline technology solutions, didn’t begin informing airlines that they had been caught up in the breach until late October.


We have demanded detailed clarification of this incident from Amadeus,said Finnair’s chief information security officer, Timo Arndal.
“A detailed investigation is still ongoing, but Amadeus has already confirmed to us that credit card numbers or passwords have not been accessed. Finnair systems have not been compromised,” Finnair’s press release states.
Amadeus further told the airline that roughly 750 Finnair reservations “have been opened for examination.” Of these, 30 are related to the airline’s Aurinkomatkat travel packages.
In October, Amadeus stated that it had discovered a vulnerability “affecting a travel booking display environment” and that “certain booking-display data” was accessible through the flaw.
Seven airlines among victims
The good news is that the unauthorized activity has been contained. According to Finnair, only a fraction of the examined reservations are still active, and the company has issued new booking numbers for them to prevent potential misuse.


Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
Many of the processes passengers use, like booking a flight on an airline’s website, managing a booking, or checking in for a flight, run in the background on Amadeus Altéa platform.
Finnair is now the seventh major global airline to come forward as a victim of the data breach at Amadeus. Other airlines caught up in the incident include Singapore Airlines, Cathay Pacific, ANA All Nippon Airways, Japan Airlines, Korean Air, and Condor.
The variety of information exposed in the breach included booking references, names, and flight details, as well as passenger email addresses, phone numbers, travel documents, and frequent flyer numbers in a smaller number of cases.
Passengers who believe their personal data has been compromised are advised to change their passwords, enable multifactor authentication, and carefully monitor any accounts that could have been exposed.