Dutch police take down malicious proxy network exploiting 178,000 devices
The hackers were hiding in plain sight until the cops showed up.
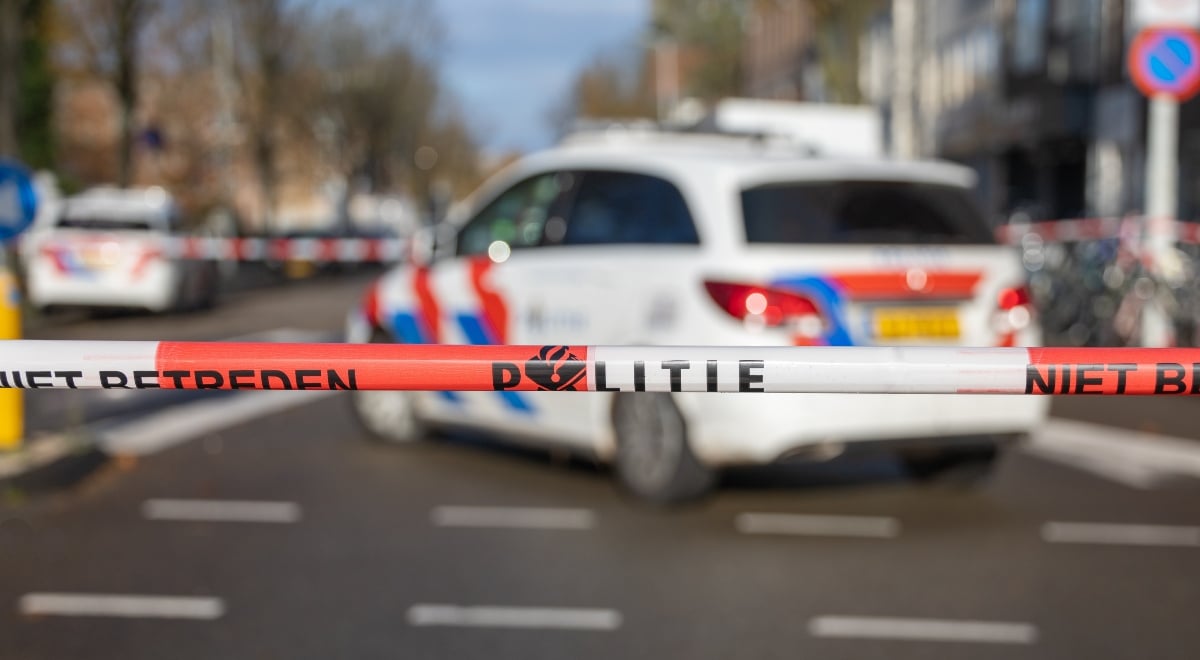
Netherlands police. Photo by Robert Coolen/Shutterstock
 Follow us
- Dutch police and partners took down a proxy service made of 178,000 compromised devices.
- Criminals used the service to hide behind internet addresses belonging to innocent citizens and businesses.
- Police seized servers at multiple hosting providers, and more server takedowns may follow.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
The Dutch National Police, the Netherlands Public Prosecutor’s Office, and the Shadowserver Foundation have taken down a malicious proxy service consisting of 178,000 compromised devices.
Through the proxy service, criminals were able to exploit the IP addresses of innocent citizens and businesses.
A proxy server is a computer that acts as an intermediary between a user and the internet, forwarding requests through another server to improve privacy and control access. Proxy servers help to hide a client’s public IP address and conceal their online identity and location.
Cybercriminals love using proxy servers for their illegal activities because it’s very hard to track their internet traffic back to them.
A proxy server can also be used to bypass geographic restrictions on the internet. This can come in handy, for example, when you want to watch a Netflix movie that’s only available in a different region.
Lastly, a proxy server can also be used to forward sensitive or confidential information, and you don’t want the intelligence services of an authoritarian regime to find out.
This shows that a proxy service doesn’t have to be illegal. However, if it’s used by criminals to conceal their identities and criminal activities, it is.
This makes it more difficult to track down and prosecute offenders. On top of that, it makes it appear that a criminal act was committed by the owner of a compromised device.
According to the Dutch National Police, the proxy service that was taken offline comprised 178,000 infected devices. How the devices got infected hasn’t been disclosed.
“Users of the service could connect to the internet via these devices without the owners’ knowledge. This means that if criminals were to use the service to commit cybercrimes, the IP addresses of innocent citizens and businesses could be wrongly flagged as suspicious in criminal investigations,” the police stated in a press release.
Multiple hosting providers targeted
To dismantle the proxy service, police officers took down servers at multiple hosting providers last week, with more servers to follow in the near future.
Users who try to visit the proxy service’s site will get to see a splash page that says that “this website has been taken down” by the Dutch National Police, the Netherlands Public Prosecutor’s Office, and the Shadowserver Foundation, a nonprofit security organization that helps to make the internet more secure for everyone.
“Cybercrime is not combated solely through investigation and prosecution. By gathering and analyzing data and through national and international cooperation, the police disrupt the operations of cybercriminals to prevent victims,” the Dutch National Police concluded its press release.
Earlier this year, the Dutch National Police, together with the FBI, managed to take the proxy service SocksEscort offline, which quietly hijacked 369,000 WiFi routers and other devices and helped hackers to hide their internet traffic behind residential IP addresses.