FBI hack: ShinyHunters countdown ticks down, claims "we got what we wanted" in new post
ShinyHunters insists the FBI hack is “NOT financially motivated” and “NOT a ransom,” as the hackers give the agency five days to comply with its demands.
Miguel Candela/SOPA/LightRocket/Getty Images

Key Takeaways by nexos.ai, reviewed by Cybernews staff.
The ShinyHunters extortion group – which earlier this week claimed to have compromised several FBI servers as payback for spreading “false information” about the gang – has now posted its “Final Statement” to the federal law enforcement agency on its dark leak site.
The hackers confirmed the new statement to Cybernews in an email on Thursday.
ShinyHunters initially claimed responsibility for the breach in an extensive message on its onion site Monday – calling out the FBI for publishing misinformation about how the group operates and disputing the FBI's characterization of behaviors such as harassing, pressuring, and exaggerating access to victims’ data.
With 48 hours now gone, the gang initially gave the FBI a seven-day deadline to remove the information off the web, or face unknown consequences.
ShinyHunters issues "final statement"
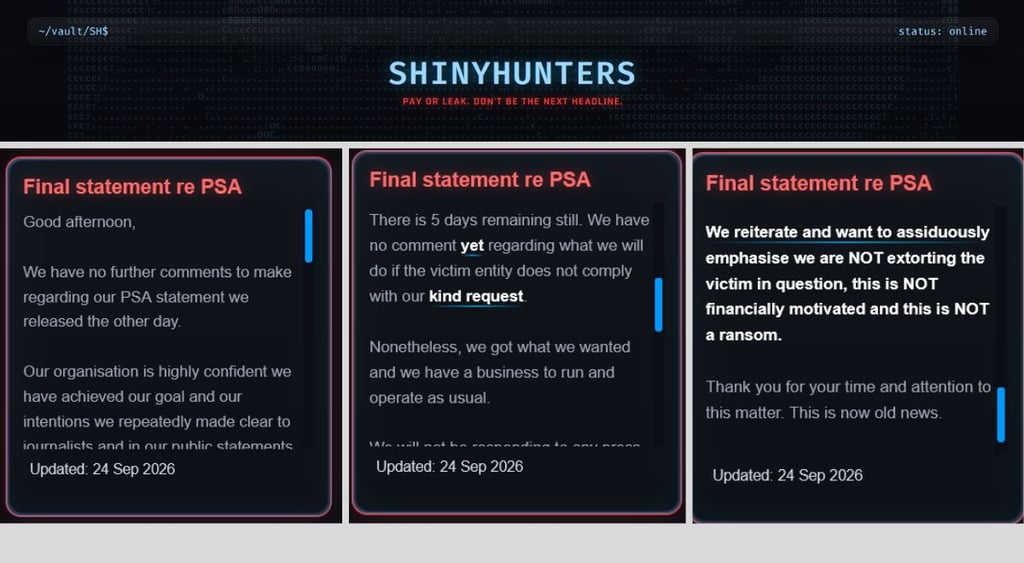
The new message, which it calls a “PSA” – an obvious nod to the FBI’s own public service announcement from May that ShinyHunters has a problem with – basically states that the group has “no further comments” and “will not be sharing updates” about any other undisclosed datasets.
Our organisation is highly confident we have achieved our goal and our intentions we repeatedly made clear to journalists and in our public statements.ShinyHunters said in a new post published to its leak site on Thursday.
There is 5 days remaining still. We have no comment yet regarding what we will do if the victim entity does not comply with our kind request.
Nonetheless, we got what we wanted and we have a business to run and operate as usual,
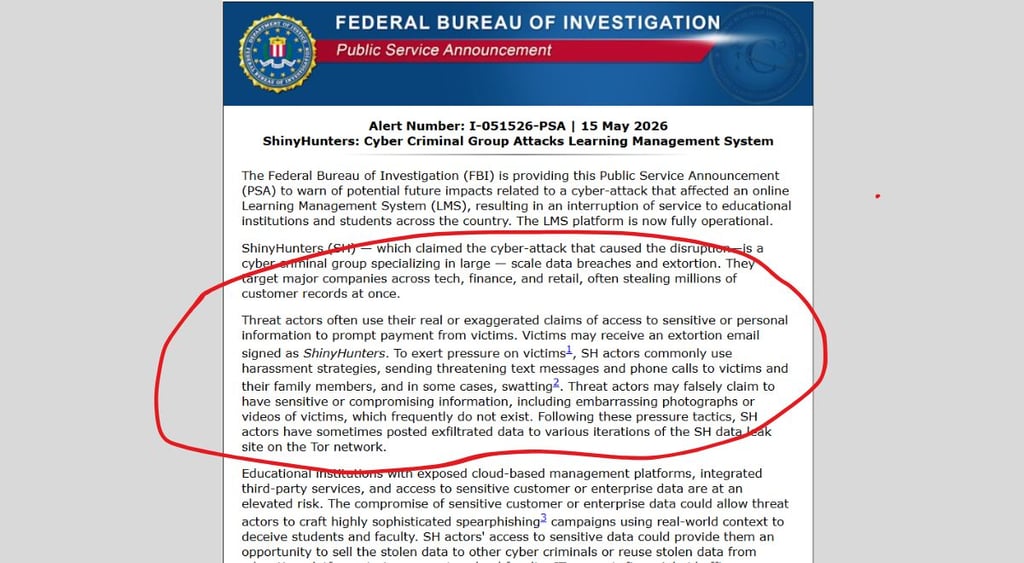
Seeking further clarification, Cybernews asked ShinyHunters why the original FBI post was taken down from their dark leak site, to which the hackers responded on Thursday, “We advise you read our new and final statement regarding this matter.”
FBI’s secretive hacking unit exposed
The alleged cache is reportedly anywhere from 2TB to 3TB – with researchers at 404 Media confirming a proof sample containing data on about 5,000 FBI agents.
ShinyHunters told Cybernews on Monday it had stolen sensitive data encompassing “almost all” FBI agents, employees, and job applicants who applied through the FBI jobs web portal.

A more extensive analysis by 404 Media, released on Thursday, shows that besides exposing FBI agents' “addresses, phone numbers, and even their spouses,” the stolen information appears to include “members of the FBI’s secretive hacking team” – an elusive unit that remains in the shadows due to the clandestine nature of the tools it uses.
404 Media said it identified three records referencing the FBI's Remote Operations Unit (ROU), including one with a phone number reportedly linked to a person associated with the Secret Service and another identified as a “student workforce trainee.”
ShinyHunters additionally told Cybernews that the stolen job applicant data includes:
- Full personally identifiable information (PII)
- Background information
- Educational data: Specific grades and degrees
- Former US government employment information
- Serious and sensitive medical and drug-related information
- More stuff we can go on and on for
The group also told Cybernews it broke into FBI systems “immediately after discovering a new z-day [zero-day] in Oracle PeopleSoft” enterprise software.
Oracle has not responded to our request for comment.
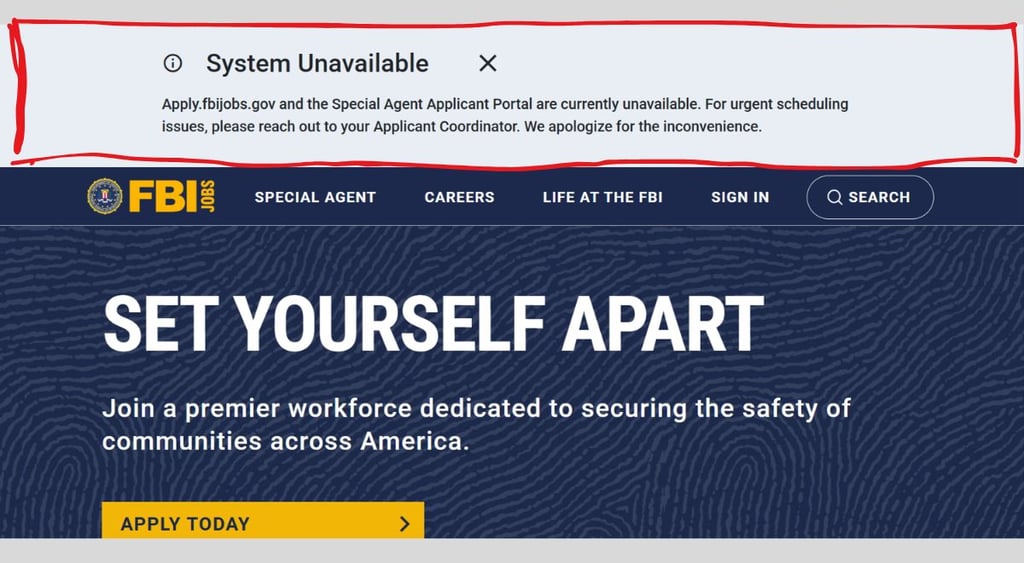
Notably, both the FBI’s job and application online portals are still unavailable as of Thursday.
FBI "actively investigating" breach claims
The FBI told Cybernews on Monday it was “aware of the claims regarding unauthorized activity affecting FBIjobs.gov” that it is currently investigating.
While the point of breach is still undetermined – whether a third-party or the FBI’s enterprise – we are actively and aggressively investigating this matter and working closely with those third-party providers that support fbijobs.gov to mitigate any and all risk,the FBI said in a separate statement released on Wednesday.
Cybernews has reached out to the FBI for comment on the gang’s latest post but has not heard back at the time of this report.




Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.