Russian hackers compromised Microsoft Exchange to steal NATO, EU emails
ESET says the cybercriminals used a previously unknown toolkit called Cereal.
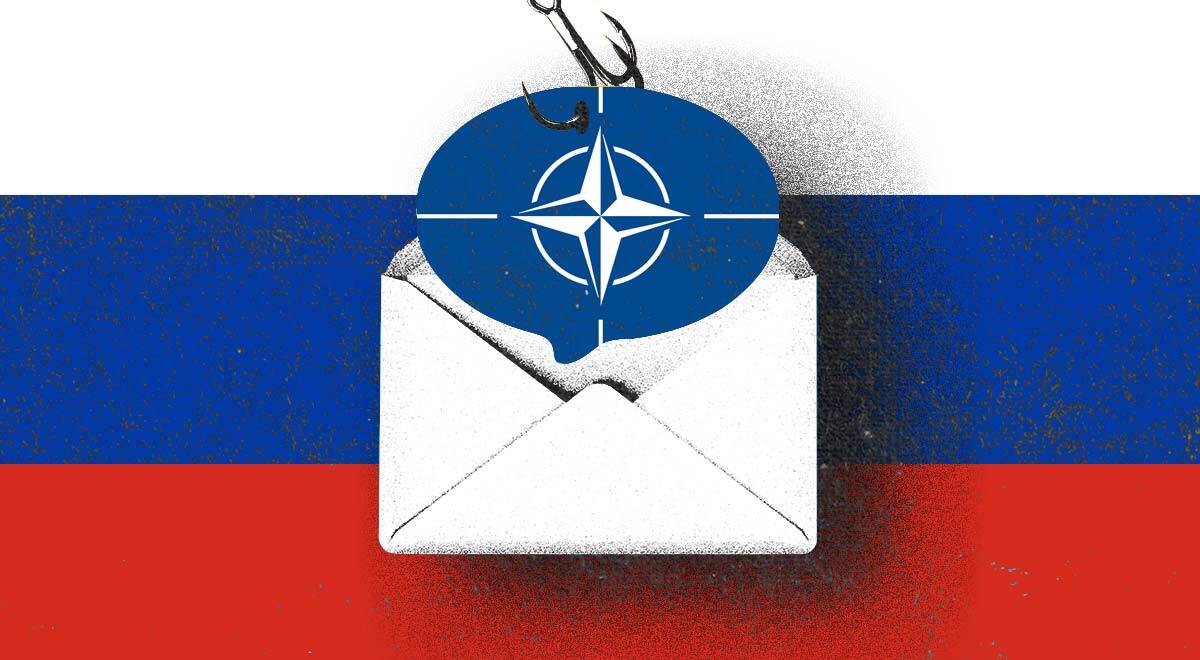
Russian hackers compromised Microsoft Exchange to steal NATO, EU emails. By Cybernews.
 Follow us
- ESET says Russian-linked Turla compromised Romanian government Microsoft Exchange servers.
- The new Cereal malware can copy selected emails involving NATO and EU officials.
- The hackers used the victim's Exchange server as a control hub to avoid external infrastructure.
- Researchers do not know how the hackers got in or how much data they stole.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Russian state-sponsored hackers breached government email servers in Romania using new malware to intercept messages, including emails sent to and from NATO and European Union officials.
According to cybersecurity company ESET, Turla, a Russian cyber espionage group closely linked to the country’s Federal Security Service (FSB), is behind the compromise.
Interestingly, the group used a previously unknown toolkit called Cereal to monitor email traffic, steal particular messages, and then maintain access to compromised Microsoft Exchange servers without detection.
“The Cereal toolset is a carefully constructed instrument for long-term, stealthy cyberespionage. It leaves little on disk, avoids external infrastructure that could be discovered and blocked, and conceals itself within legitimate Exchange processes,” said ESET.


Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
The toolkit is highly stealthy. When an official sends an email to a colleague in another NATO country, the message goes out through a Microsoft Exchange server without raising suspicion.
But before the email leaves the building, a piece of code quietly examines it, decides that it is interesting, and sets aside a copy to be forwarded to prying eyes, while the original email continues on its way,ESET explained in a blog post.
That precise scenario was uncovered by the cybersecurity firm late last year. The toolset that installs such code on an Exchange server of a governmental organization was found in Kazakhstan.
The same toolset was soon discovered at a governmental organization in Romania – compromised on December 23rd, 2025 – where it was configured to identify emails sent to or received from NATO and the EU.
Novel hacking technique
According to ESET, what makes this toolset stand out is its combination of novel techniques requiring deep knowledge of Exchange internals with unusual .NET execution methods.
One of the most interesting aspects of this toolset is what the researchers didn’t find: external command and control (C&C) infrastructure.
Has your password leaked?
Instead – adding insult to injury – the victim’s compromised Exchange server is co-opted to act as the C&C hub. This allowed Turla to operate without relying on external servers that could be detected, blocked, or shut down.
“Abusing a compromised Exchange server as a central operational hub is a rare technique, used by only a handful of APT groups. Turla has used variations of this approach in the past,” ESET noted.
The technique has not previously been documented in other malware families. However, it remains unclear how the hackers initially gained access to the government servers or how much data they extracted.
Turla, also known as Snake, has been active since at least 2004. It usually targets governments, diplomatic missions, and defense organizations across Europe, Central Asia, and the Middle East.
The group was previously found to be extensively surveilling foreign embassies, diplomatic missions, and other sensitive organizations in Moscow. In that case, the attackers utilized internet service provider (ISP)-level access.
Interest in Romania might be related to regional tensions. Since early 2025, Romania has been reporting incidents involving Russian drones crashing near or within its territory.
The Kazakh compromise occurred just as the country began deporting some Russian exiled and regime critics who fled Russia after it invaded Ukraine in 2022.