Telegram warning: Hackers could run code through Android calls
You do not want to answer this call.
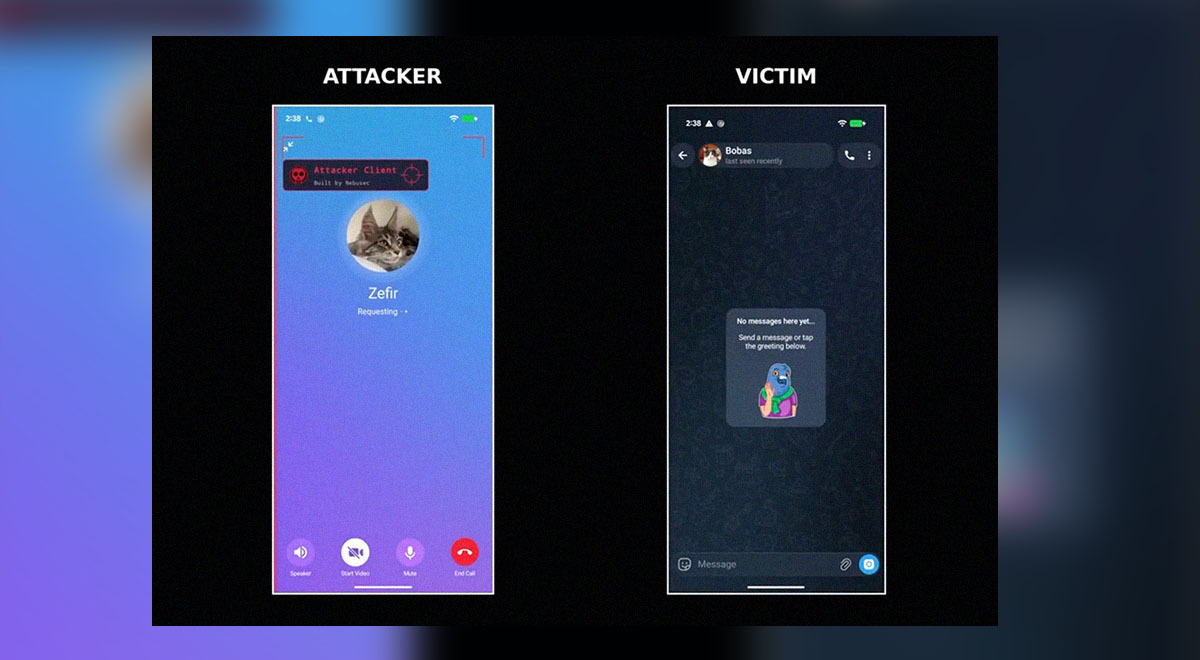
Image source: Nebusec
 Follow us
- NebuSec says attackers could exploit Telegram Android call handling by convincing a victim to answer a voice call.
- The flaw reportedly went unnoticed for four years in code used to manage voice and video calls.
- Telegram for Android versions 8.6.2 through 12.10.3 are affected, according to NebuSec.
- Users should update Telegram for Android to version 12.10.4 or later and check Settings for their version.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Answering a routine Telegram call could have allowed hackers to take control of an Android phone, a security company finds.
A Telegram voice call could have allowed attackers to execute code on an Android phone simply by convincing the victim to answer, according to security startup NebuSec.
NebuSec disclosed the vulnerability on October 29th, saying an attacker needed only a regular Telegram account to exploit it.
The vulnerability, which went unnoticed for four years, was discovered in the code Telegram uses to manage voice and video calls.
During a call, the two devices exchange short messages to establish the connection and communicate their state.
The security company stated that it used OpenAI's GPT-5.4 model to discover the flaw.
How can a Telegram call hack a phone?
NebuSec's demonstration shows two phones, labeled as the attacker and the victim. The victim accepts an incoming Telegram call.
Roughly 30 seconds later, the victim's phone switches to its home screen, with app icons tumbling down the display before a “HACKED BY NEBUSEC” logo appears.
NebuSec explains the mechanism simply: one message type, called MediaState, carries information such as whether the microphone is muted, the camera is enabled, or how the video is oriented.
NebuSec says the code responsible for processing these messages failed to handle missing fields correctly, causing it to access unauthorized memory locations.
Attackers can sometimes exploit such memory-handling errors to execute code, although researchers have not publicly documented the precise exploit path for this specific bug.
Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
Telegram users are urged to update
The flaw does not have an assigned CVE identifier yet. According to NebuSec's co-founder and CEO, who provided details to The Hacker News, the vulnerability affects Telegram for Android versions 8.6.2 through 12.10.3.
Users should check that their Android app is running version 12.10.4 or later. The installed version can be found at the bottom of Telegram's Settings page.
Previously, Telegram users reported account takeovers that exploited outdated voicemail features.
Attackers allegedly kept the victim's phone line busy so Telegram's login call went to voicemail. The intruder then accessed the voicemail code and breached the account within about five minutes.