Europol disrupts Gootloader, two other major malware operations
6.4 million stolen credentials uncovered in international cybercrime crackdown.
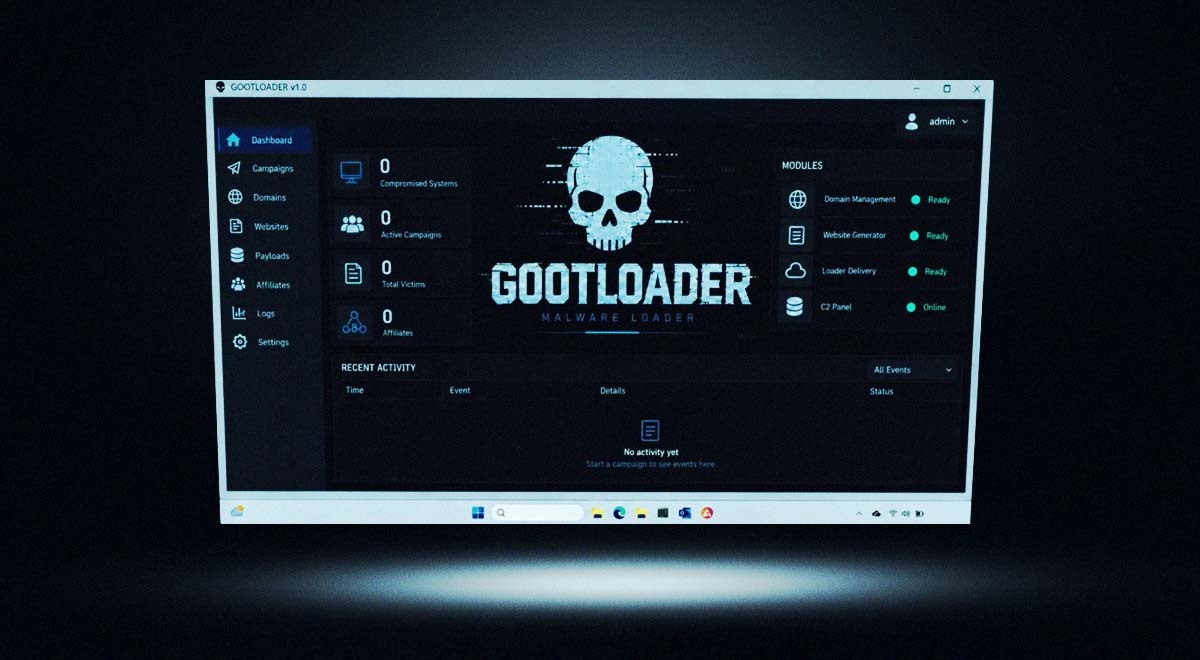
Gootloader malware. Screenshot from Europol website
 Follow us
- Europol and partners dismantled infrastructure for Gootloader, CastleRAT, and StealC malware.
- Authorities seized 235 servers and 257 domains during Operation ENDGAME.
- Investigators identified more than 6.4 million stolen login credentials linked to victims.
- WordPress site owners should update passwords, add extra login verification, and patch known flaws.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Along with law enforcement authorities from across Europe and the US, Europol has dismantled the digital infrastructure of Gootloader, CastleRAT, and StealC malware.
Authorities from Bulgaria, Canada, Denmark, Germany, Moldova, the Netherlands, Poland, the United Kingdom, and the United States seized 235 servers and 257 domains as part of Operation ENDGAME, a global initiative targeting the infrastructure used by cybercriminals.
The operation focused on three separate malicious toolkits: Gootleader, CastleRAT, and StealC.
Gootloader is a malware loader that spreads through compromised websites, often using fake legal documents to trick visitors into downloading malicious files.

The actors behind Gootloader used search engines and made suspicious websites appear at the top of search results. This was done via the infection of websites using WordPress. When people clicked on these search results, they found themselves on criminals’ websites.
Investigators took down 14 servers and 218 domains associated with the malware. They also helped clean up 681 infected websites.
CastleRAT, a remote access trojan first identified in 2025, allows attackers to control infected computers remotely. Criminals have used it to encrypt data and disrupt IT systems, forcing organizations to pay ransoms. Authorities seized 120 servers and 39 domains linked to its infrastructure.
The third toolkit, StealC, is an information-stealing malware that extracts passwords, login credentials, and digital identities from compromised devices. The stolen data is often sold or used for fraud and other cyberattacks. Investigators dismantled 102 servers associated with StealC.


Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
During the operation, investigators identified more than 6.4 million login credentials from victims. These were sold and most likely used to pull off additional ransomware attacks.
As part of the response, WordPress website owners are advised to update their login credentials, enable multi-factor authentication, and patch known vulnerabilities to reduce the risk of compromise.
Europol’s European Cybercrime Centre (EC3) supported the investigation through intelligence sharing, financial tracing and victim notifications. Eurojust coordinated judicial cooperation between participating countries.