A phantom Chinese online casino empire is quietly spreading malware
Bizarrely, many security teams ignore online gambling and casino domains, especially Chinese-language websites.
Chinese online casinos conceal malware. By Cybernews.
- Infoblox tracks 1.7 million Chinese-language casino websites tied to illegal gambling.
- Researchers say some sites hide PeckBirdy malware infrastructure used against Asian corporate and government targets.
- Attackers use fake software update pages and compromised websites to trick victims into downloading malware.
- Infoblox warns defenders not to dismiss casino or adult domains as simple browsing violations.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
The web is now full of illegal Chinese-language gambling and casino websites hiding serious malware behind their domains. Infoblox researchers say the security community should pay closer attention to these sites as they double as infrastructure for espionage and malware distribution.
In a new report, Infoblox says it’s tracking a whopping 1.7 million Chinese-language casino websites that facilitate illegal gambling. The sites then support North Korean money laundering and tax avoidance.
But some are also concealing command-and-control (C2) infrastructure, known as PeckBirdy and used by little-known China-aligned APT actors attacking corporate and government targets across Asia, researchers say.
PeckBirdy is built using JScript, an older scripting language that allows it to operate across a wide range of execution environments. According to Infoblox, in this case, the threat actors are deploying it across Chinese-language gambling sites – and adult platforms.



Our new casino research shows an expansion of the industries being targeted with these ongoing PeckBirdy APT campaigns, which are now also using low-quality Chinese-language adult websites as part of the ruse,said Infoblox in a blog post.
“We also documented a C2 domain being used by the PeckBirdy framework that had zero detections on VirusTotal at the time of this publication.”
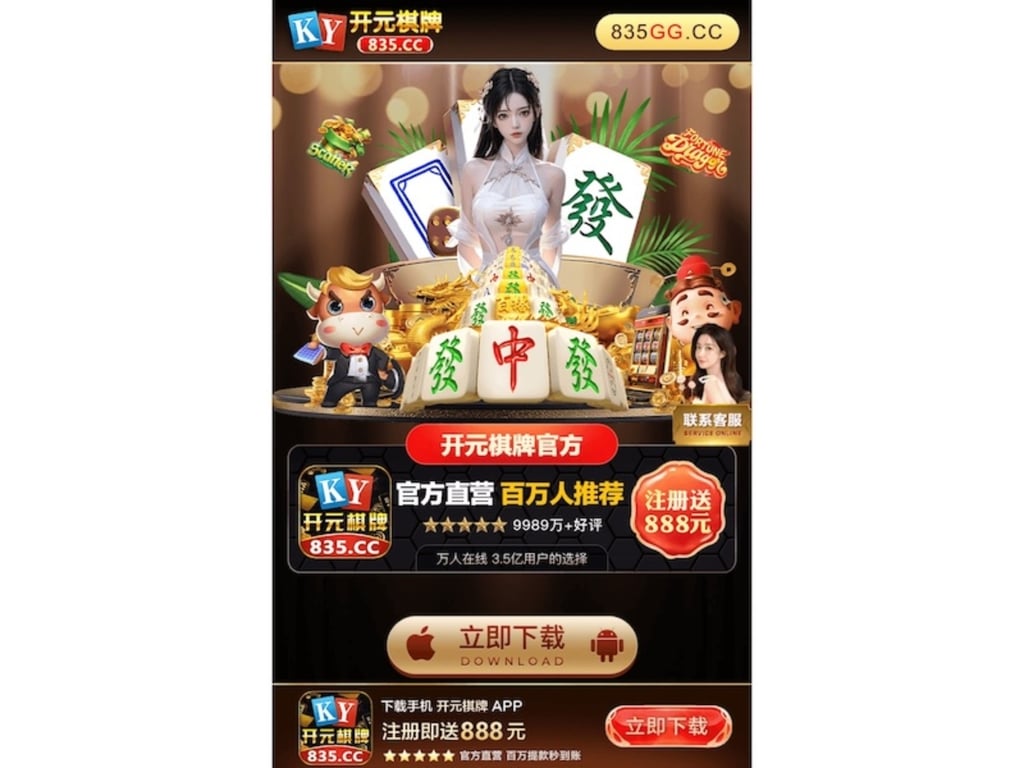
These casino sites are quite similar and operate like a legal online casino would. But even though some indeed offer real, albeit illegal, gambling and even run customer support (gambling has been banned for people in mainland China for decades), on others it’s just set dressing.
In one campaign, for example, attackers injected scripts into gambling sites that loaded PeckBirdy and displayed fake software update pages designed to entice victims to download malware.
In other documented cases, PeckBirdy links were embedded into compromised government websites or executed via MSHTA, a Windows-native binary designed to execute Microsoft HTML Application script code.
What deepens the issue is that some of these sites rely on US cloud providers such as Amazon, Microsoft, Cloudflare, and Google for computing infrastructure, creating a huge cybersecurity headache.
Has your password leaked?
One likely explanation is account theft at those providers, a practice documented previously as “infrastructure laundering,” Infoblox said.
Presenting this particular research, the company’s staff threat researcher Zach Edwards explained: “This is basically my pièce de résistance to help people understand the scope of illegal online casinos and how serious threat actors are running roughshod over defenders in the US and around the world.”
Infoblox defenders advise to stop ignoring casino domains.
“An alert on a Chinese-language casino or adult domain that gets closed as an employee browsing violation is precisely the outcome the PeckBirdy operators are counting on. The decoy works because the dismissal is reasonable – these domains genuinely are, most of the time, exactly what they appear to be,” said the researchers.