Ubiquiti patches high-severity security bugs in its security appliance AI Key
Ubiquiti urges to update UniFi Protect AI Key devices.
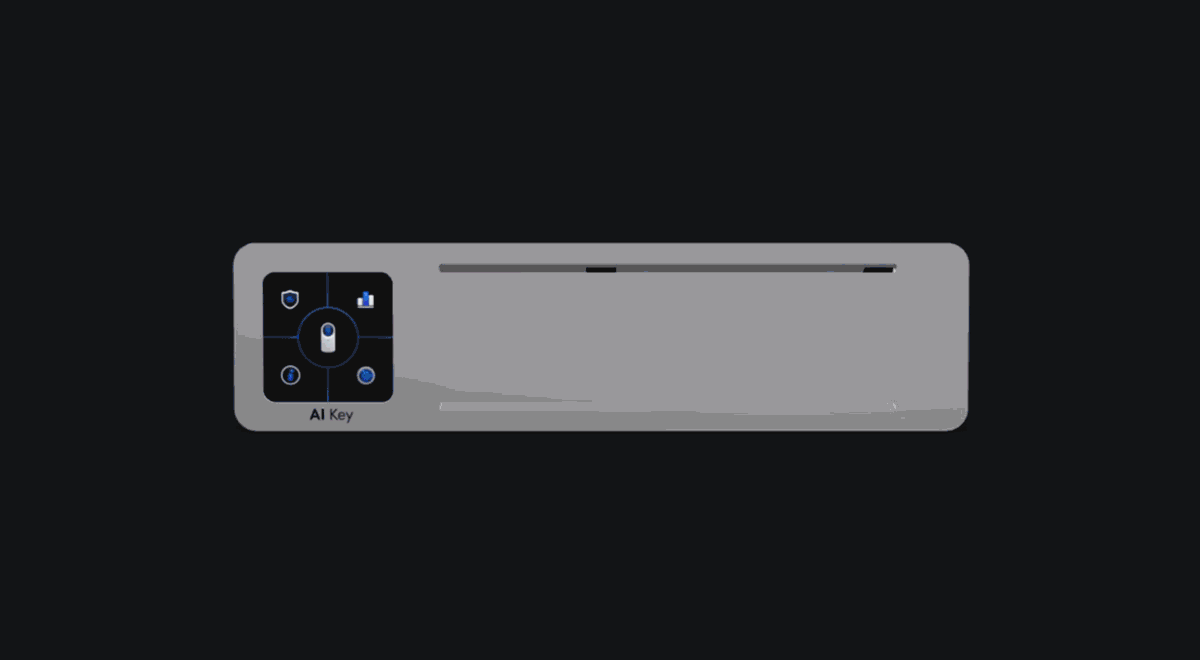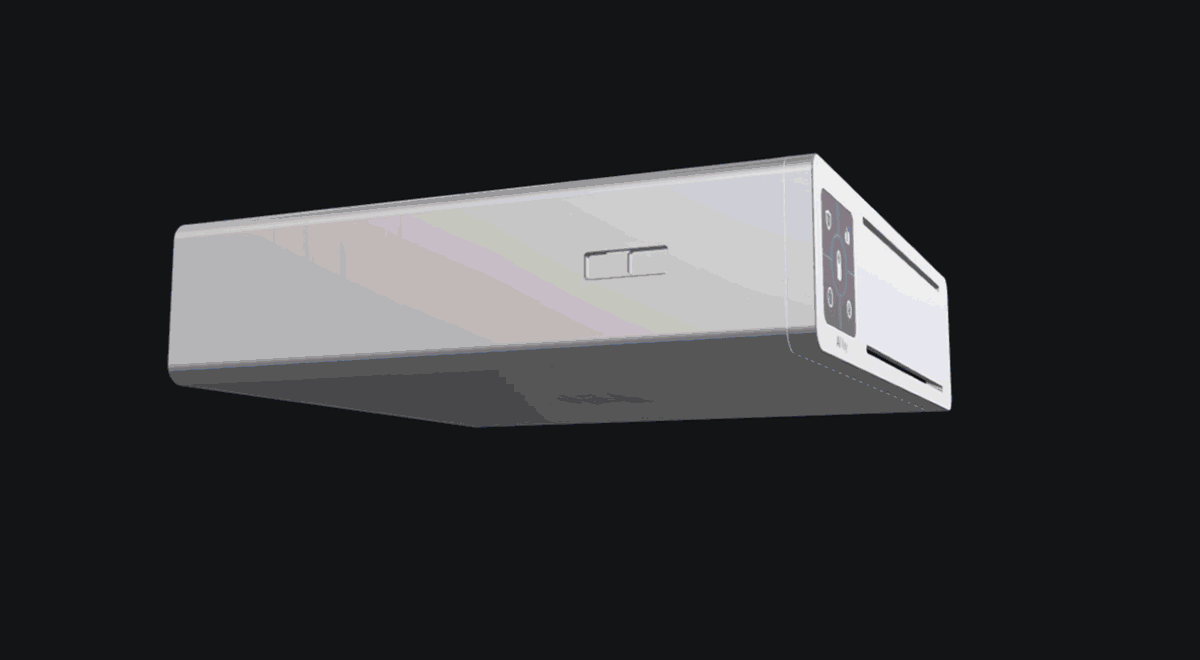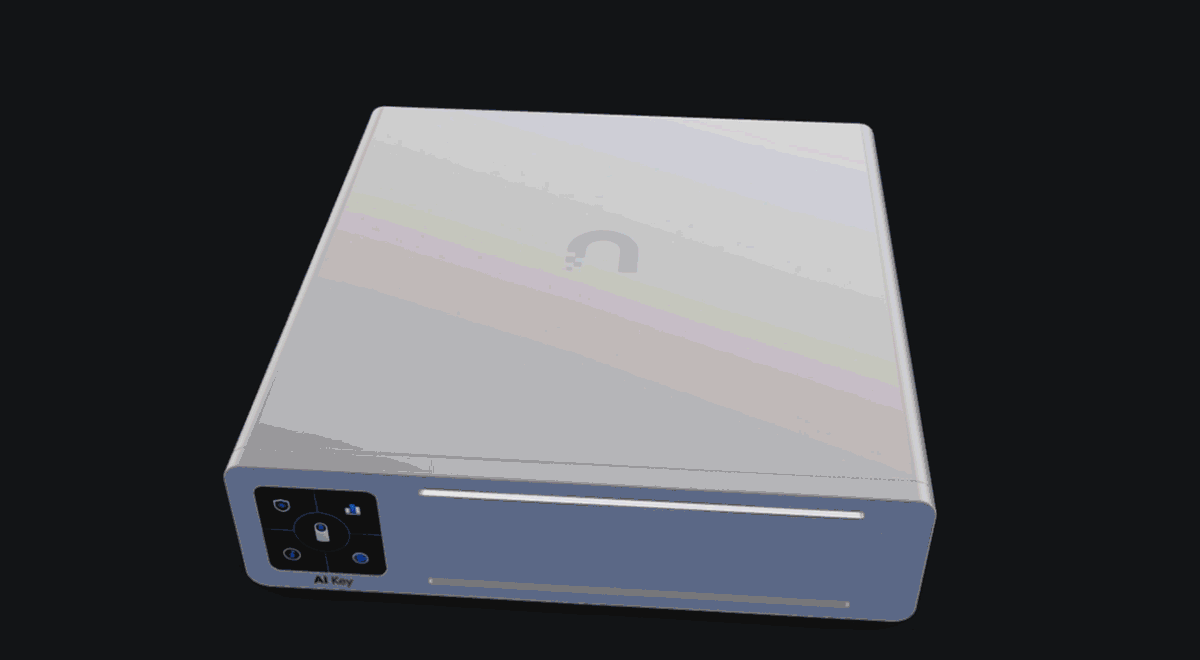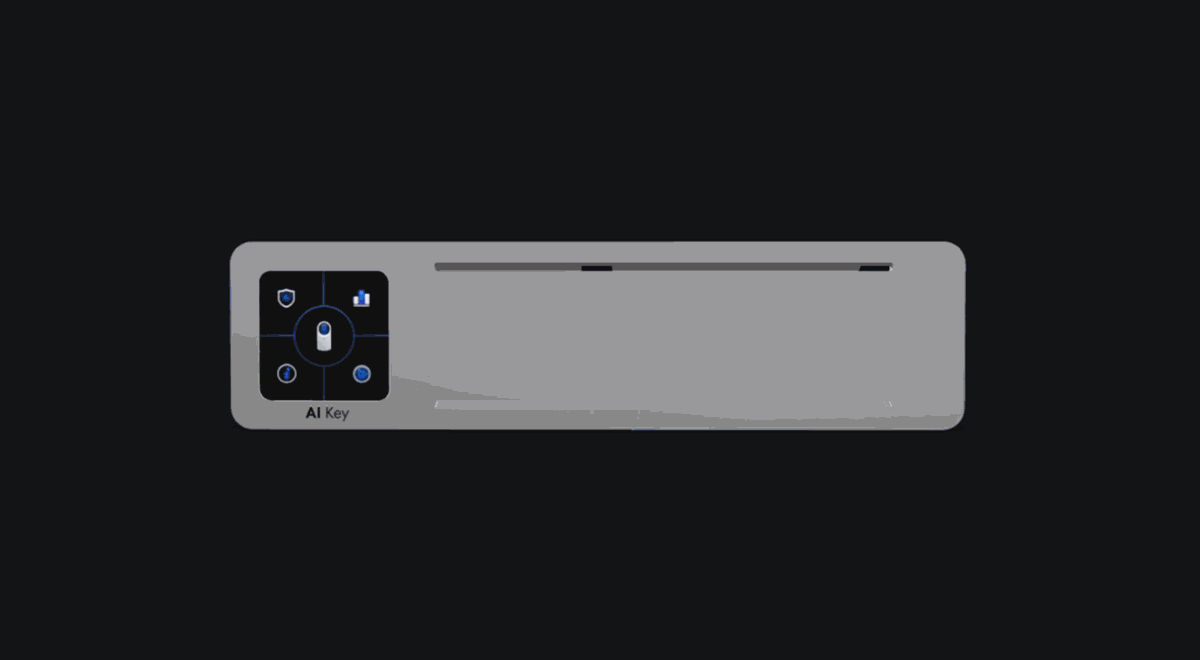
Ubiquiti AI Key device. Image by Cybernews / Ubiquiti.
 Follow us
- Ubiquiti fixed 6 vulnerabilities in its AI Key video surveillance appliance.
- Attackers on the same network could inject commands, disrupt devices, or access sensitive information.
- The most serious flaw needs no login or user action and has low attack complexity.
- Ubiquiti urges AI Key users on version 2.2.6 or earlier to update to 2.2.8.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Ubiquiti, an American technology company that manufactures networking products, has disclosed 6 vulnerabilities affecting its video surveillance appliance AI Key. Attackers on the same network can inject commands, disrupt or compromise the device, and access sensitive information.
UniFi Protect AI Key is a physical device that adds AI-driven threat detection and alerting to UniFi Protect, the company’s enterprise-grade video surveillance and physical security system.
The appliance searches footage, recognizes faces or license plates, and can analyze up to 1,800 smart detection events per hour.
Ubiquiti has addressed 6 security vulnerabilities currently affecting the device.
The most serious bug is an improper access control vulnerability, rated 8.6 out of 10 on the severity score. Malicious attackers with access to the network can leverage it “to obtain information, make unauthorized changes, and execute a Denial of Service (DoS) attack on the device.”
No privileges or user interaction are required, and the attack complexity is low.
Another high-severity (8.1 out of 10) input validation vulnerability allows threat actors, under certain conditions, to inject commands into the vulnerable device, Ubiquiti’s new advisory reads.

Check if your data was exposed
Find out if your email and related personal information have appeared in known data breaches.
Four other vulnerabilities are less severe. Two medium-severity bugs expose internal resources through the device. Two low-severity path traversal flaws allow attackers to create or truncate files on the device, or obtain information about existing files.
The vulnerabilities can be chained together to potentially pull off a more damaging attack. Ubiquiti credited the discoveries to security researcher Andy Gill of ZephrSec Ltd.
The advisory doesn’t mention whether these bugs have been exploited in real-world attacks.
All the vulnerabilities affect AI Key devices running version 2.2.6 or earlier. Ubiquiti urges users to update their devices to the latest version, currently 2.2.8, released 24 days ago.