Millions of Android phones face massive hacking risk: zero-click critical flaw
Google’s November patch fixes dozens of critical vulnerabilities – millions of unpatched older Android devices are exposed to remote exploitation.
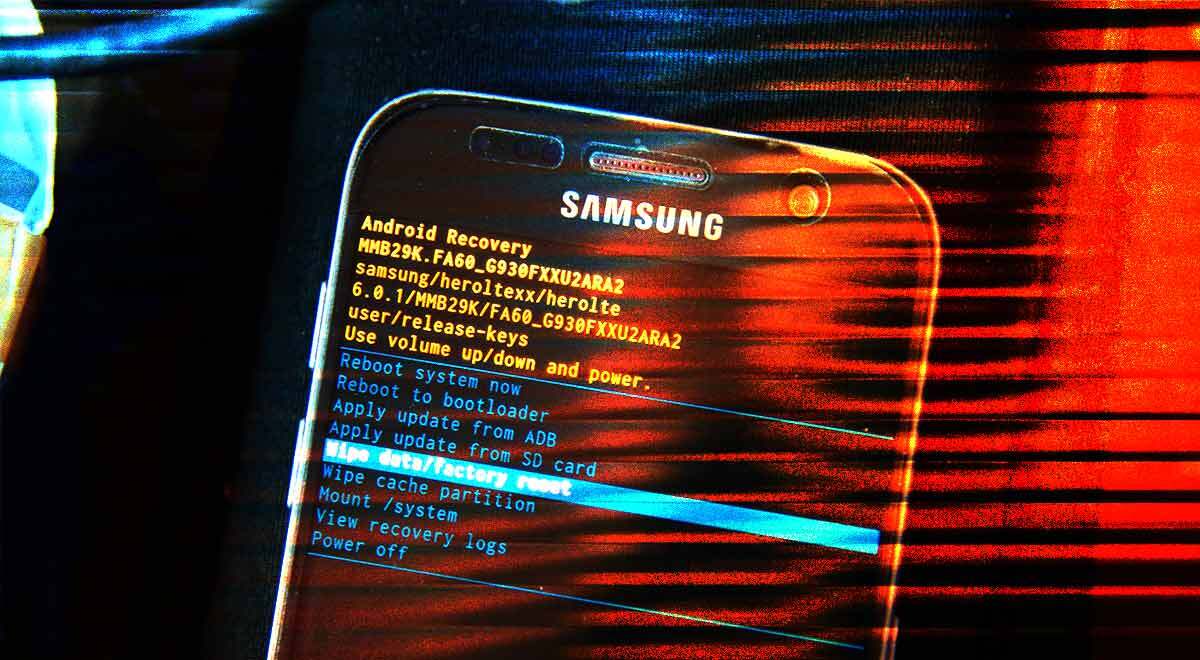
Android recovery mode. Image by Cybernews / Shutterstock / rukawajung.
 Follow us
- Google fixed a critical Android flaw that could let attackers take over phones without a tap.
- The flaw affects supported Android versions 14 through 17, and older versions may also be vulnerable.
- 43.6% of active Android devices run unsupported versions and will not receive the fix.
- The November update fixes 216 flaws, including bugs that can crash calls or give attackers higher access.
Google has fixed a critical Android security flaw that could allow hackers to take over a phone without the user clicking or approving anything. The most severe bug lies in media-processing code that generates preview images. Nearly half of active Android devices will never receive the patch.
The November 2026 Android Security Bulletin warns of a critical remote code execution vulnerability that hackers can exploit without users noticing anything.
“The most severe of these issues is a critical security vulnerability in the Framework component that could lead to remote code execution with no additional execution privileges needed. User interaction is not needed for exploitation,” the advisory reads.
The highlighted flaw affects all supported Android versions 14 through 17. The advisory doesn’t say whether older end-of-life (EOL) Android releases are vulnerable, but it's possible, given that the vulnerable component dates back to 2017.
All users are advised to update their devices to the latest security patch level of 2026-11-01 or later.
Android is the most popular mobile operating system with a user base nearing 4 billion, according to various estimates.


Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
Android’s distribution data shows that 43.6% of active devices still run Android 13 or older – security support for them has ended, and they don’t receive new fixes.
For newer Android devices, each manufacturer has to build and ship the patch. In the best case, it only carries a delay. But many budget phones that passed their promised update window might also never get the November patch.
Memory corruption bug lies in media-handling code
Zero-click doesn’t automatically mean that attackers can reach every device over the internet.
Google describes the most severe flaw as a heap buffer overflow, causing an out-of-bounds write – such bugs often cause crashes, but under certain conditions could allow an attacker to run arbitrary code. The bug is tracked as CVE-2026-58868.
The vulnerable code lies in Android’s framework component responsible for handling media playback. The advisory specifies a vulnerable function in the FrameDecoder.cpp file, a part of Android that creates preview images, such as video and photo thumbnails.
Such code may be involved in routine media-processing operations, such as generating thumbnails for received or downloaded media files.
“In onOutputReceived of FrameDecoder.cpp, there is a possible out-of-bounds write due to a heap buffer overflow. This could lead to remote code execution with no additional execution privileges needed. User interaction is not needed for exploitation,” reads the advisory.
The vulnerable component carries a 2017 copyright header, suggesting that the code is nearly a decade old. However, it remains unclear when the flaw was first introduced.
No public proof-of-concept exploit is currently available, and Google hasn’t confirmed any active exploitation in the wild.
However, AI-assisted attackers can relatively quickly reverse-engineer the patches once the source code is publicly released 48 hours after the bulletin's initial publication.
Check if your data was exposed
Find out if your email and related personal information have appeared in known data breaches.
The update addresses 216 vulnerabilities
The Android security update addresses 23 critical vulnerabilities and 193 less severe bugs in total.
It brings a fix for a critical “SMS of Death” vulnerability, which enables attackers to crash Android’s phone service, drop active calls, including emergency calls, and potentially cause a reboot loop.
Two critical severity system vulnerabilities, CVE-2026-58876 and CVE-2026-58936, both rated 9.8 out of 10 on the severity scale, could lead to remote code execution without requiring additional execution privileges or user interaction.
Several critical vulnerabilities that enable malicious code to elevate privileges were identified in kernel components. Google also included critical fixes for MediaTek and Qualcomm components.