Ukraine warns hackers are exploiting China-made Dahua cameras
Surveillance feeds could be used to monitor military movements and critical infrastructure.
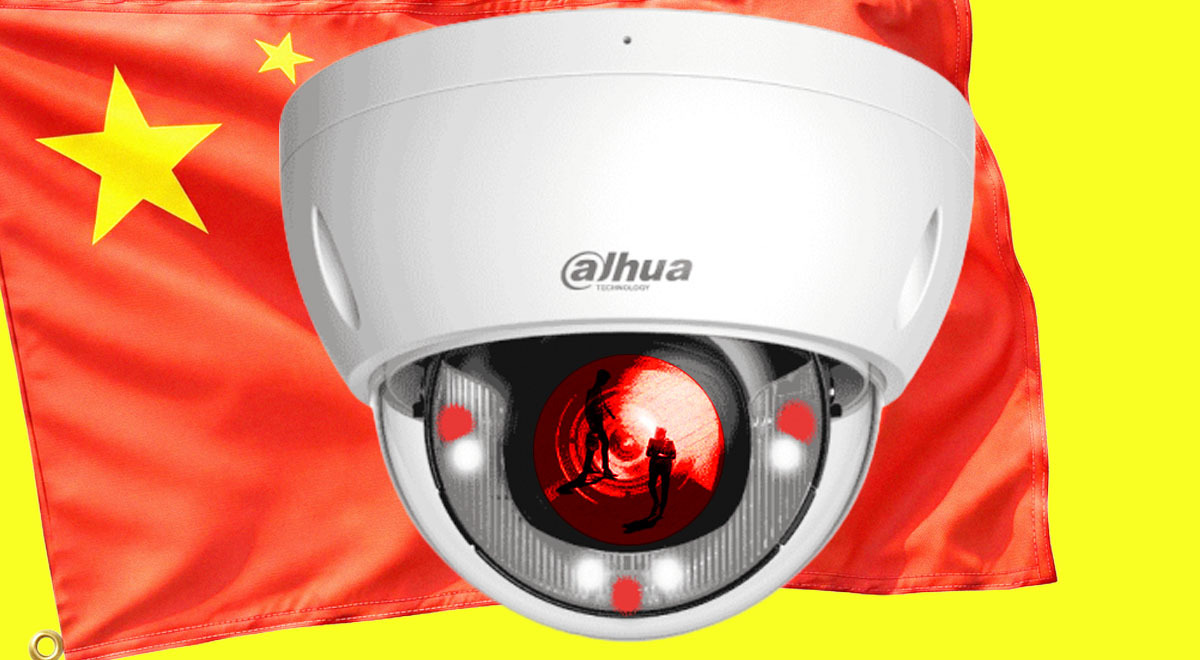
Ukraine warns over Chinese-made Dahua cameras. By Cybernews.
 Follow us
- Ukrainian CERT says hackers compromised some Dahua cameras and recorders, changed settings, and created unauthorized accounts.
- Officials fear exposed camera feeds could help Russian intelligence track troops and critical infrastructure.
- CERT-UA says Dahua’s Easy4IP feature may let attackers find devices by guessing predictable serial numbers.
- Weak passwords and outdated firmware can increase the risk, especially on devices with known critical flaws.
Key Takeaways by nexos.ai, reviewed by Cybernews staff.
Hackers are gaining access to surveillance cameras produced by the Chinese manufacturer Dahua, potentially exposing video feeds and allowing them to remotely control the devices, Ukrainian government cybersecurity researchers have warned.
CERT-UA, Ukraine’s computer emergency response team, said it had identified cases when hackers compromised the smart cameras and video recorders, changed their settings, and created unauthorized user accounts.
It’s unclear how many cameras were compromised, when the attacks occurred, or who was responsible. But Chinese surveillance equipment is widely used in Ukraine, including its military.
In Kyiv, officials are worried these devices could be exploited by Russian intelligence services to monitor military movements and critical infrastructure. Ukraine has been at war with Russia since early 2022.
Cases of compromising IP cameras and DVRs with access to the video stream, changing the device configuration and creating third-party accounts have been recorded,CERT-UA said in a press release.
According to the researchers, the attackers appear to be exploiting a feature called Easy4IP, which allows users to access Dahua cameras remotely through the manufacturer’s cloud service.
Predictable patterns
Easy4IP connects devices to the cloud using their serial numbers, even when the devices are protected by firewalls or cannot be accessed directly over the web.
But CERT-UA said the serial numbers actually follow predictable patterns. This has apparently allowed the hackers to guess a large number of them and identify cameras connected to the cloud.
“Serial numbers have a predictable structure and are likely obtained by attackers through brute force and subsequent verification of the presence of the corresponding device in the cloud,” said CERT-UA.
Stay updated with our latest stories and follow us on social media
Be the first to discover new stories, ideas, and updates from our team.
“Therefore, all devices with active Easy4IP functionality are at risk. The assumption that the serial number is unknown to anyone is not a reason to consider the device secure.”
Once a device is identified, attackers can attempt to gain access by guessing weak or default passwords or exploiting security flaws in outdated firmware that allow them to bypass authentication.
Specifically, CERT-UA warns about 2 critical vulnerabilities, CVE-2021-33044 and CVE-2021-33045, disclosed in 2021, that affect certain Dahua cameras and video recorders.
Has your password leaked?
In 2024, the US Cybersecurity and Infrastructure Security Agency issued a warning about these critical flaws, stating that Dahua IP cameras and related products contain authentication-bypass vulnerabilities.
Dahua is one of China’s largest manufacturers of video surveillance equipment, but it has faced restrictions in the US and elsewhere over national security and human rights concerns.