Latrodectus malware detected on over 44,000 IP addresses
Over 44,000 IP addresses were infected with dangerous Latrodectus malware, which is used to deploy banking trojans, before a law enforcement takedown during this month's Operation Endgame, new data reveals.

Image by Cybernews.
 Follow us
Over 44,000 IP addresses were infected with dangerous Latrodectus malware, which is used to deploy banking trojans, before a law enforcement takedown during this month's Operation Endgame, new data reveals.
Latrodectus is a Windows malware downloader that hackers have used to download and execute other payloads and modules since at least 2023. This threat is commonly distributed with malicious emails.
Threat actors have been using Latrodectus to deliver IcedID, a modular banking malware that steals financial information, QakBot, another modular banking trojan. There are also overlaps with Pikabot, a backdoor used for initial access, and other malware.
Just two weeks ago, over 44,000 IPs were running Latrodectus malware, and, likely, some other malicious software.
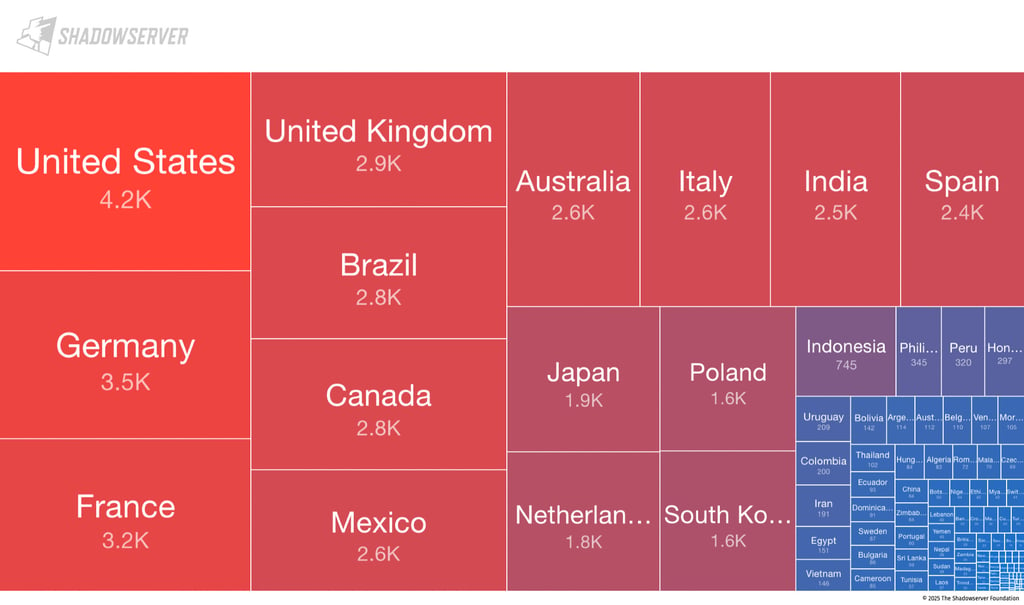
The Shadowserver Foundation, a nonprofit security organization, has shared a special report on its tracking of the infected machines between April 26th and May 20th, 2025.

Most of the infected devices were detected in the US (4,200), followed by Germany (3,500), France (3,200), the United Kingdom (2,900), and Brazil (2,800). Over 2,000 infected hosts were detected in Canada, Mexico, Australia, Italy, India, and Spain.
Cybernews reported on May 23rd that Europol, accompanied by other international authorities, dealt a massive blow to several malware families, seizing 300 servers worldwide, taking down 650 domains, and issuing arrest warrants against 20 cybercriminals.
Europol said it neutralized Latrodectus, among other malware strains such as Bumblebee, Qakbot, Hijackloader, DanaBot, Trickbot, Warmcookie, and others.
The detected 44,000 infected IPs may still be dangerous, running malicious packages. ShadowServer shares the report with internet service providers, network owners, and other organizations, which helps to clean up infected devices.
“The data in this IcedID/Latrodectus Historical Bot Infections Special Report was provided to Shadowserver by the Operation Endgame Law Enforcement partners to disseminate to National CERTs/CSIRTs and network owners globally, to maximize remediation efforts,” Shadowserver explains.
“This special report has severity level CRITICAL set on all events.”
We have shared a Special Report on IPs infected with Latrodectus malware during 2025-04-26 to 2025-05-20. This is one of the results of the continued international Law Enforcement action called Operation Endgame Season 2.0 Over 44K infected IPs seen: dashboard.shadowserver.org/statistics/c...
undefined The Shadowserver Foundation (@shadowserver.bsky.social) May 29, 2025 at 5:48 PM
[image or embed]
Latrodectus is an advanced malware with sandbox evasion capabilities, making it harder to detect in testing environments. It communicates with command-and-control servers to send system information and receive commands. It uses HTTP POST requests to communicate with the operator, the data is encrypted with RC4 and encoded in base64, explains a report by Proofpoint.
Operation Endgame is an ongoing, long-term oriented, large-scale operation conducted jointly by law enforcement agencies around the world. It's directed against services and infrastructures assisting in or directly providing initial or consolidating access for ransomware.